

Microsoft has announced a significant update to its identity platform, Microsoft Entra ID, with the introduction of expanded passkey (FIDO2) support in public preview.
Set to roll out globally from mid-October to mid-November 2025, this enhancement marks a major step in Microsoft’s ongoing push toward passwordless authentication and improved enterprise security, as per a report by .
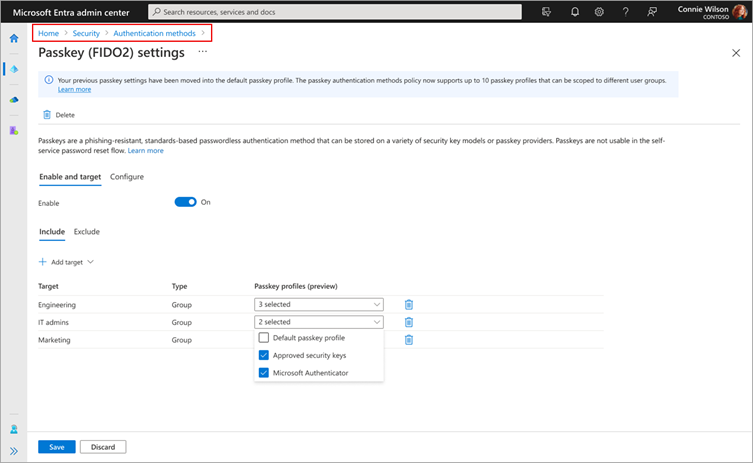
What’s New: Group-Based Passkey Profiles
The upcoming update will allow IT administrators to configure passkey authentication policies at a granular, group-based level.
This means organizations can tailor which user groups are permitted to use specific FIDO2 security key models or leverage passkeys stored in Microsoft Authenticator, providing unprecedented flexibility and control over authentication methods.
For example, one department could be restricted to using only company-issued hardware keys, while another could use device-bound passkeys on mobile devices.
These new settings will be accessible via the Microsoft 365 admin center under Security > Authentication methods > Passkey (FIDO2) settings.
The update also introduces changes to the API schema, enabling more advanced configurations and integrations for organizations that manage authentication through Microsoft Graph API or third-party tools.
Expanded Device and Platform Support
Microsoft Entra ID’s passkey support now extends across Windows, macOS, Android, and iOS, covering both web and native applications.
Notably, device-bound passkeys can be stored securely in the Microsoft Authenticator app on iOS and Android, catering to organizations with strict security requirements.
This approach ensures private keys remain on managed devices, reducing risk if a device is lost or compromised.
Additionally, with the new update, Microsoft Entra ID will accept any WebAuthn-compliant security key or passkey provider when attestation enforcement is disabled.
This broadens compatibility and allows organizations to use a wider range of security keys and passkey providers for registration and authentication.
The rollout will be automatic, requiring no immediate action from administrators.
However, organizations are encouraged to review their current passkey configurations, notify IT staff of the changes, and update internal documentation to reflect the new capabilities.
During the public preview, any modifications made via the Microsoft Azure or Entra portal will adopt the new schema, while changes through Graph API or third-party tools will retain the existing schema until general availability.
End users will notice updates in the sign-in experience, with the term “passkey” now encompassing credentials from hardware keys, computers, and mobile devices. This unification simplifies the authentication process and aligns with Microsoft’s broader strategy to phase out traditional passwords in favor of more secure, phishing-resistant methods.
Microsoft’s expansion of passkey support in Entra ID is part of a broader industry shift toward passwordless authentication, aiming to enhance security and user experience.
The company has signaled ongoing investments in both device-bound and, eventually, synced passkeys for enterprise accounts.
For more details and guidance on enabling passkeys in your organization, Microsoft will update its official documentation ahead of the rollout.
Organizations can prepare by exploring the new features in preview and planning for a future where passwords are no longer the weakest link in enterprise security.
Find this News Interesting! Follow us on Google News, LinkedIn, and X to Get Instant Updates





 support in public preview.)