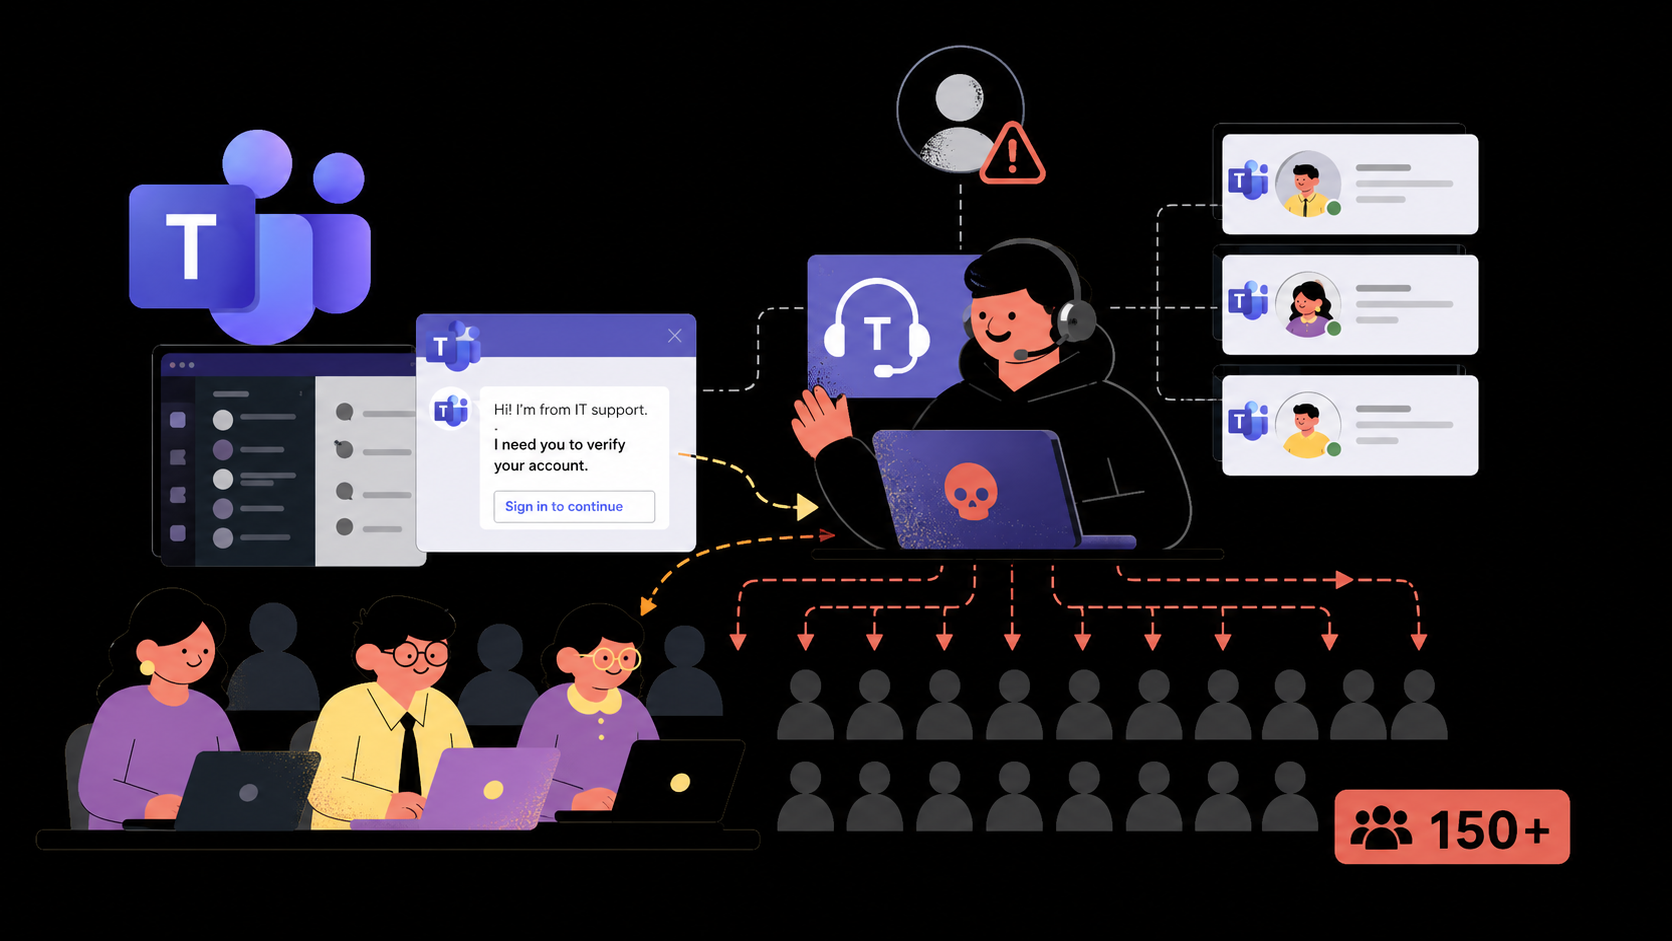

A coordinated social-engineering campaign dubbed Spring Ring used external Microsoft Teams accounts to impersonate corporate IT help desk staff and target more than 150 employees across at least 10 organizations between January and April 2026.
The operation demonstrates how attackers are shifting phishing activity from email into trusted collaboration platforms, using live voice calls to persuade employees to run remote-access tools or malware.
The accounts were hosted on adversary-controlled .onmicrosoft[.]com tenants whose names included corporate-sounding terms such as “internal,” “network,” “certified,” and “infrastructure.”
Unit 42 stressed that the activity did not result from a vulnerability or compromise in Microsoft Teams itself.
The attack begins with an unsolicited Teams chat request. Once the target accepts or engages, the impersonator quickly places a voice call and claims to be addressing an urgent technical problem.
This vishing component is central to the operation. Rather than relying only on a malicious link or credential-harvesting page, the attacker uses real-time conversation to overcome suspicion and adapt the lure to the victim’s responses.
Attackers made repeated call attempts, sometimes leaving voicemails and cycling through multiple employees. Unsuccessful calls frequently lasted seconds, while engagements that progressed further often continued for 10 to 15 minutes.
The campaign’s scale and persistence underline the growing abuse of external collaboration features as an initial-access channel.
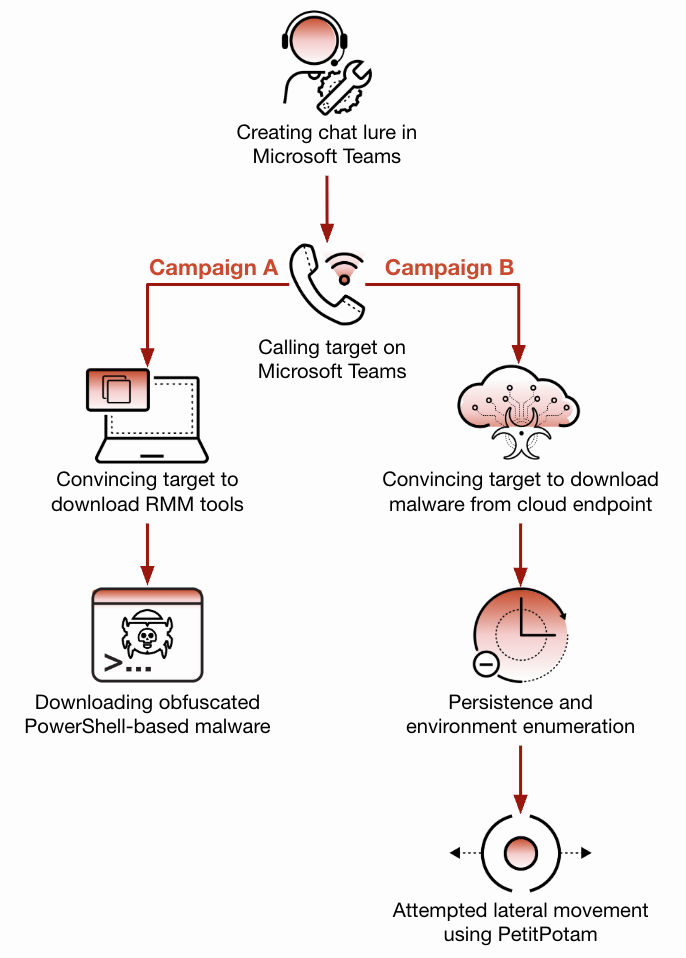
Unit 42 observed two distinct payload-delivery chains following the Teams vishing lure.
In the first campaign, the fake technician persuaded employees to launch Windows Quick Assist or install legitimate remote monitoring and management tools.
Once granted remote control, the operator ran reconnaissance commands including whoami /groups and net group /dom to identify the compromised system and domain environment.
The actor then used PowerShell to retrieve an obfuscated remote-access Trojan from san-sid[.]com.
Researchers at Palo Alto Networks Unit 42 said that, the attackers created external Microsoft 365 identities designed to resemble internal support functions, using urgent and professional display names such as “IT Help Desk,” “IT Assistance,” and “Support Staff.”
Researchers found the concealed script attempted to disable the Antimalware Scan Interface through the amsiInitFailed flag, validate the bypass, collect host information, and contact command-and-control infrastructure for additional payloads.
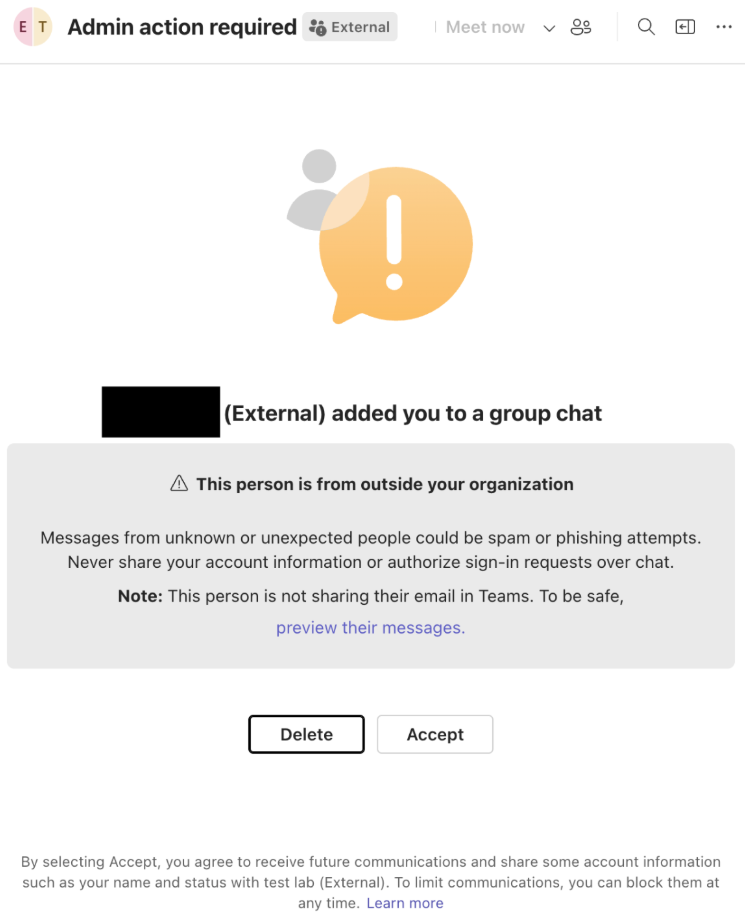
Cortex XDR protections blocked the malware during execution.
Microsoft Teams IT Support Scam
Victims were directed to cloud-hosted executables named to match both the target organization and the individual recipient, increasing the appearance of legitimacy.
After execution, the malware copied itself into the Temp directory, created additional executable copies for persistence, and launched a hidden Microsoft Edge instance to sideload a browser extension.
The chain then used Python from C:\ProgramData\IntegrityData\python.exe to scan internal systems over SMB on TCP port 445 and trigger NTLM authentication activity against the organization’s domain controller.
The attackers subsequently attempted to use PetitPotam to coerce the domain controller into authenticating to attacker-controlled infrastructure, enabling an NTLM relay attempt that could have escalated to domain-level privileges.
The attempted takeover was blocked by Unit 42 Managed Detection and Response.
The Spring Ring activity reflects a wider trust problem in SaaS communications.
Employees may scrutinize external email banners, suspicious sender domains, and embedded links, but a Teams call from an apparent help desk contact can appear routine particularly when the caller uses technical language and creates urgency.
Unit 42 reported that collaboration-tool phishing alerts accounted for 42% of all Cortex phishing alerts during the first four months of 2026, up from 30% in the preceding four-month period.
The firm also cited KnowBe4 data showing a 41% increase in Teams-based attacks between October 2025 and March 2026.
Defenders should treat an external Teams chat that rapidly turns into an unsolicited voice call as a high-risk identity signal.
Other indicators include external tenants impersonating IT departments, multiple short calls from the same identity, unexpected RMM deployment, personalized cloud-hosted executables, unusual Edge extension activity, and EFSRPC or NTLM traffic involving domain controllers.
Organizations should restrict or tightly govern external Teams communication where business requirements allow, establish a mandatory callback-verification process for IT support requests, and prohibit help desk personnel from asking users to install remote-access software through unsolicited calls.
Monitoring for SMB scanning, forced authentication, and relay behavior is also essential.
For environments using NTLM, Microsoft recommends protections including SMB signing and Extended Protection for Authentication.
Alongside reducing or disabling NTLM where operationally feasible particularly around Active Directory Certificate Services and domain infrastructure vulnerable to relay scenarios.
★ Which Security Tools Should You Cut? Score Them on One Page – Download the Inherited Security Stack Guide




