
Storm-2945, a Midnight Blizzard subcluster, has resumed CaptiveCrunch, an espionage campaign abusing hospitality Wi-Fi networks to infect travelers and compromise corporate accounts.
An October 5, 2026 update confirms renewed activity observed on September 29, including deployment of a Rust variant of the CornFlake infostealer, with characteristics consistent with continued AI-enabled malware development.
The resurgence likely reflects persistent access to upstream hospitality managed service providers rather than isolated hotel compromises.
Microsoft’s assessment aligns with Black Lotus Labs research, which assessed with moderate confidence that attackers compromised several providers before exploiting downstream customer relationships.
That investigation identified approximately 70 affected IP addresses associated with three North American providers. These providers serve seven of the ten largest American hotel chains.
CaptiveCrunch manipulates DNS and HTTP traffic on networks using captive portals, redirecting selected travelers to attacker-controlled infrastructure.
Microsoft has tracked this activity since early May 2026, although the initial compromise vector remains under investigation.
Shared equipment and management systems across affected venues suggest access within the broader captive portal ecosystem.
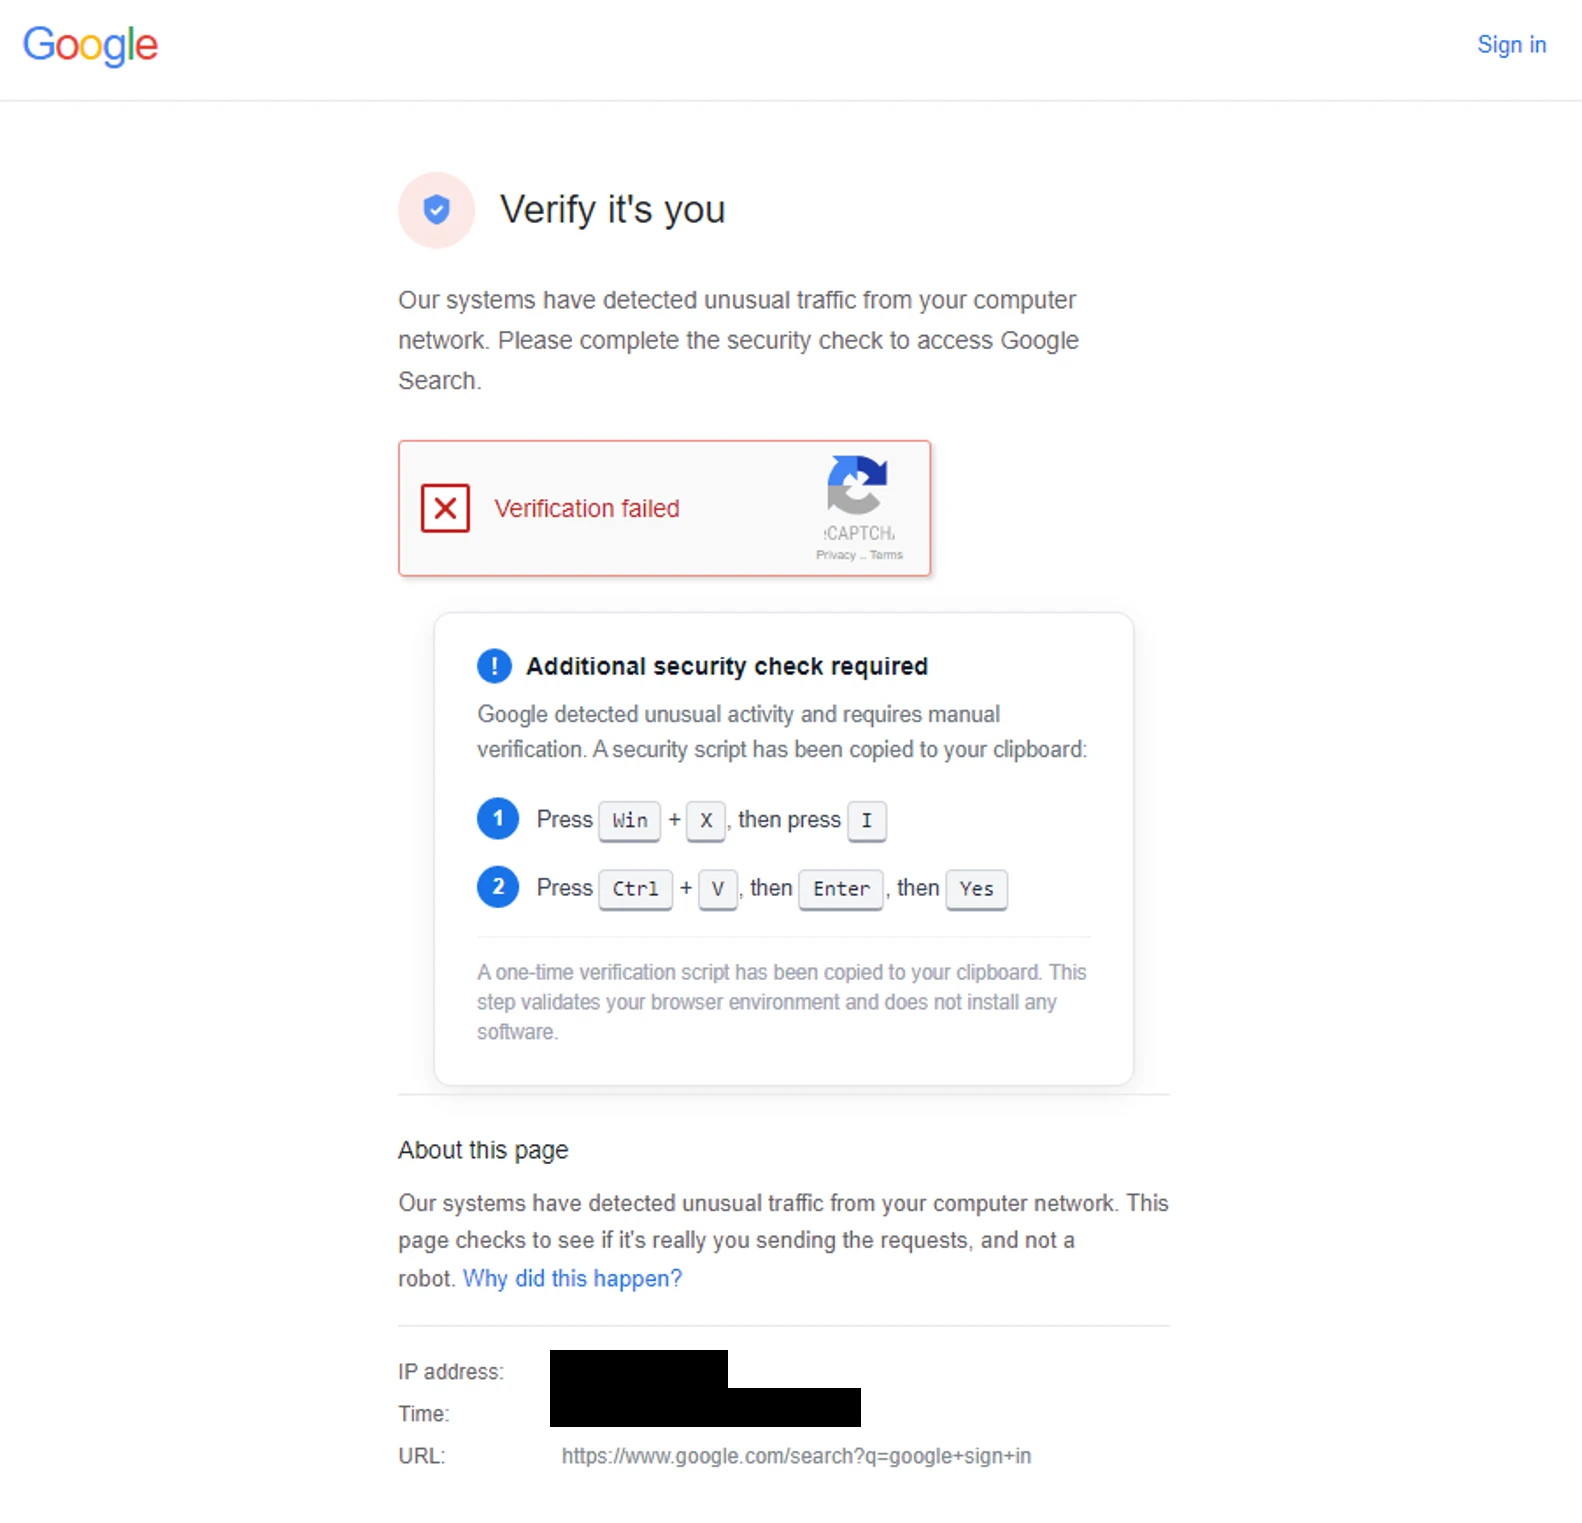
Attackers exploit automated browser connectivity checks to display fraudulent browser updates, operating system updates, and network repair prompts.
ClickFix-style instructions then persuade victims to download or execute malicious payloads. Some landing pages also instruct Android users to install APK files, indicating possible mobile targeting rather than confirmed deployment across Android devices.
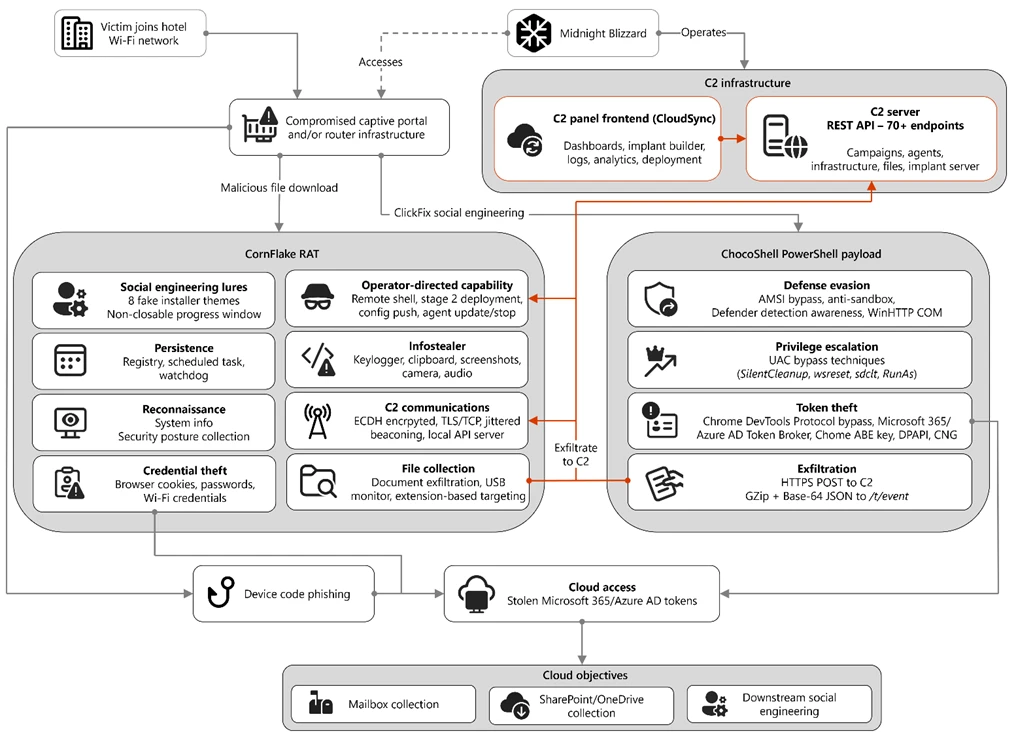
Microsoft attributes Storm-2945, to Midnight Blizzard through technical and operational overlaps, including device code phishing, Microsoft Graph email collection, and similar victim targeting.
Midnight Blizzard is attributed by American and British authorities to Russia’s Foreign Intelligence Service, the SVR.
Midnight Blizzard subcluster
The previously documented Go-based CornFlake implant displays a deceptive installation window while copying itself to %APPDATA%\svchost32\svchost32.exe.
It masquerades as “Cloud Sync Service” and maintains persistence through service registration, Registry Run keys, scheduled tasks, and a watchdog that restores removed mechanisms.
Its command-and-control channel uses ephemeral ECDH P-256 key exchange and SHA-256 session-key derivation.
A runtime configuration file, sync.dat, permits changes to servers, collection targets, and TLS settings without redeployment.
Collection capabilities include keylogging, clipboard monitoring, screenshots, microphone recording, webcam capture, browser credential theft, file exfiltration, and remote command execution.
The accompanying ChocoShell PowerShell infostealer runs in memory and harvests browser cookies, saved passwords, Microsoft 365 tokens, and Wi-Fi credentials.
It combines AMSI tampering, elevation techniques, browser debugging interfaces, and token impersonation to access protected data.
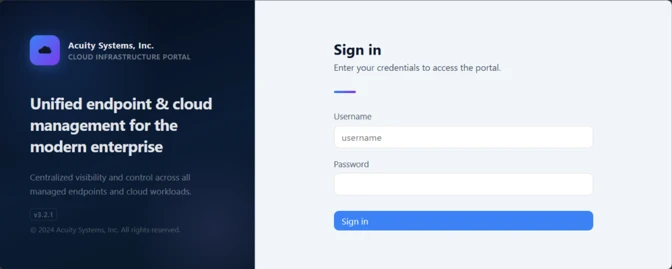
FruitStone, the campaign’s operator console, centralizes implant management, payload building, collection tasking, and infrastructure rotation.
Separate CaptiveCrunch landing pages abuse Microsoft Entra device code authentication. Victims enter attacker-generated codes on legitimate Microsoft sign-in pages, authorizing the attacker’s session instead of their own.
This extends techniques documented in Microsoft’s Storm-2372 investigation.
Microsoft’s updated hunting guidance identifies cdn-gstat[.]com, sslcdnhost[.]com, network-privacy[.]com, 154.29.75[.]245, and 149.3.170[.]186 as recent infrastructure.
Defenders should correlate connectivity with suspicious downloads, persistence changes, and anomalous device code authentication.
Microsoft recommends private connectivity where practical, rejecting portal-delivered software updates, and blocking device code flow unless explicitly required.
Its hunting queries also correlate executable or archive creation within two minutes of connectivity checks, although matches require validation and do not independently establish compromise or attribute activity to Storm-2945.
Indicators of compromise
| Indicator | Type | Description | First seen |
| cdn-gstat[.]com | Domain | CaptiveCrunch redirect | 2026-09-30 |
| Sslcdnhost[.]com | Domain | CaptiveCrunch redirect | 2026-09-30 |
| 154.29.75[.]245 | IP address | CaptiveCrunch infrastructure | 2026-09-29 |
| network-privacy[.]com | Domain | CaptiveCrunch redirect | 2026-10-01 |
Note: IP addresses and domains are intentionally defanged (e.g., [.]) to prevent accidental resolution or hyperlinking. Re-fang only within controlled threat intelligence platforms such as MISP, VirusTotal, or your SIEM.
Stops Cyber threats before impact with 21 min faster MTTR. Integrate ANYRUN’s Sandbox in your SOC.


