
Iran-linked threat actor Mirage Kitten is targeting software developers with fake recruitment assessments that hide two newly identified cross-platform remote access trojans: NodeRabbit and PollCat.
The campaign uses recruiter impersonation on LinkedIn and other job-search platforms, weaponized Node.js projects, and cloud-hosted ZIP archives to gain covert access to developer endpoints across Windows, Linux, and macOS.
Telemetry linked the activity to fintech, aviation, and aerospace targets across the Middle East and Africa, while malicious project archives were also submitted to public scanning services from India, Türkiye, Israel, Iraq, Germany, and Ireland.
The infection chain begins with a fake recruiter offering a technical role and sending a time-sensitive coding challenge. One archive, Front-Technical-Challenge.zip, presented a legitimate-looking TaskFlow application built with Express, React, and Vite.
Its README told candidates to fix front-end defects while explicitly claiming that server.js was safe and should not be changed directing scrutiny away from the tampered file.
The malicious server.js imported colorized_terminal version 2.1.0, a trojanized package bundled locally in node_modules rather than downloaded from npm.
When the victim ran the project, the package launched a concealed NodeRabbit payload from node_modules/.cache/.320697f1/index.js as a detached process. Other samples used a similarly weaponized package named pretty-log.
This social-engineering model is particularly effective against developers: the assessment appears to require normal setup steps such as npm install and application execution, while artificial deadlines and instructions not to use AI assistants discourage code review.
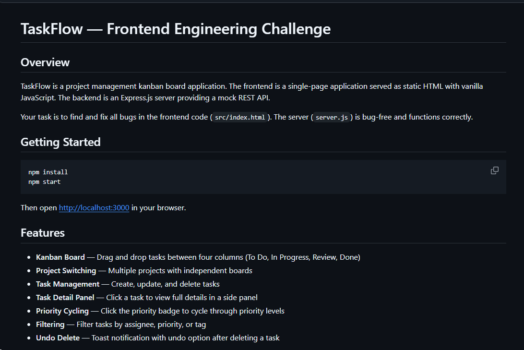
Kaspersky noted that an AI-based or manual audit could have exposed the suspicious package import.
NodeRabbit is a Node.js-based RAT capable of operating across Windows, Linux, and macOS.
It generates a host-specific identifier from system attributes including hostname, username, operating-system data, architecture, and MAC address, then establishes persistence using operating-system-native mechanisms.
On Windows, early variants copied themselves into directories disguised as Microsoft Edge Update or Intel Driver & Support Assistant components, paired a renamed node.exe binary with a JavaScript payload, and created Registry Run keys or scheduled tasks.
Linux variants used cron @reboot entries, while macOS variants created LaunchAgents.
Mirage Kitten Campaign
The implant communicates with Azure-hosted command-and-control infrastructure using encrypted JSON requests protected with AES-256-GCM.
Kaspersky researchers first identified NodeRabbit on a victim system in Afghanistan, then uncovered more advanced variants in Egypt and Ethiopia.
Operators can collect system and network information, enumerate processes, run shell commands, read and write files, alter beacon intervals, and execute arbitrary Node.js scripts.
Later NodeRabbit builds added proxy discovery and authentication support, anti-analysis checks, and developer-focused persistence through a fake VS Code extension branded as “GitHub Copilot Helper” and malicious Git post-merge or post-checkout hooks.
PollCat, the second newly documented malware family, is an obfuscated JavaScript RAT delivered in a separate React-based assessment named RankChallenge-react.
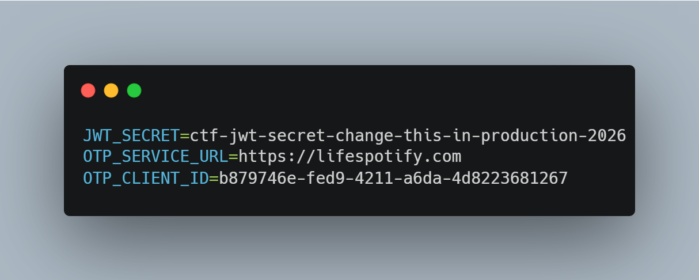
.env file (Source : Kaspersky).The lure uses recruiter-supplied, short-lived OTP codes and a one-hour completion window, but the malware begins in the background during application startup before the victim enters a code.
After registration, PollCat can inventory the host, execute commands, list and delete files, enumerate drives and running processes, transfer files in either direction, start hidden processes, and execute attacker-provided JavaScript.
Its SYSTEM_CHECK routine inventories software and security-product-related directories, including paths associated with Microsoft, CrowdStrike, SentinelOne, Palo Alto Networks, Fortinet, Sophos, and Kaspersky.
PollCat’s C2 design also overlaps with the group’s earlier Retrograde/MiniFast tooling: both treat an HTTP 400 response as a successful session handshake, extract a socketId, and use that value for command polling.
The shared protocol structure, identical default beacon timing, victimology, and recurring use of Azure Websites and Cloudflare-backed domains underpin Kaspersky’s high-confidence attribution to Mirage Kitten.
The campaign marks a significant shift for Mirage Kitten, which previously favored native C, C++, and Go malware often delivered through DLL search-order hijacking.
NodeRabbit and PollCat instead blend into modern developer workflows by abusing Node.js dependencies, JavaScript execution, IDE extensions, Git hooks, and cloud-hosted assessment files.
Organizations should treat unsolicited coding challenges as untrusted software, isolate assessments in disposable environments.
Inspect bundled dependencies before execution, monitor for unexpected Node.js processes and new scheduled tasks, and review Git hooks and VS Code extension directories.
Kaspersky detects the activity as Trojan.JS.MirageKitten.*.
IOCs
| Type | Domain |
|---|---|
| Domain | oracle-challenge.s3.us-east-1.amazonaws.com |
| Domain | naturalapplication.azurewebsites.net |
| Domain | retaildemo.azurewebsites.net |
| Domain | tubitak.azurewebsites.net |
| Domain | rgbteller.azurewebsites.net |
| Domain | wslwebui.azurewebsites.net |
| Domain | plugplay.azurewebsites.net |
| Domain | crossdwm.azurewebsites.net |
| Domain | wdisystem.azurewebsites.net |
| Domain | wslmenus.azurewebsites.net |
| Domain | dnshnsdev.azurewebsites.net |
| Domain | hpjumpsrv.azurewebsites.net |
| Domain | storview.azurewebsites.net |
| Domain | healthcomfsdpower.com |
Note: IP addresses and domains are intentionally defanged (e.g., [.]) to prevent accidental resolution or hyperlinking. Re-fang only within controlled threat intelligence platforms such as MISP, VirusTotal, or your SIEM.
★ Which Security Tools Should You Cut? Score Them on One Page – Download the Inherited Security Stack Guide