

CloudSEK’s TRIAD threat intelligence team has uncovered a sophisticated spearphishing campaign orchestrated by the Muddy Water APT group, targeting multiple critical sectors across the Middle East, including diplomatic, maritime, financial, and telecom entities.
The campaign leverages icon spoofing and weaponized Word documents to deliver a newly identified Rust-based implant dubbed “RustyWater,” capable of maintaining persistent, low-noise command and control while evading traditional antivirus and endpoint detection and response solutions.
Muddy Water, tracked by various organizations under the names Earth Vetala, MERCURY, Static Kitten, and Mango Sandstorm, has historically relied on PowerShell and VBScript loaders for initial access and post-compromise operations.
This latest campaign marks a significant tactical shift toward Rust-based implants, offering enhanced modularity, reduced operational noise, and improved resilience against legacy security controls.
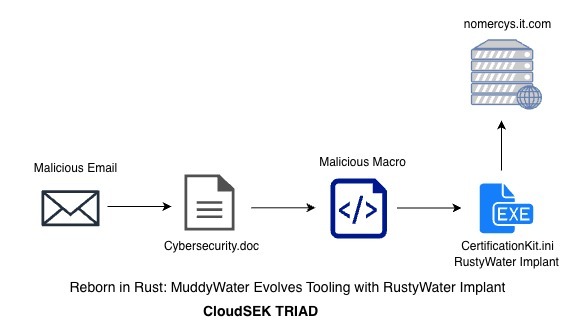
While the Rust implant has received limited documentation under designations such as Archer RAT and RUSTRIC, researchers attribute this variant as RustyWater to avoid nomenclature conflicts and provide clarity in threat tracking.
Technical Kill Chain Analysis
Initial Access Vector: The campaign begins with spear phishing emails impersonating legitimate entities.
Security researchers identified emails purportedly originating from “info@tmcell,” mimicking official correspondence from TMCell (Altyn Asyr CJSC), Turkmenistan’s primary mobile operator.
These emails, titled “Cybersecurity Guidelines,” arrive with a malicious Word attachment named Cybersecurity.doc.
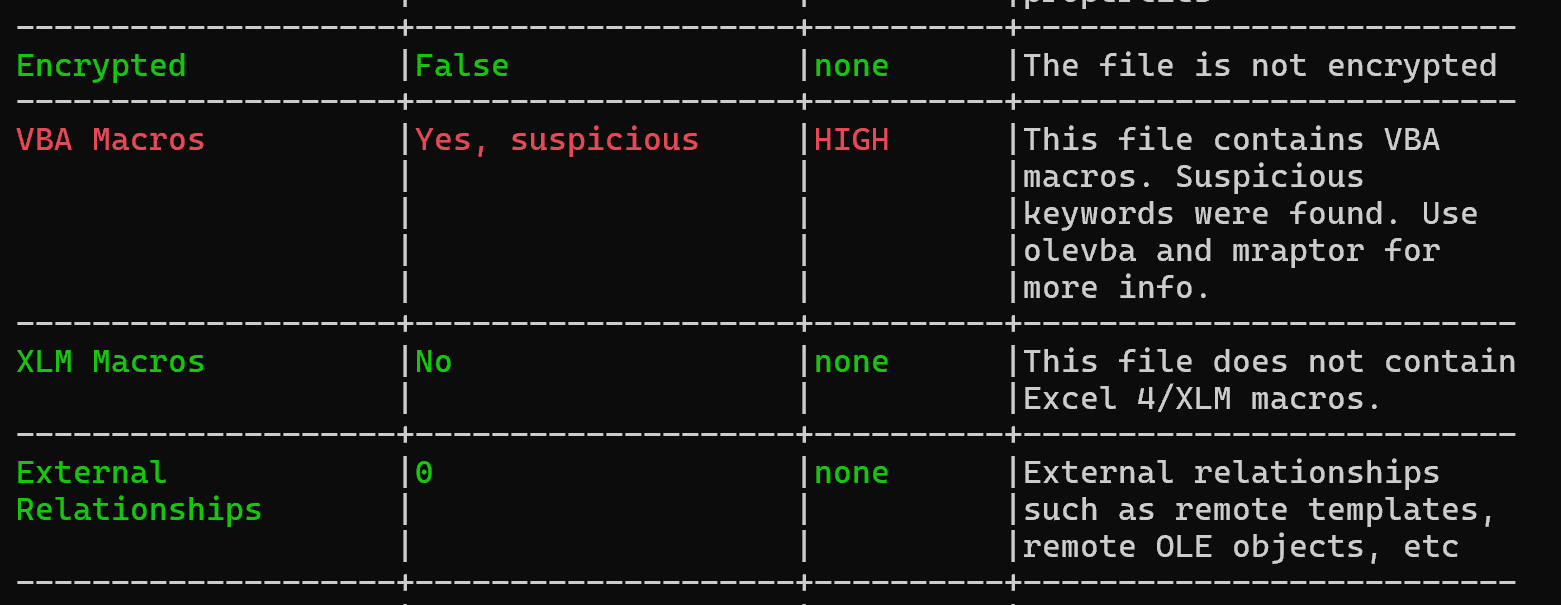
Stage One – Document Exploitation: The Cybersecurity.doc file contains embedded VBA macros that execute two critical functions.
The WriteHexToFile function reads a hex-encoded byte stream from UserForm1.TextBox1.Text, decodes the data, and writes a reconstructed payload to disk as CertificationKit.ini in C:\ProgramData.
Subsequently, the obfuscated love_me_function reconstructs the string WScript.Shell using ASCII values and the Chr() function, instantiates a COM object, and executes the written payload via cmd.exe.
Stage Two – RustyWater Implant: The decoded PE file (presented as reddit.exe with a Cloudflare logo) contains the actual RustyWater implant compiled in Rust.
Upon execution, the malware establishes anti-debugging mechanisms through Vectored Exception Handlers and collects victim machine information including username, computer name, and domain membership. All strings remain encrypted using position-independent XOR encryption.
We can run oleid to identify if any macros are present in the document and dump them further using tools like oledump.
RustyWater implements multi-layered evasion techniques designed to circumvent modern security infrastructure. The malware scans for more than 25 antivirus and EDR products by examining agent files, service names, and installation paths.
Command and control communication employs three layers of obfuscation JSON encoded data is base64 encoded, then XOR encrypted making traffic analysis substantially more difficult.
Persistence is achieved through registry-based autostart mechanisms. The malware writes itself to the Windows Run registry key under the current user context, pointing to the payload at C:\ProgramData\CertificationKit.ini.
The implant utilizes the Rust reqwest library for HTTP-based C2 communication, implementing configurable timeouts, connection pooling, retry logic, and randomized sleep intervals with jitter to avoid temporal pattern detection.
Attribution and Campaign Scope
Technical artifacts and similarities provide high-confidence attribution to Muddy Water. VBA macro code patterns, including distinctive hex-encoded payload embedding within UserForm controls, match previously documented campaigns.
Infrastructure pivoting revealed compromised legitimate email accounts impersonating government entities of Turkmenistan and the UAE, facilitating credential-based spearphishing.
Researchers identified at least five additional lures targeting UAE financial and educational sectors, alongside campaigns targeting Middle East maritime industry entities approximately November 2025.
The combination of registry-based persistence, delayed beaconing, and in-memory execution enables long-term silent compromise with minimal forensic artifacts.
Modular architecture allows post-compromise capability expansion without binary re-delivery, facilitating tailored surveillance aligned with victim roles.
Dynamic C2 failover mechanisms, request jitter, and protocol switching significantly reduce detection efficacy of traditional network countermeasures.
Follow us on Google News, LinkedIn, and X to Get Instant Updates and Set GBH as a Preferred Source in Google.







