

Compromised Namastex npm packages are delivering a new TeamPCP-style CanisterWorm variant that targets developer secrets, browser and wallet data, and then attempts to spread across npm and PyPI ecosystems using canister-backed exfiltration infrastructure.
The campaign closely mirrors the original CanisterWorm, reinforcing concerns that TeamPCP is continuing to refine its supply chain tooling against real-world development pipelines.
The affected releases include @automagik/genie versions 4.260421.33 through 4.260421.39 and pgserve versions 1.1.11, 1.1.12, and 1.1.13, all sharing the same embedded RSA material used by the malicious script.
Threat hunting on the same indicators also linked previously compromised @fairwords/websocket (1.0.38–1.0.39), @fairwords/loopback-connector-es (1.4.3–1.4.4), and @openwebconcept design-system components, suggesting shared builder infrastructure or direct malware code reuse across multiple publisher namespaces.
Security researchers have discovered that several npm packages associated with Namastex Labs’ Automagik AI tooling have been surreptitiously modified to deliver a CanisterWorm-like malware payload at install time.
Socket’s AI Scanner flagged @automagik/[email protected] as malicious while the package still recorded roughly 6,700 weekly downloads, and pgserve was seeing around 1,300 weekly downloads, indicating that these are not fringe test modules but live dependencies in specialized developer workflows.
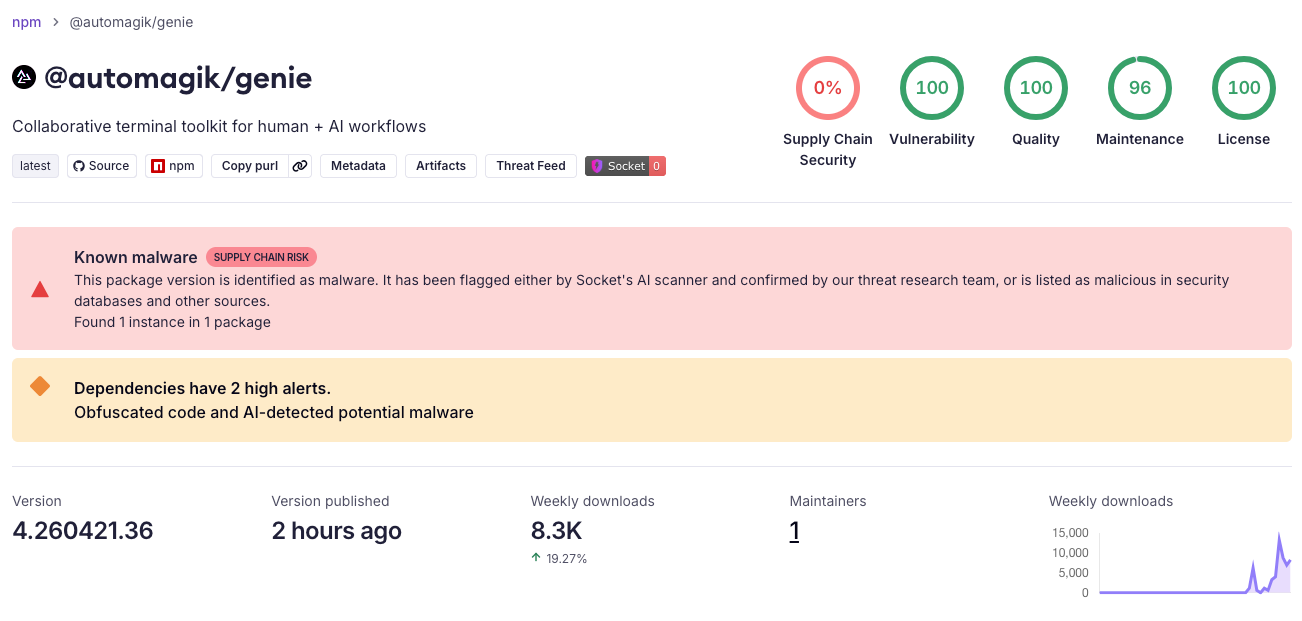
@automagik/[email protected] as malicious (Source : Socket).@automagik/genie is positioned as an AI coding and agent-orchestration CLI, while pgserve is an embedded PostgreSQL server used in development and CI testing, increasing the likelihood that compromised environments hold high-value cloud and registry credentials.
Overlap with TeamPCP’s CanisterWorm
The newly identified payload reuses the same core tradecraft seen in TeamPCP’s earlier CanisterWorm npm worm, which was the first publicly documented supply chain malware to use an Internet Computer Protocol (ICP) canister as a dead‑drop command‑and‑control channel.
The implant again executes at install time via a malicious postinstall script, performs aggressive credential harvesting from developer systems, exfiltrates data to both a conventional HTTPS webhook and an ICP canister, and includes worm-like logic to republish poisoned package versions using stolen npm tokens.
Investigators also found an explicit reference to a TeamPCP/LiteLLM method in the malicious code, strengthening the linkage to the same actor or toolkit family.
In this incident, the hardcoded infrastructure includes telemetry.api-monitor[.]com endpoints and an ICP canister ID cjn37-uyaaa-aaaac-qgnva-cai.raw.icp0[.]io/drop, which function as dual exfiltration sinks for harvested secrets.
While the canister is not identical to the one used in the original CanisterWorm wave, the behavioral overlap, encryption approach, and self-propagation logic are consistent with TeamPCP’s broader supply chain operations documented across npm and CI/CD ecosystems.
The malicious JavaScript performs four main functions once triggered during package installation.
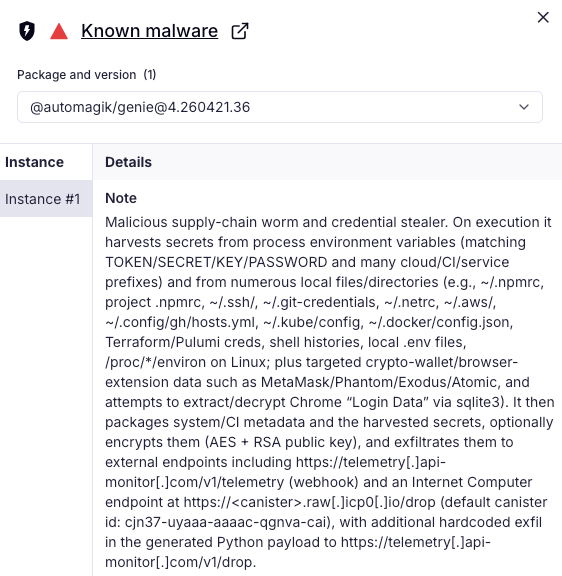
First, it harvests environment variables and local configuration files that commonly store authentication material, such as .npmrc files, SSH keys, .git-credentials, .netrc, cloud provider credentials (AWS, Azure, GCP), Kubernetes and Docker config, Terraform and Pulumi state, Vault data, local .env files, and shell history.
This behavior is entirely inconsistent with legitimate npm install workflows and is clearly aimed at full session and infrastructure takeover.
Second, the malware targets browser and cryptocurrency wallet artifacts, attempting to access Chrome login data, MetaMask and Phantom extension stores, and local wallet files for ecosystems including Solana, Ethereum, Bitcoin, Exodus, and Atomic Wallet.
Third, it exfiltrates all collected data to both an HTTPS webhook and the ICP canister endpoint, encrypting payloads with a hybrid AES‑256‑CBC and RSA‑OAEP‑SHA256 scheme when a bundled RSA public key is available, and falling back to plaintext packaging otherwise.
Finally, it attempts self‑propagation by extracting npm tokens from the victim, enumerating publishable packages, injecting a malicious postinstall hook, and republishing tainted versions, while a parallel routine prepares PyPI packages using a .pth‑based loader and Twine if Python credentials are present.
Evidence of publisher compromise
Multiple ecosystem signals point to a compromise of existing publisher infrastructure rather than the creation of obviously new throwaway malware packages.
The targeted modules belong to real projects with public GitHub repositories, documentation, and clear marketing around AI consulting and open source tooling, and @automagik/genie has already achieved meaningful adoption for a relatively new package.
In at least one case, pgserve was updated on npm to versions 1.1.12 and 1.1.13 without corresponding Git tags in the upstream repository, a release-path anomaly that, while not definitive on its own, fits the pattern of TeamPCP abusing stolen publishing credentials to inject backdoors into trusted namespaces.
With additional malicious versions still being published and identified, the full scope of affected maintainers and release pipelines remains under active investigation, and organizations consuming these packages are being urged to assume credential exposure.
Follow us on Google News, LinkedIn, and X to Get Instant Updates and Set GBH as a Preferred Source in Google.


