

Cybersecurity researchers Victor Viale, Sick Codes, Nick Sahler, Kelly Kaoudis, and John Jackson have recently detected a severe networking vulnerability in the Netmask npm package. In general, the apps use the Netmask to parse IPv4 addresses, and the CIDR relates them.
Apart from this, the component has procured more than 238 million downloads till now in its lifetime, and near about 278,000 GitHub repositories are also dependent on the netmask.
Due to the presence of the bug in the library, the netmask attends a distinct IP while parsing an IP address with zero in the lead, and this occurs due to the incorrect validations in place.
Leading Zero Alters the IP address
The security flaw that is being detected by the security experts is identified as “CVE-2021-28918,” and this flaw affects the working method and chain of the netmask.
The IPv4 addresses are generally expressed in decimal format, but the fact is that an IP address can be expressed in several formats.
Let’s make it a bit more clear, suppose your system’s IPv4 address interpreted in decimal format (106.30.67.309), but due to the bug, the same IP could be displayed as 0780.0034.0014.0214, in octal format.
Suppose we give you an IP in a decimal format which is broadly conceived as the local loopback address or localhost, “127.0.0.1.” What if here we ask you to put a 0 before it? Will it parse 0127.0.0.1 as 127.0.0.1 or something else?
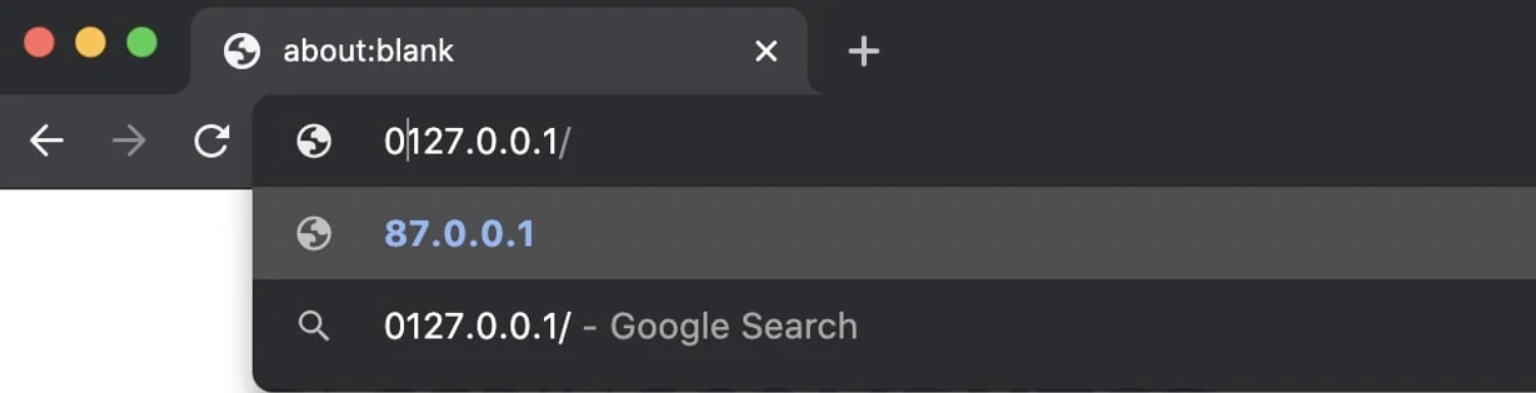
While I tried this on the address bar of my Chrome web browser, it parsed me to this IP “87.0.0.1,” as this is how the apps are made to handle these type of obscure IPs.
SSRF bypass to Remote File Inclusion
Initially, this bug may seem harmless, but, in reality, this flaw can lead an attacker to influence the IP address input and accelerate the inflation of various other security flaws from Server-Side Request Forgery (SSRF) bypass to RFI (Remote File Inclusion).
Moreover, the threat actors can easily exploit this flaw for Remote File Inclusion (RFI) with an IP address that seems private to the netmask.
There are many projects that use the netmask for IP parsing, and that’s why this security vulnerability is concerning security analysts.
Security fixes
The cybersecurity analysts who have discovered and reported the “CVE-2021-28918” flaw has pushed out a series of fixes. And with the netmask version 2.0.0, the researchers have fixed the “CVE-2021-28918” security flaw.
So, currently, the security analysts have strongly recommended the users upgrade their outdated netmask version to the fixed version 2.0.0. And to spread this awareness, they have also published their findings on different platforms.
You can follow us on Linkedin, Twitter, Facebook for daily Cybersecurity, and hacking news updates.







