

The cybersecurity team of zLabs Zimperium has recently detected several applications that have stolen the passwords of thousands of Facebook users.
Not only this, but the Zlab security researchers have also checked this attack, and they claimed that the malware used in this attack was dubbed as “FlyTrap.”
According to the report, FlyTrap has been conducting all its attacks and operation from Vietnam. Apart from all this the experts also came to know that FlyTrap is a member of a trojan family that employs social engineering to win over its victims’ Facebook accounts.
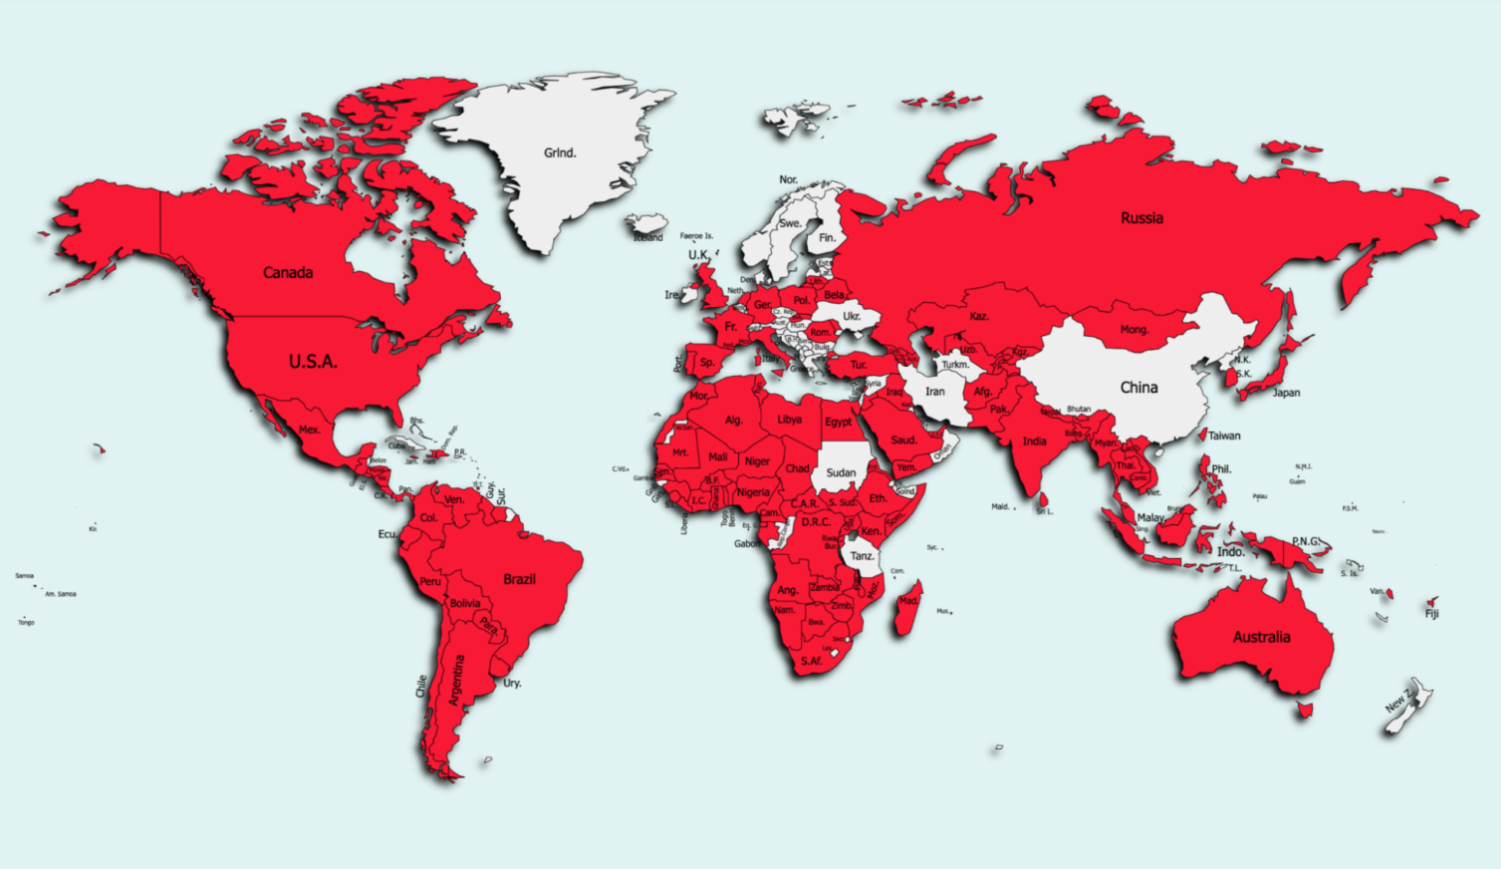
The security researchers asserted that this malware has spread to nearly 10,000 users, and since March 2021, and it has been attacking in at least 144 countries.
Abilities of FlyTrap
FlyTrap is a mobile application, that directly attacks the victim’s Facebook account with the trojan infecting their Android device.
Here, methods and techniques that are used by social engineering are quite effective in the digitally connected world. Not only this, but different threat actors used this method to spread malware from one victim to another.
After hijacking the victim’s account the threat actors generally collects the data from the Android device of the victim’s, that’s why we have mentioned them below:-
- Facebook ID
- Location
- Email address
- IP address
- Cookie associated with the Facebook account
- Tokens associated with the Facebook account
Luring Victims with High-quality apps
The FlyTrap has a high-quality design, that is quite effective in nature and this application is being distributed through Google Play and third-party Android stores.
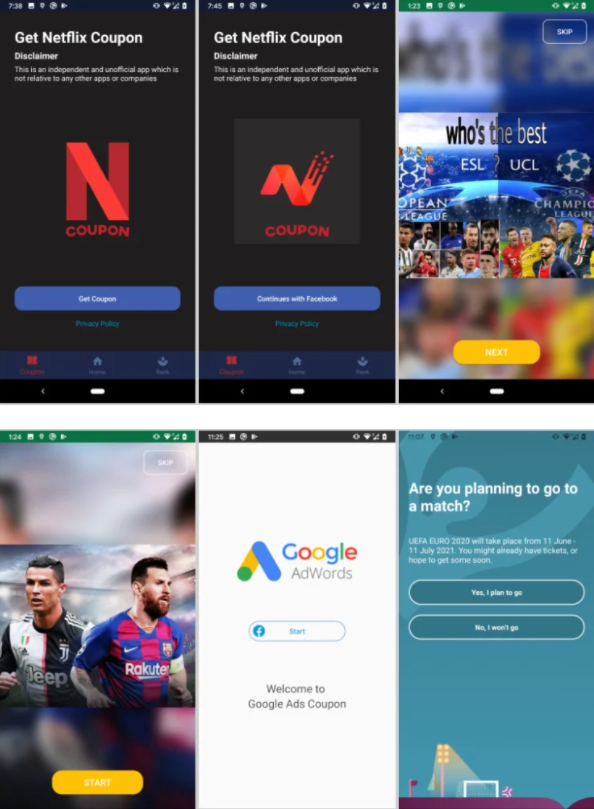
However, the malicious application starts luring by offering free coupon codes for Netflix as well as Google AdWords, and not only this but it also voted for the favorite soccer team or player, in the delayed UEFA Euro 2020 competition.
Victims of FlyTrap Trojan
The experts have done a brief investigation, and they found that the database which has been stolen by the threat actors contains geolocation information of thousands of victims, and based on this information a victimology map has been generated.
FlyTrap Trojan Android Applications
The security analyst has found 9 applications that were involved in this malicious threat attack, and here we have mentioned them below:-
- GG Voucher
- Vote European Football
- GG Coupon Ads
- Chatfuel
- GG Voucher Ads
- GG Voucher
- Net Coupon
- Net Coupon
- EURO 2021 Official
FlyTrap is an active malicious threat attack, and the experts are continuously trying to bypass this kind of attack. The tools and methods that were used by FlyTrap are quite effective and that’s what makes it powerful for the victims to detect the malware application.
You can follow us on Linkedin, Twitter, Facebook for daily Cybersecurity and hacking news updates.







