

Security researchers have disclosed critical vulnerabilities in Airoha-based Bluetooth headphones that enable attackers to compromise connected smartphones through chained exploits.
The three vulnerabilities CVE-2025-20700, CVE-2025-20701, and CVE-2025-20702 affect dozens of popular headphone models from Sony, Marshall, Jabra, Bose, and other manufacturers.
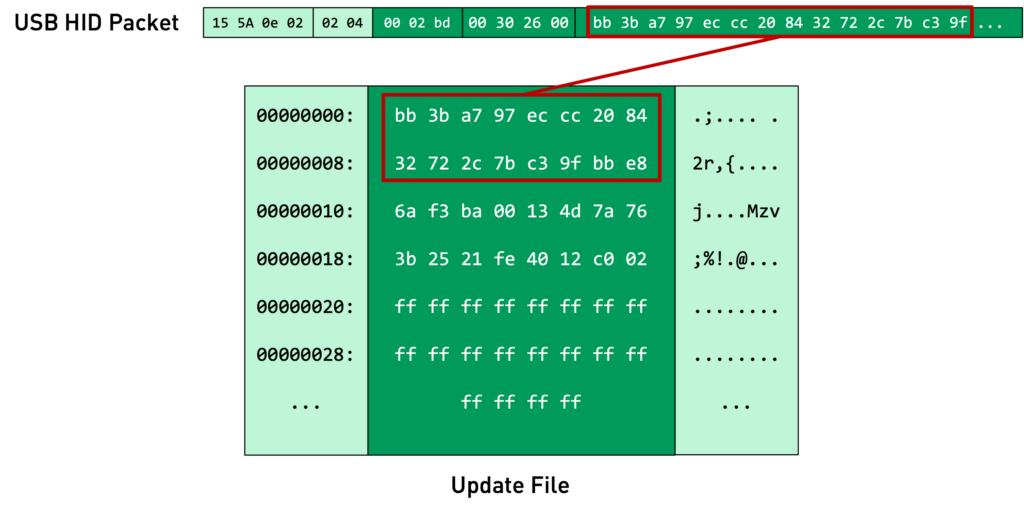
The vulnerabilities center on missing authentication mechanisms and exposed debugging functionality in Airoha’s custom RACE protocol, which is used for device configuration and firmware updates.
Attackers within Bluetooth range can exploit these flaws without requiring prior pairing or user interaction.
The Attack Chain
The exploitation begins with unauthenticated connection establishment. CVE-2025-20700 allows attackers to connect via Bluetooth Low Energy without authentication, while CVE-2025-20701 permits unauthorized Bluetooth Classic connections.
Once connected, attackers leverage CVE-2025-20702 to access the RACE protocol, which provides arbitrary read and write access to device memory.
Using these capabilities, attackers can extract the Bluetooth Link Key the cryptographic secret shared between headphones and paired smartphones.
According to Insinuator, Researchers demonstrated that this key enables attackers to impersonate trusted headphones to the victim’s phone, gaining a privileged position on the device.
From this privileged state, attackers can execute multiple attacks. Using the Bluetooth Hands-Free Profile, they can access phone numbers, contact lists, and call history.
More critically, attackers can trigger voice assistants to send messages, make calls, or extract location data on unlocked devices.
The vulnerabilities also enable call hijacking, where attackers silently accept incoming calls and capture audio streams, or eavesdropping by initiating calls to attacker-controlled numbers using the victim’s phone.
The vulnerability survey identified at least 30 vulnerable devices, including Sony WF-1000XM5, Marshall ACTON III, JBL Live Buds 3, and Beyerdynamic Amiron 300.
However, researchers note this represents only verified devices, with potentially many more affected models remaining unpatched.
Notably, some vendors like Jabra implemented additional security measures and patched their devices, while others including Sony and Bose have not publicly addressed the vulnerabilities.
Airoha released SDK patches in June 2025, but vendor adoption remains inconsistent. Users should immediately update their devices and remove old paired devices from their phones.
Researchers recommend high-value targets like journalists and diplomats consider using wired headphones instead.

The researchers released a white paper and the RACE Toolkit, enabling users to verify device vulnerability status independently.
Manufacturers are urged to apply Airoha patches and conduct security assessments before product release using established Bluetooth security testing methodologies.
The disclosure follows responsible disclosure practices, with technical details released six months after initial notification to allow vendors adequate patching time.
Follow us on Google News, LinkedIn, and X to Get Instant Updates and Set GBH as a Preferred Source in Google.


