

A new Android trojan called BrasDex has been identified as the work of the same threat actors responsible for the Casbaneiro malware that targets Windows banking systems.
The security analysts at ThreatFabric recently spotted an ongoing multi-platform campaign in which Brazilian users have been observed to be targeted as part of this malware (BrasDex) attack.
Complicated Keylogging capabilities are built into BrasDex to exploit the Accessibility Services in an attempt to extract and acquire credentials specifically from:-
- A set of Brazilian-targeted apps
- A highly capable Automated Transfer System (ATS) engine
BrasDex Android Malware Stealing User Data
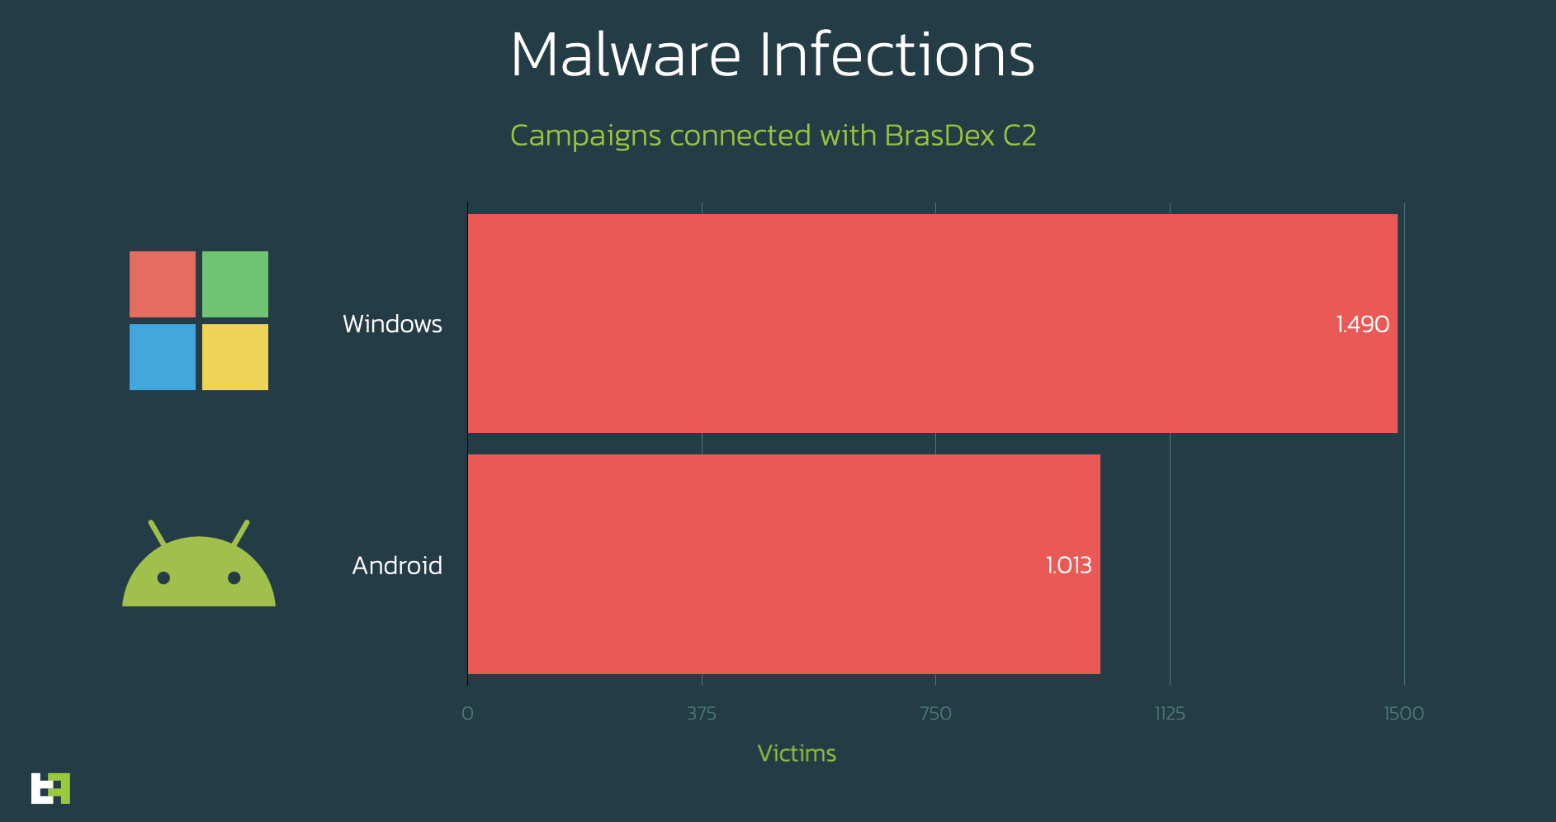
Casbaneiro is also being controlled via the C2 infrastructure that is being used in conjunction with BrasDex. Brazil and Mexico are the two countries that have also recently experienced the same problems with their banks and cryptocurrency services.
This malware has been active for over a year now and initially misrepresented itself as an Android setting application to specifically target Brazilian banking apps.
The various malware families have begun to abandon the use of overlays for a more lean and flexible solution, which does not require a continuous update or additional data to be downloaded, as they are more efficient.
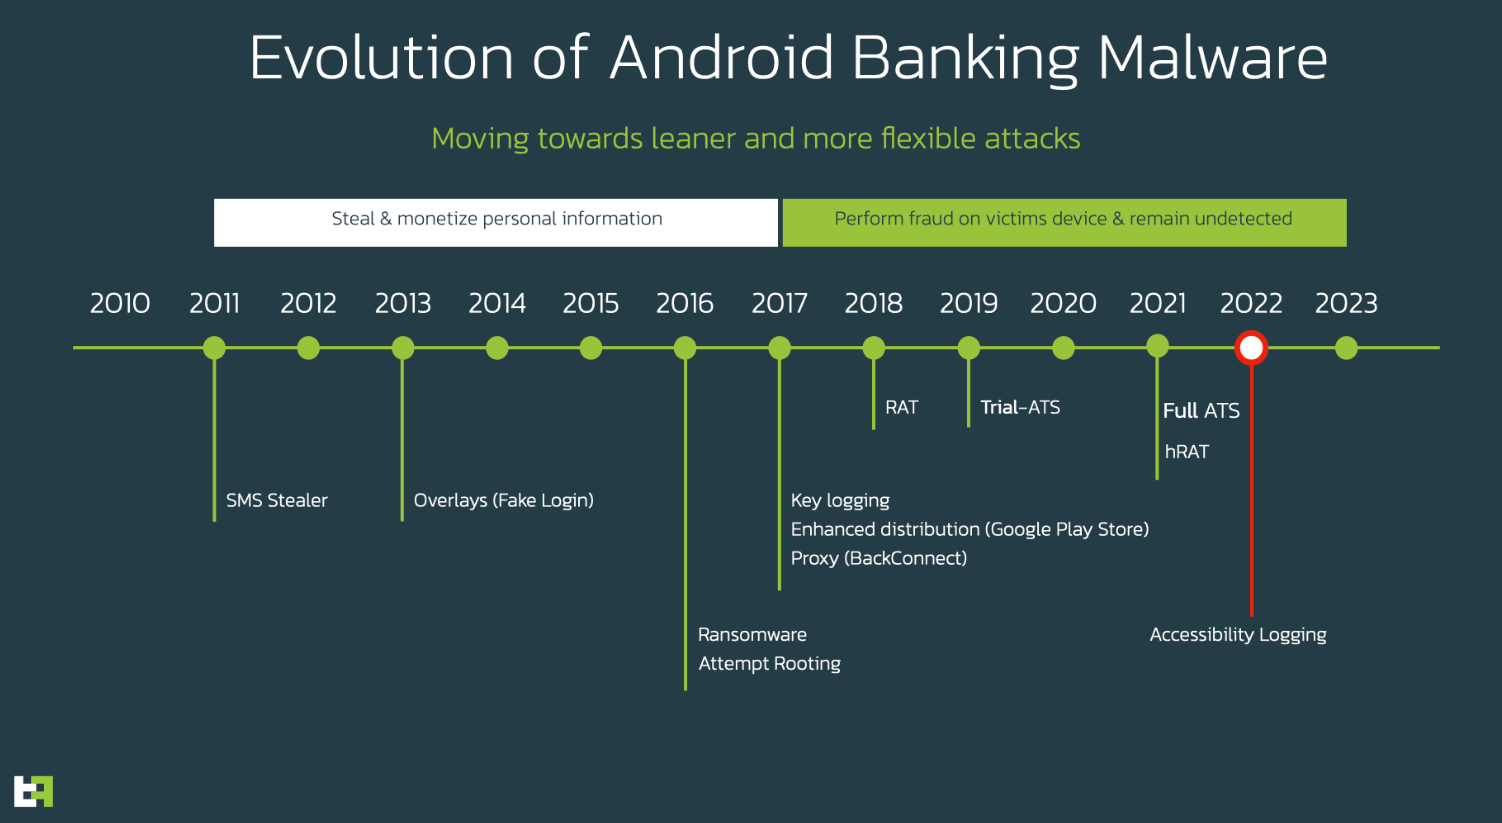
It is becoming more and more common for malware families to incorporate accessibility logging into their malware designs in order to extract logging credentials and other personal information from victims infected by the malware.
ATS (Automated Transfer System) capabilities are one of the main reasons that make BrasDex stand out from many other malware families.
BrasDex Capabilities & Panel
Here below we have mentioned the capabilities of BrasDex:-
- Keylogging
- ATS
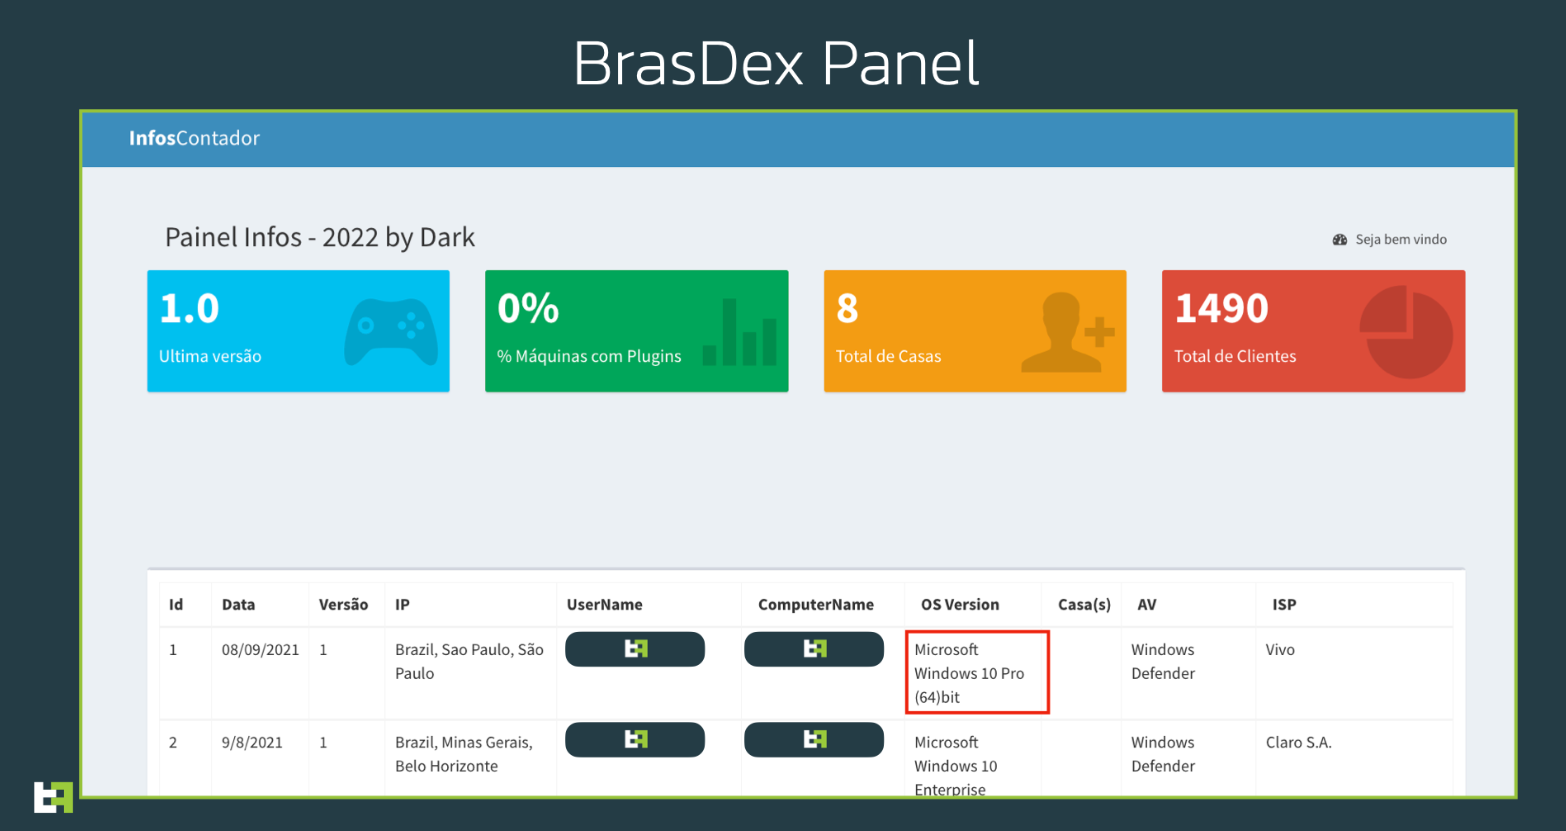
As ThreatFabric investigated this malware family, they were also able to get some visibility into the Panel hosted on the C2 server, which was an important discovery.
The panel contains multiple pages and other important information like:-
- List of infected devices
- List of service providers
- List of the device models
- List of the Android version
- Logs obtained from the infected devices
Targets Attacked
Specifically focused on the Brazilian market, BrasDex is one of the most well-known malware families. In order for the malware to operate on Brazilian devices only, test checks are included in the malware itself.
It did this by performing a programmatic check on the SIM card used by the device to ascertain that its SIM is operating in Brazil, after which it complete all its desired operations and then configure the device properly.
However, the malware automatically shuts down and abandons all the communicating channels to its C2 server, if it detects that the SIM card on the device is from anywhere else.
There may be some unknown problem with the Pix payment system within the Brazilian banking ecosystem causing this hard dedication to a single market.

In 2020, Pix was introduced and has been one of the fastest payment systems ever created by the Brazil Central Bank. By knowing a user’s identifier, it is possible for a user to transfer payments to another user via Pix.
There is no doubt that BrasDex and Casbaneiro are two of the most dangerous malware families available today. A large number of Android and Windows users can be targeted in broad daylight by the actor behind them.
On the very first border of the transaction, there is an urgent need for an effective solution to detect suspicious behavior during the transaction as well as to identify the threats present on the device of the customer.
Secure Web Gateway – Web Filter Rules, Activity Tracking & Malware Protection – Download Free E-Book







