

Recently, Google has released a new version of Google Chrome browser for Windows, Mac and Linux, that contains only one bugfix for a zero-day vulnerability that was exploited in the wild.
This vulnerability was described as an issue, and it’s a heap overflow vulnerability in JavaScript engine V8. Security researcher Mattias Buelens asserted the name of the vulnerability as CVE-2021-21148 and informed Google regarding it on January 24, 2021.
Google security team issued a report on attacks by North Korean cybercriminals on the data security industry. However, some of these attacks were to tempt security researchers into a specific blog where the malware was launched on their systems by a zero-day browser vulnerability.
Root cause summary
Most of the time, the PoC code help to extract the bug from the attack code so that the security researchers could investigate the root cause of the vulnerability.
After a proper investigation, the experts affirmed that the bug that has been used by the attacker was a Double Free bug that appeared in the part of the DOM object’s attribute value release.
However, the API in this vulnerability was used to publish the attribute of string data attached to the DOM object. While the API internally APP_DATA::FreeCachedMemmanages the memory to be published through a function.
Arbitrary Function Call
In an arbitrary function call, the threat actors execute the utility function to analyze the internal situation of the method and plan to call necessary APIs arbitrarily.
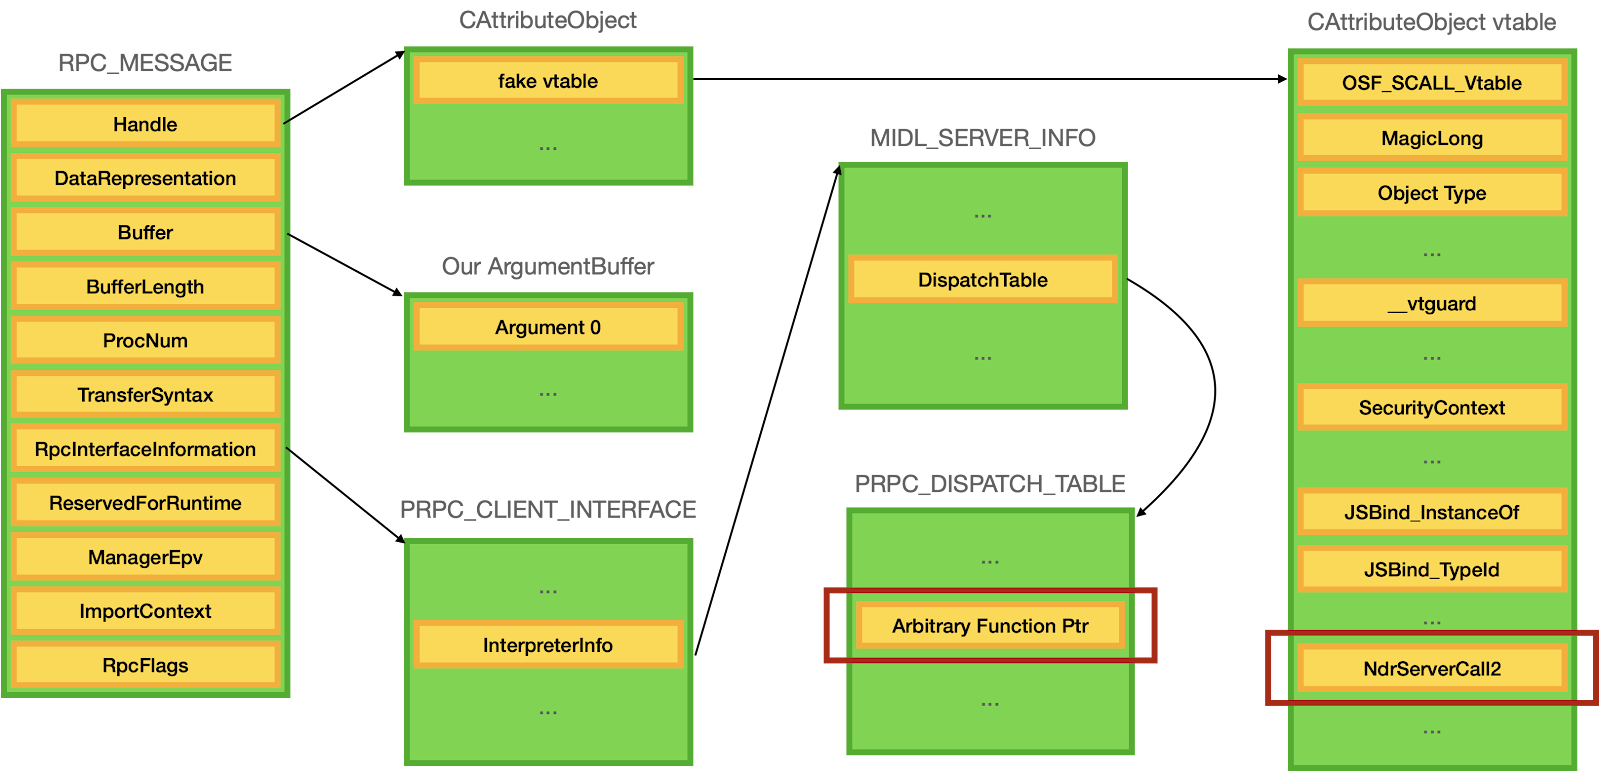
In case of this attack code, if the Control Flow Guard is implemented, then the protection method is neglected, and the threat actors exploit the RPC mechanism presented by the Windows operating system to convey the arbitrary APIs.
Shellcode summary
The shellcode simply sends a list of processes that are operating on the infected system through which it collects all the necessary information of the infected target and then downloads and executes the further malicious code encrypted from the C2 server to memory.
Apart from this, all the key features of the malicious codes are classified during analysis and here we have mentioned them below:-
- Direct System Call
- Disable User Mode Hook
- In Process Dll Hiding

According to the cybersecurity researchers, the cybercriminals mostly overworked a zero-day vulnerability in Chrome. And Google did not explain whether CVE-2021-21148 was utilised in attacks, but many experts believe that this was the actual case.
And to avoid all this exploitation of the vulnerability by various cybercriminals, Chrome users are recommended to update their browser to the most recent version.
You can follow us on Linkedin, Twitter, Facebook for daily Cybersecurity and hacking news updates.







