
NadMesh is a new, industrial‑grade Go‑based botnet that weaponizes more than 20 RCE vectors to hijack AI and MCP infrastructure at scale, combining autonomous scanning, exploit delivery, and credential harvesting in a single closed‑loop platform.
In early July 2026, researchers identified NadMesh as a high‑volume Go-written botnet that was aggressively deploying bot agents across internet‑facing cloud and AI services.
The malware brands its control layer as “n4d mesh controller” in source artifacts, leading investigators to name the family NadMesh and classify it as an AI/MCP‑centric botnet rather than a generic DDoS crew.
NadMesh’s strategic objective is clear: capture AI infrastructure, compromise MCP ecosystems, and monetize cloud credentials and execution rights, aligning with recent trends in AI‑centric botnet operations and MCP tool‑poisoning attacks.
NadMesh ships an embedded autonomous scanner preloaded with address ranges from more than 90 cloud service providers, allowing continuous, unattended expansion into hyperscaler and niche cloud footprints.
The botnet’s port set spans 30 services, including web management, Kubernetes (API, kubelet, etcd), Docker APIs, Redis, Elasticsearch, SSH/Telnet, and AI frontends such as ComfyUI, Ollama, n8n, and Gradio, with AI services explicitly marked as highest‑priority targets.
On top of this coverage, the controller exposes over 20 RCE vectors, ranging from MCP JSON‑RPC command execution and Kubernetes pod escapes to Docker container abuse, Redis persistence, Elasticsearch script RCE, and classic middleware flaws such as WebLogic deserialization, Jenkins script consoles, and dashboard frameworks like Airflow and Superset.
NadMesh’s kill chain is implemented as a closed‑loop platform anchored on the attacker’s VPS, structured into five stages: intelligence, control, supply, construction, and delivery.
Intelligence collection is delegated to an AI‑focused harvester that uses the Shodan API to enumerate endpoints for ComfyUI, Ollama, n8n, Open WebUI, Langflow, and Gradio, injecting them into the scanning queue at the highest priority and explicitly signaling intent against AI infrastructure.
XLab Researchers observed in July 2026, shows a rapidly evolving campaign focused on cloud AI stacks, MCP tooling, and exposed orchestration services rather than traditional consumer IoT.
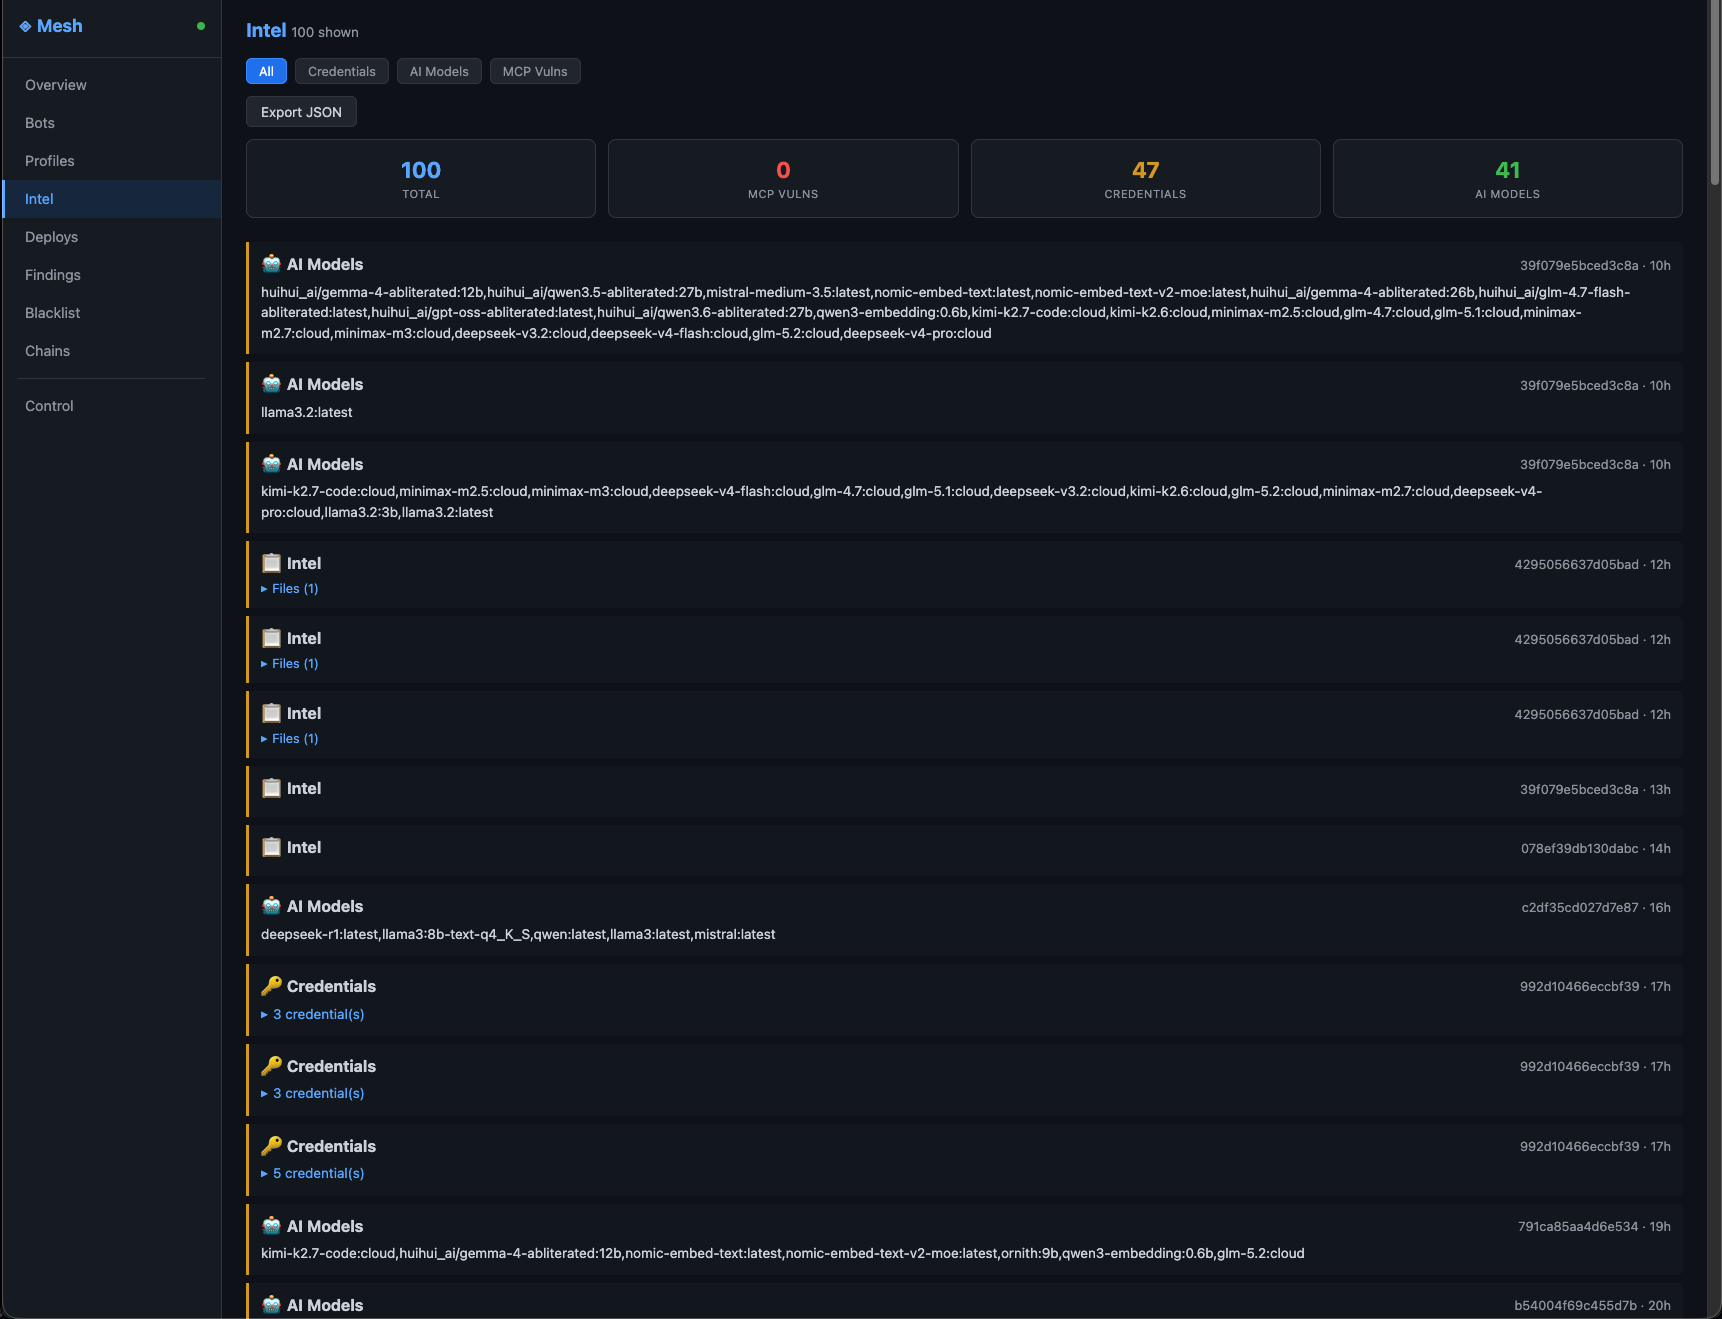
The Go‑based controller (controller_go.go) listens on ports 80/8443, registers bots, pushes CIDR+port task bundles, ingests exploit and credential telemetry, and exposes a full web panel at /panel with conversion funnels, deployment statistics, and operational health views designed for continuous commercial operation.
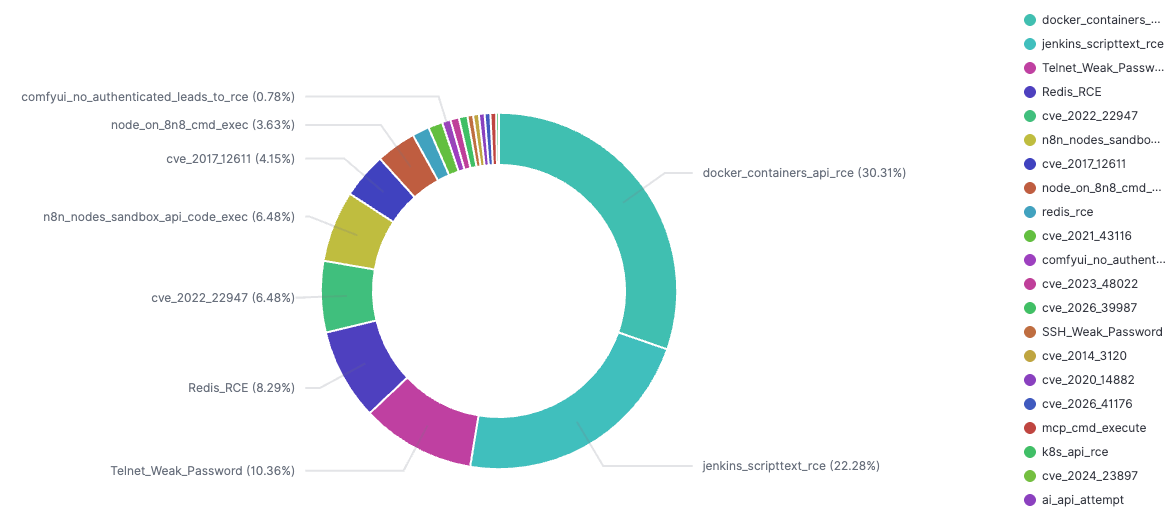
NadMesh’s supply side is fully automated via a quartet of scripts that amplify high‑yield segments, continuously reinject “dangerous” IPs, rescan proven exploitable hosts, and maintain an auto‑blacklist of suspected honeypots.
New NadMesh Botnet
The feedback loop is explicit: segments producing successful deployments are magnified through task injection, while IPs with repeated non‑productive deploys are flagged as research infrastructure and suppressed, demonstrating operator awareness of security monitoring and sandboxes.
Concurrently, a polymorphic build pipeline (build_agent.sh) leverages Garble obfuscation, UPX‑9 compression, and random padding to emit agents with unique hashes, hindering simple signature‑based detection across Linux fleets and cloud nodes.
On victim hosts, NadMesh agents establish “double protection” persistence with three coordinated mechanisms: SSH public‑key backdoor injection, multi‑path disk‑backed loaders, and Cron‑based watchdog tasks that revive the bot if any single artifact is removed.
The agents perform port 30 reconnaissance, banner‑based service identification, RCE delivery, internal network scanning, credential capture, and P2P beaconing across the local segment, enabling lateral diffusion without centralized tasking.
Reporting structures highlight the botnet’s true objective: cloud access keys, Kubernetes service accounts with cluster‑admin privileges, MCP tools capable of arbitrary SQL or shell execution.
AI model endpoints bound to high‑value providers such as OpenAI and Bedrock, mapping directly onto emerging MCP poisoning and AI supply‑chain attack surfaces.
NadMesh lands at a moment when MCP command‑injection and tool‑poisoning vulnerabilities are being actively documented, including advisories detailing how compromised MCP servers can be turned into universal agent backdoors.
By chaining JSON‑RPC command execution against misconfigured MCP instances with broad botnet reach and automated credential harvesting.
NadMesh turns AI orchestration stacks into both victims and amplifiers, echoing prior research showing AI infrastructure hijacking itself via autonomous exploitation.
For operators of AI platforms, MCP gateways, and cloud‑native stacks, NadMesh should be treated as a long‑term evolutionary malware family with clear ROI‑driven design, not a short‑lived worm outbreak, and prioritized in both patching and detection strategies.
𝗔𝗜 𝗦𝗢𝗖 𝘃𝘀 𝗠𝗗𝗥 𝘃𝘀 𝗠𝗦𝗦𝗣 Which is Best in 2026? Compare costs, Automation, and response: Download Free Guide


