

A new phishing campaign targeting Amazon Prime users has been identified, aiming to steal login credentials and other sensitive information, including payment details and personal verification data.
The attack, analyzed by the Cofense Phishing Defense Center (PDC), uses a carefully crafted email impersonating official Amazon communications to deceive recipients.
Sophisticated Email Spoofing Campaign Exploits Amazon Branding
The phishing emails appear to notify users of an expired or invalid payment method, urging them to update their information.
The sender’s address is spoofed to resemble a legitimate Amazon notification, while the email body mimics authentic branding with the Amazon logo, corporate footer, and familiar language.

The subject line creates a sense of urgency, compelling recipients to act quickly. However, closer inspection reveals that the sender’s domain is unrelated to Amazon, a key red flag.
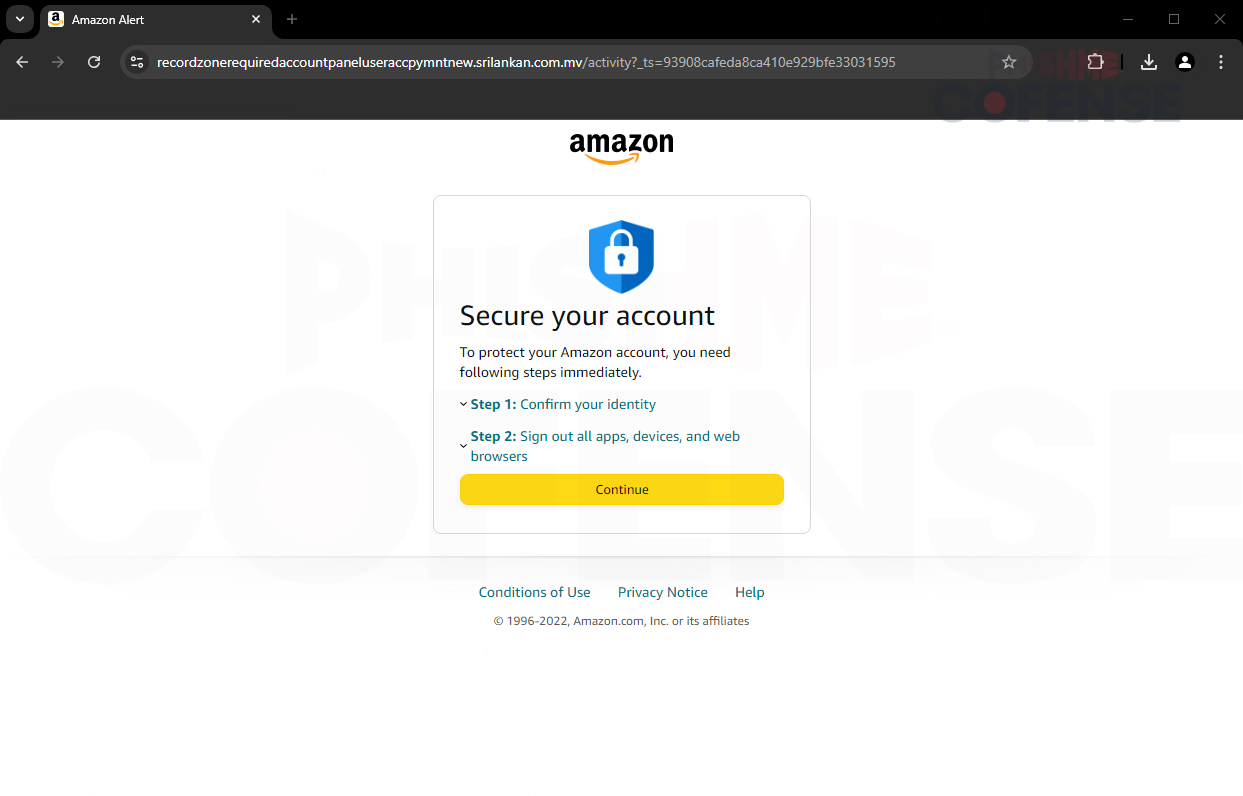
When users click on the provided link, they are redirected to a fraudulent webpage that imitates Amazon’s security verification process.
Instead of leading to Amazon’s official site, the URL redirects users to platforms like Google Docs or other suspicious domains.
This fake security notice is designed to lower suspicion and encourage victims to proceed further.
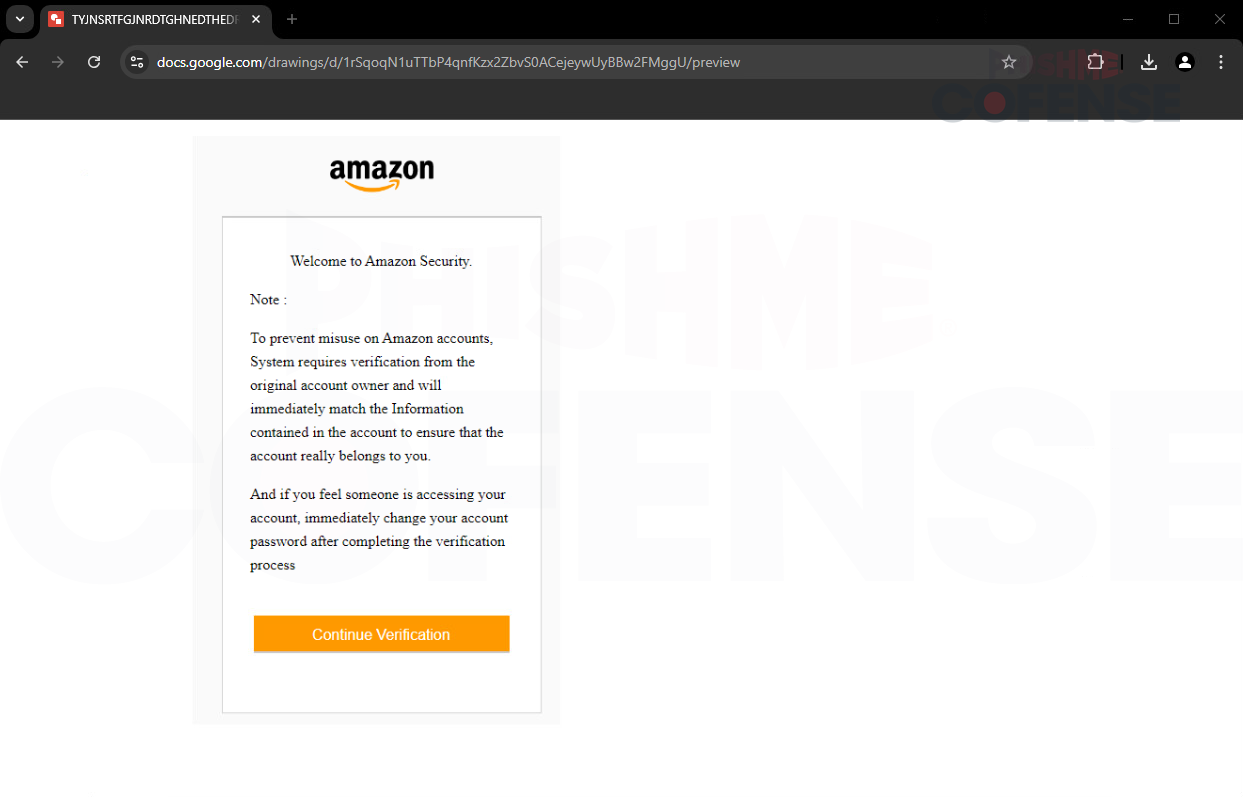
Phishing Scheme Seeks Payment and Personal Data for Fraudulent Use
Once on the phishing site, users are prompted to enter their Amazon login credentials on a counterfeit login page.
Following this step, they are directed to additional pages requesting personal information such as their mother’s maiden name, date of birth, phone number, billing address, and even credit card details.

According to Cofense Report, these details are commonly used in identity verification processes and can be exploited for unauthorized access or financial fraud.
The phishing scheme also seeks payment card information, including cardholder name, card number, expiration date, and CVV code.
If compromised, these details could enable attackers to conduct unauthorized transactions or sell the data on the dark web.
What sets this campaign apart is its multi-layered approach: it not only harvests login credentials but also requests supplementary data that could aid attackers in bypassing additional security measures.
The fraudulent pages often contain minor grammatical errors, another indicator of their illegitimacy.
To protect against such attacks, users are advised to verify the sender’s email address and avoid clicking on links within unsolicited emails.
Instead, they should log in directly through Amazon’s official website or app.
Enabling multi-factor authentication (MFA) adds another layer of security against credential theft.
The rise in phishing attacks targeting popular platforms like Amazon underscores the importance of vigilance in online interactions.
Users should remain cautious when handling sensitive information and report suspicious emails or websites directly to Amazon.
Free Webinar: Better SOC with Interactive Malware Sandbox for Incident Response, and Threat Hunting - Register Here


.webp?fit=1600,900&ssl=1&description=A new phishing campaign targeting Amazon Prime users has been identified, aiming to steal login credentials and other sensitive information.)