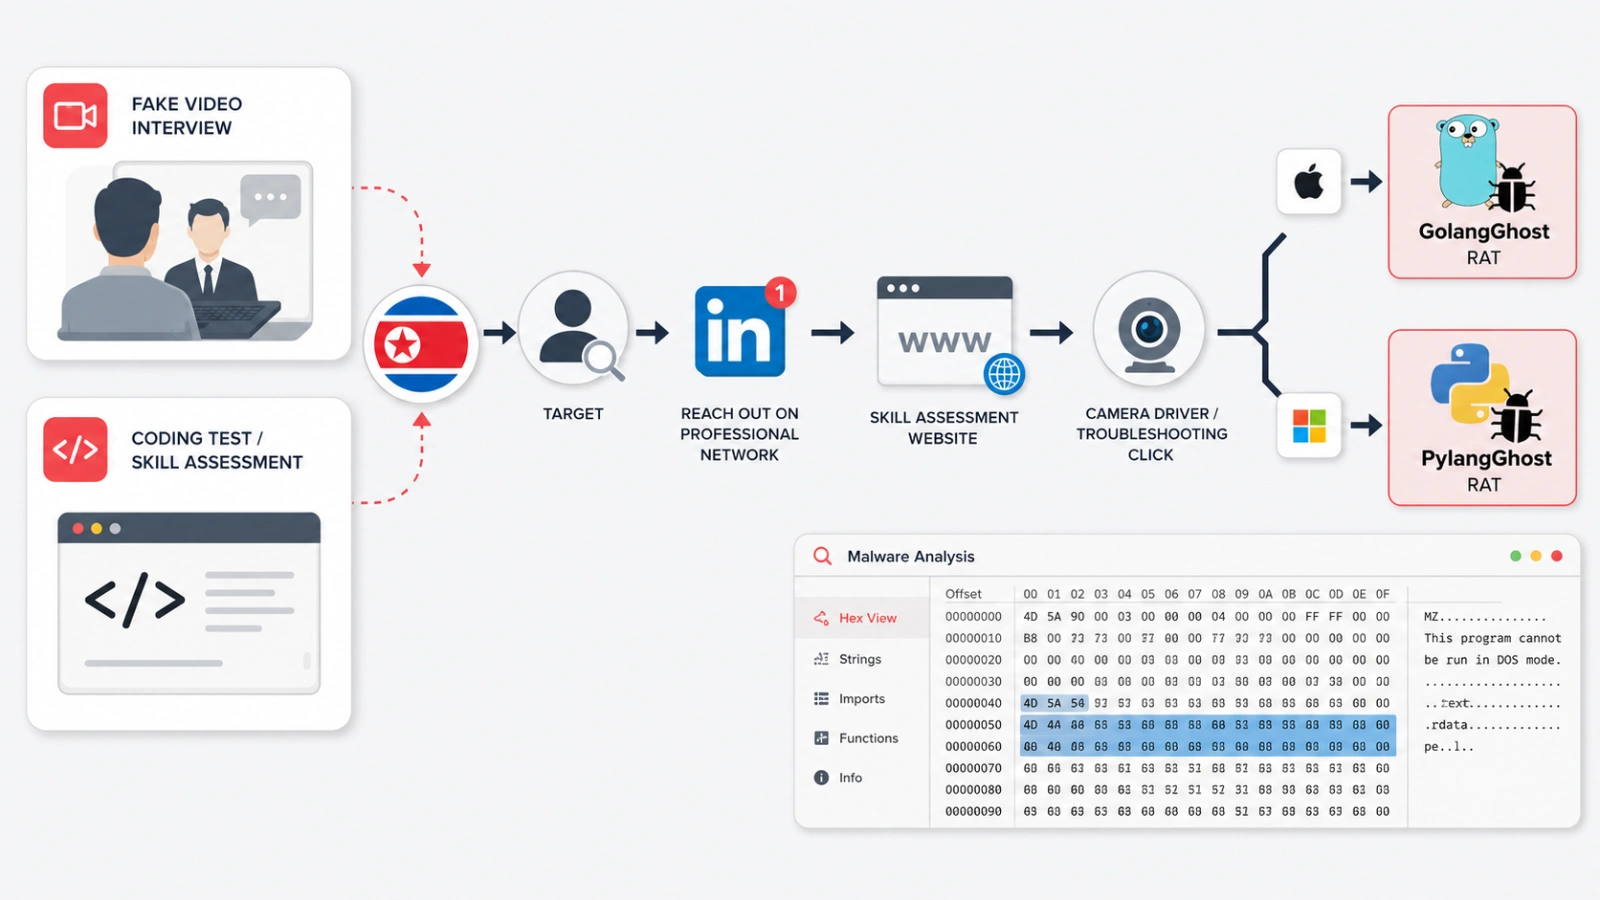

North Korea’s Famous Chollima threat group, also tracked as Wagemole, is actively running a sophisticated cyberespionage campaign dubbed ClickFake Interview.
The operation targets cryptocurrency and Web3 professionals, tricking candidates into executing terminal commands that infect their devices with platform-specific Remote Access Trojans (RATs): PylangGhost on Windows and GolangGhost on macOS.
Detailed analysis by the SOCRadar Threat Research Unit highlights how the threat actor has industrialized fake recruitment workflows to establish initial access for financial theft and espionage.
North Korean Hackers Use Fake Job Interviews
The attack initiates on social media platforms like LinkedIn and X, where operators pose as recruiters representing well-known Web3 firms such as Coinbase, Robinhood, Uniswap, and Archblock.
After engaging candidates, the fake recruiters direct them to complete a staged “skills assessment” on a fraudulent web portal.

Upon completing the test, targets are invited to a video interview on a spoofed meeting platform styled after legitimate hiring software like Willo. During the call, candidates are prompted to authorize camera and microphone permissions.
When the platform simulates a device failure, the candidate is instructed to run a terminal command to “update camera drivers” leveraging the well-known ClickFix social engineering vector. This tactic reflects broader ClickFix threat trends expanding across corporate endpoints.
Executing the terminal command triggers a platform-tailored infection:
- PylangGhost (Windows): A Python-based RAT compiled into native libraries to evade signature detection.
- GolangGhost (macOS): A Go-based backdoor sharing functional parity with PylangGhost for remote access, persistence, and file management.

Both RATs systematically harvest credentials, credential stores, and session cookies from over 80 popular browser extensions. High-value targets include password managers like 1Password and NordPass alongside crypto wallets like MetaMask and Phantom.
According to SOCRadar Threat Research, On macOS endpoints, the backdoor may deploy an auxiliary SwiftUI credential harvester to capture system login credentials. Earlier campaign waves also integrated an intermediate module called FROSTYFERRET to assist in live credential capture.
The ClickFake Interview operation represents a direct evolution of the long-running Contagious Interview campaign (also tracked as DeceptiveDevelopment or DEV#POPPER), attributed to North Korea’s Reconnaissance General Bureau under the Lazarus Group umbrella.

| Operational Component | Implementation Strategy | Target Impact |
| Recruitment Pretext | Spoofed LinkedIn profiles & fake job portals | Builds high trust with Web3 talent |
| Interview Lure | Generative AI video filters & stolen identities | Obscures attacker identity in real-time calls |
| Payload Delivery | ClickFix terminal command execution | Bypasses traditional browser download security |
| Target Extension Scope | 80+ extensions (1Password, MetaMask, Phantom) | Exfiltrates crypto keys & session tokens |
Recent telemetry indicates that over 230 tech professionals were targeted in fake job interview attacks during recent months alone.
Operators have increasingly adopted AI-generated video filters and stolen candidate identities to pass live video screenings, aligning with broader Lazarus macOS targets across the fintech landscape.
Recommended Defensive Mitigations
To neutralize recruitment-themed social engineering tactics, organizations and job seekers should enforce strict operational safeguards:
- Reject Terminal Instructions: Treat any requirement to execute terminal commands during a hiring assessment as an immediate security breach attempt.
- Restrict Endpoint Scripting: Enforce strict script execution and execution-policy controls on endpoints used by recruiters, developers, and HR staff.
- Vet Browser Extensions: Implement centralized extension whitelisting to limit credential theft from browser memory and local session stores.
- Monitor Endpoint Indicators: Configure EDR solutions to alert on unexpected process execution originating from terminal shells following web browser sessions.
𝗔𝗜 𝗦𝗢𝗖 𝘃𝘀 𝗠𝗗𝗥 𝘃𝘀 𝗠𝗦𝗦𝗣 Which is Best in 2026? Compare costs, Automation, and response: Download Free Guide


