
OceanLotus APT has executed a precision supply‑chain operation that implanted its SPECTRALVIPER backdoor into FireAnt MetaKit, a popular Vietnamese market‑data component.
Telemetry collected from mid‑2024 through early 2026 shows OceanLotus (aka APT32) conducting two distinct campaigns: a long‑running espionage intrusion against a Vietnamese infrastructure and transport construction company, and a targeted supply‑chain compromise of FireAnt MetaKit used by stock investors.
Both campaigns relied on SPECTRALVIPER and reveal a refined toolbox and careful campaign tailoring.
The FireAnt attack began in October 2025 when malicious payloads were served from FireAnt MetaKit’s legitimate update URL. Initial samples appear to be test iterations; subsequent, heavily obfuscated downloaders used new infrastructure and a campaign‑specific C2 domain, financemachinelearning[.]com, clearly chosen to blend with investor traffic.
The update mechanism lacked integrity checks and used unencrypted HTTP for both version metadata and binaries, enabling the attacker to substitute malicious updates.
The downloader performed basic host reconnaissance, POSTed profiling data to a staging server, and requested a next‑stage payload before deploying a side‑loading chain.
The side‑load involved deploying DtlCrashCatch.dll (a SPECTRALVIPER loader) alongside IntelAudioService.exe, a renamed copy of a legitimately signed dtlupdate.exe.
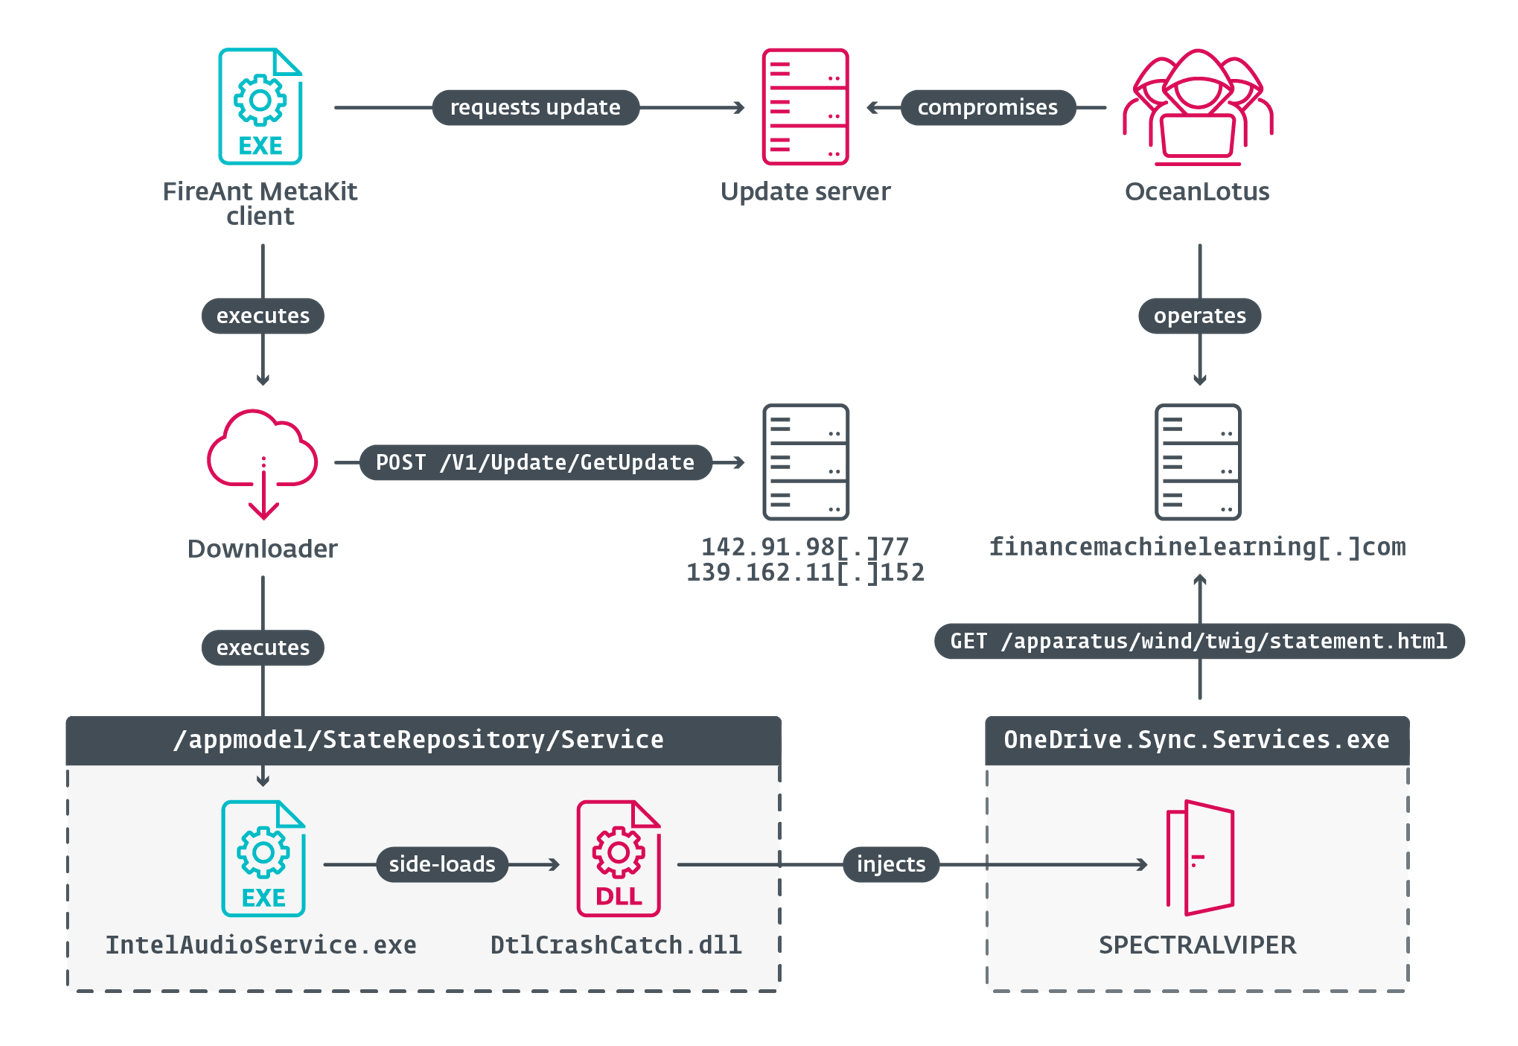
DtlCrashCatch.dll injected into OneDrive.Sync.Service.exe, after which SPECTRALVIPER beacons to HTTPS C2 endpoints embedding encrypted host information inside an HTTP Cookie header (notably using the zd_cs_pm= prefix in this campaign).
OceanLotus Targets Stock Investors
Observed staging hosts migrated over time from 139.162.11[.]152 to 142.91.98[.]77; since March 9, 2026 no further malicious updates were detected, suggesting the operation has likely ceased or been disrupted.
According to ESET, OceanLotus maintained a sustained intrusion against a major infrastructure and transport construction firm from mid‑2024 to February 2026.
The deployments show orchestration differences across the environment, consistent with tailored implants adapted to host roles.
That campaign used multiple SPECTRALVIPER variants, side‑loaded via legitimate signed executables (Toolbox.exe variants) and likely leveraged RCE exposures on public SQL servers for initial access.
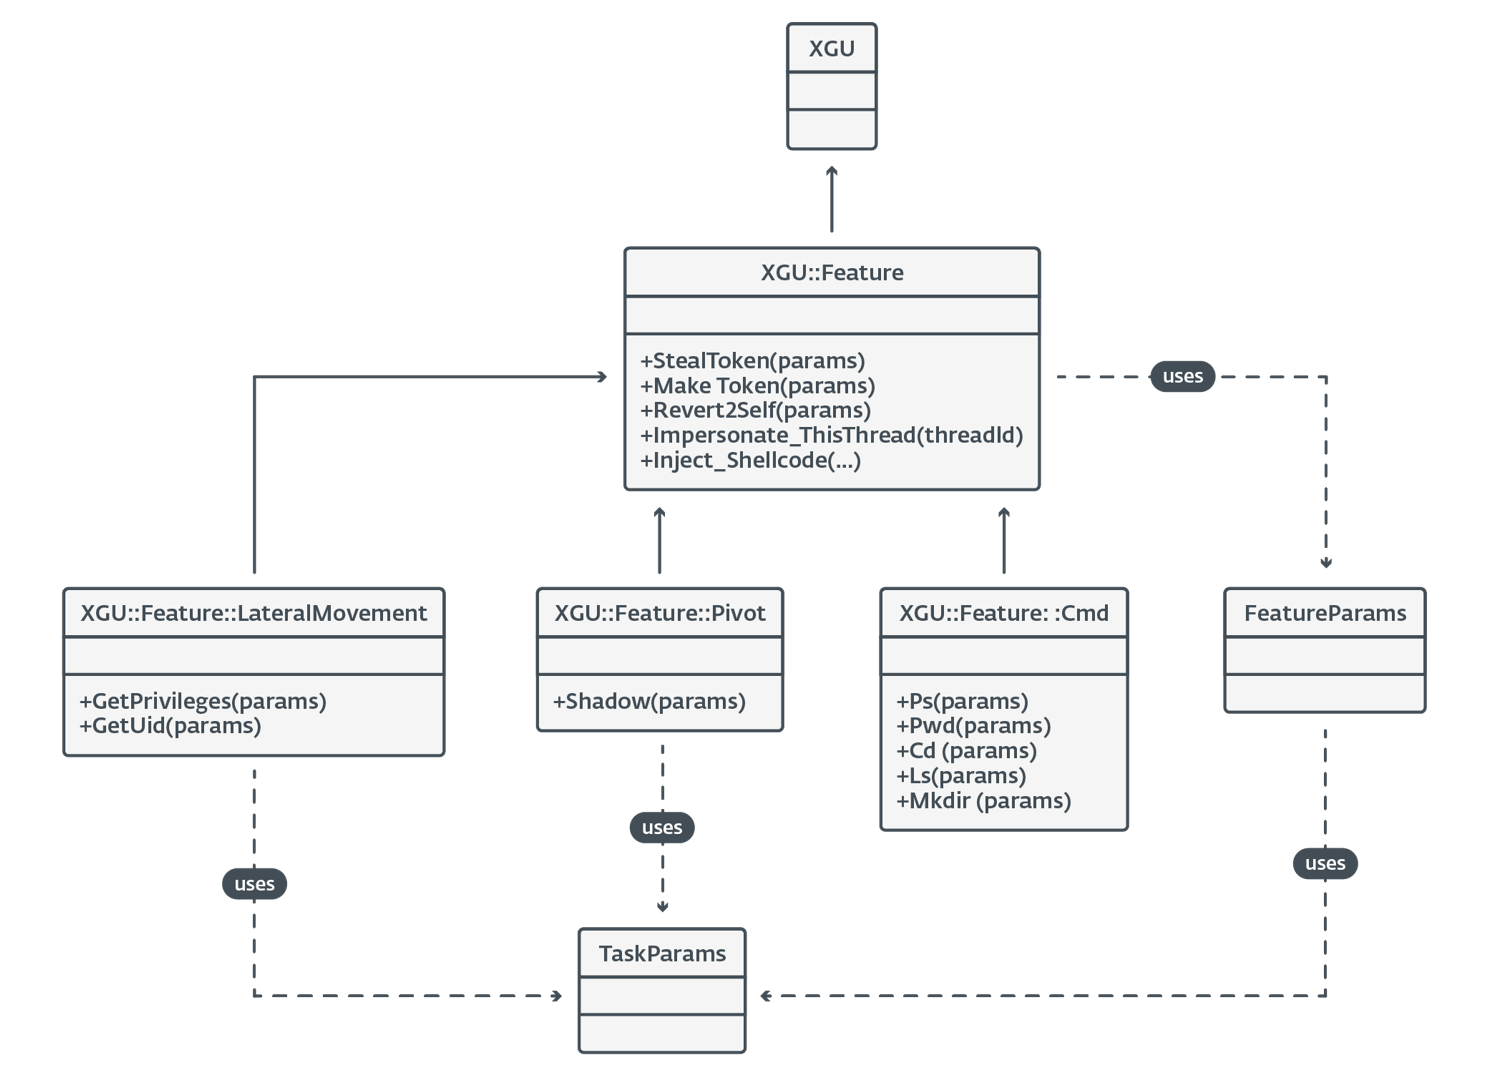
A consequential OPSEC lapse left RTTI symbols in two SPECTRALVIPER samples, enabling researchers to reconstruct parts of the malware’s internal class hierarchy. SPECTRALVIPER operates as an HTTPS‑based active backdoor.
An orchestration model: designated orchestrator instances relay commands to other compromised hosts through named pipes (methods like XGU::Pivot::StartLink and XGU::Pivot::Internal::WaitNew_RemotePipe were recovered).
The backdoor also functions as a loader, able to inject additional binaries or shellcode via ProcessReflector and ProcessManager components.
C2 domains observed across incidents (gatewayrvcenter[.]com, coachcybersecurity[.]com, mxprodesign[.]com, power-sync-services[.]com) indicate campaign‑specific naming strategies to camouflage traffic.
Contextually, this operational focus aligns with Vietnam’s intensified anti‑corruption and financial investigations (notably the “Blazing Furnace” campaigns and regulatory scrutiny of bond misreporting in late 2025).
The FireAnt compromise’s timing and choice of target strongly suggest the activity supported domestic financial‑crime investigations or surveillance objectives rather than indiscriminate theft or broad commercial espionage.
Since exposed in 2020 and then resurfacing with SPECTRALVIPER in 2023, OceanLotus appears to have shifted toward more selective, domestically oriented operations while retaining sophisticated tooling and the capacity for stealthy supply‑chain compromises.
Defenders should audit update channels for integrity and encryption, monitor for suspicious side‑loading of signed binaries, and hunt for SPECTRALVIPER indicators such as HTTP cookie‑prefixed beacons and named‑pipe orchestration artifacts.
IOCs
| IP | Domain | Hosting provider | First seen | Details |
| 38.60.245[.]37 | leadingfilipinoteams[.]com | Kaopu Cloud HK Limited | 2025‑10‑05 | SPECTRALVIPER C&C server. |
| 139.99.33[.]239 | coachcybersecurity[.]com | OVH Singapore PTE. LTD | 2025‑09‑20 | SPECTRALVIPER C&C server. |
| 139.162.11[.]152 | N/A | Akamai Connected Cloud | 2025‑10‑02 | SPECTRALVIPER hosting server. |
| 139.180.128[.]42 | gatewayrvcenter[.]com | IRT‑CHOOPALLC‑AP | 2025‑09‑20 | SPECTRALVIPER C&C server. |
| 142.91.98[.]77 | N/A | LEASEWEB SINGAPORE PTE. LTD. | 2025‑12‑03 | SPECTRALVIPER hosting server. |
| 166.88.77[.]186 | mxprodesign[.]com | Evoxt Enterprise | 2025‑06‑23 | SPECTRALVIPER C&C server. |
| 194.68.26[.]241 | financemachinelearning[.]com | M247 Europe SRL | 2025‑10‑30 | SPECTRALVIPER C&C server. |
Note: IP addresses and domains are intentionally defanged (e.g., [.]) to prevent accidental resolution or hyperlinking. Re-fang only within controlled threat intelligence platforms such as MISP, VirusTotal, or your SIEM.
Follow us on Google News, LinkedIn, and X to Get Instant Updates and Set GBH as a Preferred Source in Google.


