

Researchers at Resecurity noticed threat actors leveraging Open Redirect Vulnerabilities which is popular in online services and apps to evade spam filters to deliver phishing content. Trusted service domains like Snapchat and other online services make special URLs that lead to malicious resources with phishing kits.
The kit identified is named ‘LogoKit’ that was earlier used in attacks against Office 365, Bank of America, GoDaddy, Virgin Fly, and other financial institutions and online services.
LogoKit – Phishing Kit
LogoKit is well-known for its dynamic content generation using JavaScript. It can change logos of the impersonated service and text on the landing pages in to adapt on the fly. Therefore, the targeted victims will possibly interact with the malicious resource.
The analysis says in November 2021, there were more than 700 identified domain names used in campaigns leveraging LogoKit and it goes on to increase.
Researchers say in this case, the actors choose to use domain names in exotic jurisdictions with relatively poor abuse management process – .gq, .ml, .tk, ga, .cf or to gain unauthorized access to legitimate WEB-resources, and then use them as hosting for further phishing distribution.
LogoKit operators send victims a personalized, specially crafted URL containing their email address. Once a victim navigates to the URL, LogoKit fetches the desired company logo from a third-party service, such as Clearbit or Google’s favicon database.
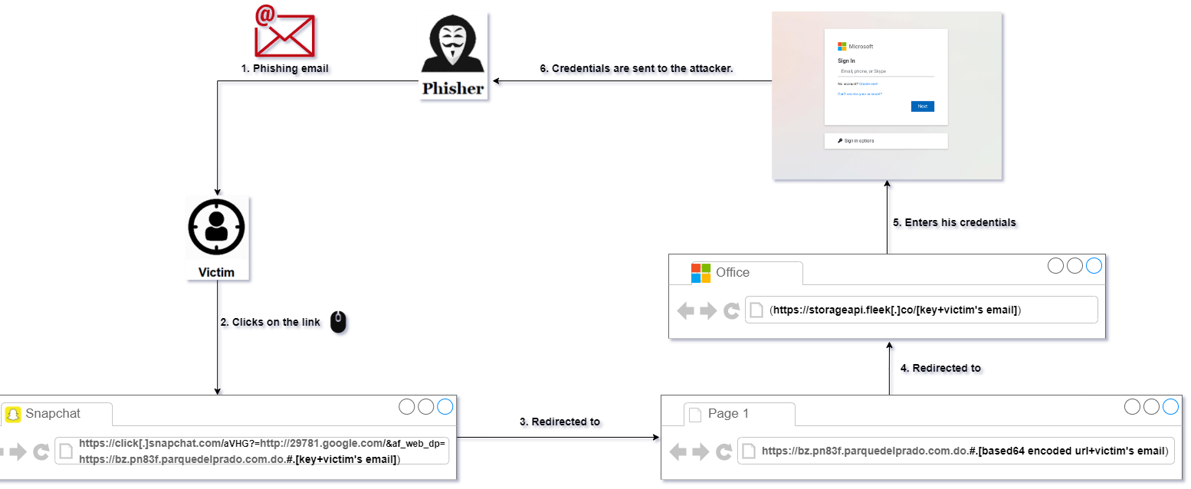
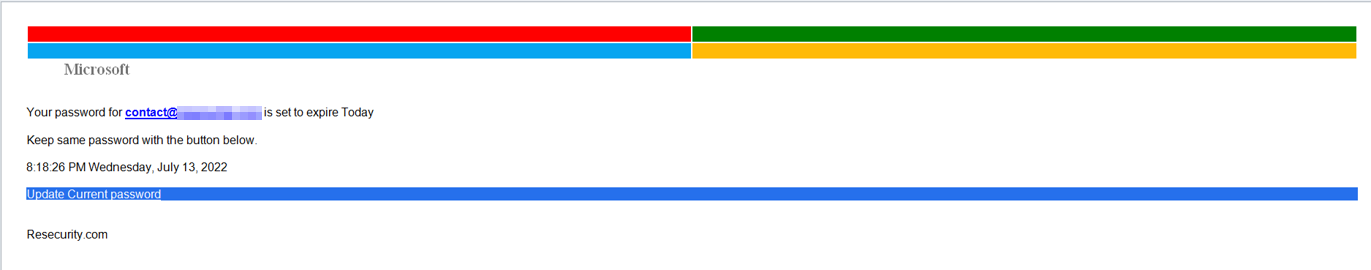
The embedded link is leveraging Open Redirect Vulnerability in Snapchat, and another URL from Google leads to a phishing resource.
The victim email is also auto-filled into the email or username field, tricking victims into thinking it’s a familiar site they’ve already visited and logged into. LogoKit performs an AJAX request sending their email and password to an attacker-owned server before finally redirecting the user to the corporate website they intended to visit when clicking the URL.
The threat actors without the need for changing templates, the LogoKit script itself will assist to embed malicious scripts or host attacker infrastructure.
“Unfortunately, the use of Open Redirect vulnerabilities significantly facilitates LogoKit distribution, as many (even popular) online-services don’t treat such bugs as critical, and in some cases – don’t even patch, leaving the open door for such abuse”, Resecurity
You can follow us on Linkedin, Twitter, Facebook for daily Cybersecurity and hacking news updates.







