

A new wave of infostealer activity targeting OpenClaw, an emerging AI assistant platform. The discovery marks a major turning point in the behavior of infostealer malware moving beyond browser and cryptocurrency theft to focus on AI configuration environments that hold deep digital identities and sensitive metadata.
Hudson Rock detected a live infection where an infostealer successfully exfiltrated the victim’s OpenClaw workspace and configuration files, including key components such as openclaw.json, device.json, and soul.md.
These files collectively define the AI assistant’s personality, access tokens, and cryptographic keys essentially the “soul” of the user’s AI ecosystem.
Interestingly, the malware responsible for the breach lacked a dedicated OpenClaw-specific module. Instead, it used a broad file-harvesting routine designed to capture files from sensitive directories (such as .openclaw) and to grab extensions associated with secrets or tokens.
This generic technique inadvertently captured an entire AI configuration environment, revealing a new layer of valuable intelligence for cybercriminals.
Hudson Rock notes that as AI assistants increasingly integrate into professional and personal workflows, threat actors will likely develop targeted modules designed to parse OpenClaw environments similar to how they currently decrypt Chrome or Telegram data.
This progression underscores the escalating convergence between AI automation and traditional credential theft.
What the Attackers Stole
The first file retrieved, openclaw.json, serves as the central configuration file of the victim’s AI agent. It contained user identifiers, workspace paths, and a sensitive gateway authentication token.
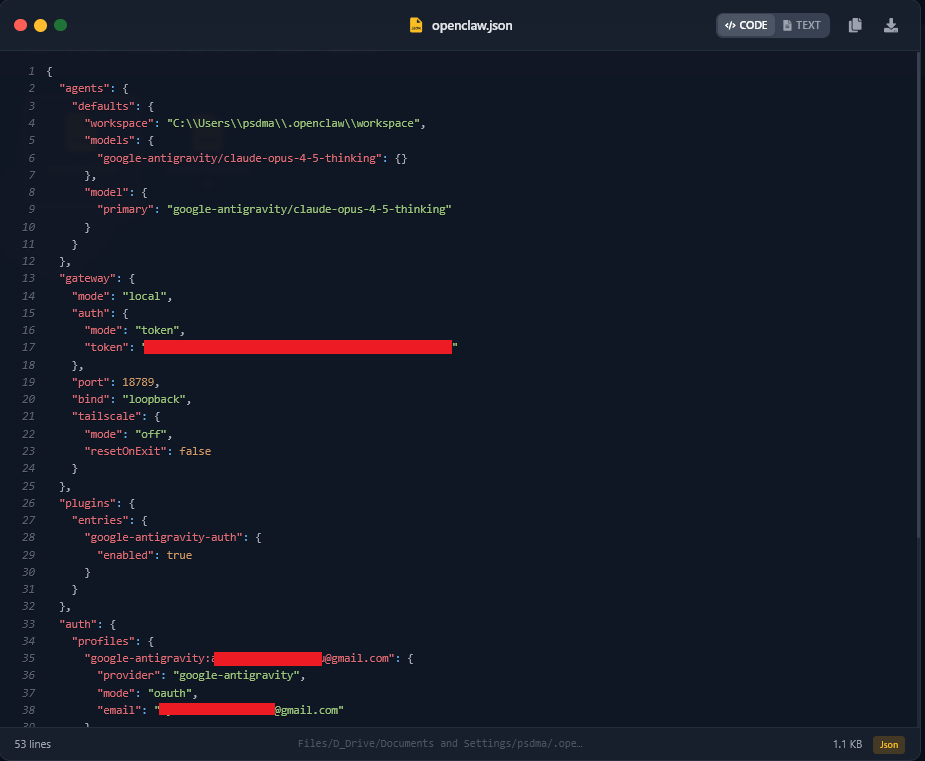
According to Hudson Rock, this token could allow attackers to remotely access or impersonate the victim’s local OpenClaw instance, posing a severe account takeover risk.
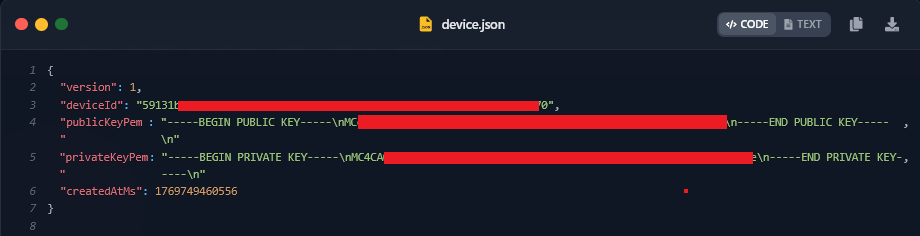
The second file, device.json, exposed the victim’s private and public cryptographic keys, which are used to authenticate and sign operations between devices in the OpenClaw ecosystem.
Possession of these keys could enable attackers to spoof trusted devices, decrypt communications, or sign malicious commands as the legitimate user.
Cryptographic file contains the publicKeyPem and, crucially, the privateKeyPem of the user’s device.
The third exfiltrated file, soul.md, revealed personal behavioral data and memory logs defining how the user’s AI assistant interacts with their daily routine including personal communications, schedules, and activity records.
These files effectively grant attackers an intimate view into the victim’s digital life, merging personal, contextual, and cryptographic compromise into a single breach.
AI Identity Theft on the Rise
Hudson Rock’s AI risk analysis system, Enki, performed an assessment of the exfiltrated data, concluding that the combination of tokens, keys, and personal context could enable an attacker to orchestrate a total identity compromise.
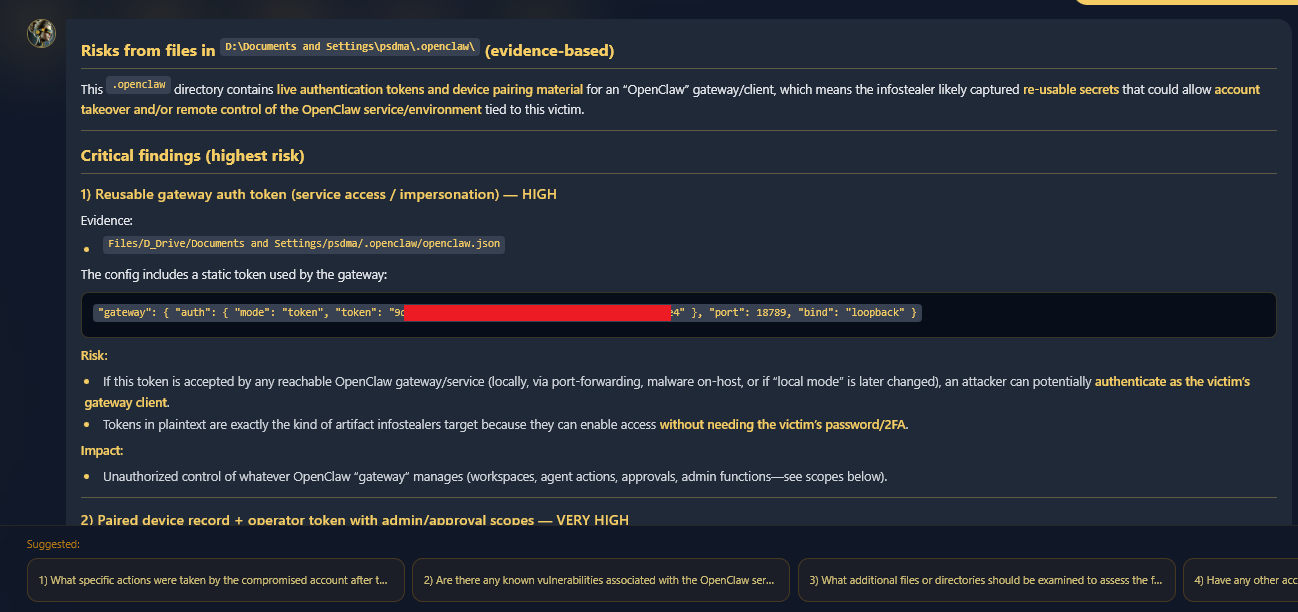
Beyond login theft, this could extend to impersonation of AI agents, unauthorized actions on the victim’s behalf, or manipulation of AI-driven workflows.
As AI platforms like OpenClaw, GPT-based agents, and other personal models evolve, the value of their configuration files will continue to rise.
This incident illustrates a new frontier in cybersecurity: AI identity theft. Infostealers are no longer after passwords alone they are targeting the contextual backbone of digital lives.
By stealing OpenClaw configurations, attackers gain not just access credentials, but insight into an individual’s habits, communications, and automated behaviors.
Hudson Rock warns that this will likely inspire the creation of specialized “AI-stealer” malware families aimed at parsing and exploiting the next generation of digital assistants.
Follow us on Google News, LinkedIn, and X to Get Instant Updates and Set GBH as a Preferred Source in Google.






%20(1)%20(1).jpg?fit=1600,900&ssl=1&description=A new wave of infostealer activity targeting OpenClaw, an emerging AI assistant platform. The discovery marks a major turning point in the behavior of infostealer malware.)