

IT giant Oracle, on 1st November 2020, issued a Security Alert Advisory, CVE-2020-14750, regarding a remote code execution vulnerability on Oracle WebLogic Server. Oracle WebLogic Server is a Java EE application server. The latest version being WebLogic Server 14c(14.1.1) released on March 30, 2020.
Security Alert Advisory
The Security Alert offers recommendations to the vulnerability which pertains to CVE-2020-14882, addressed in October 2020, Critical Patch Update, which was remotely exploitable without any authentication. Oracle strongly recommends the users to apply the updates at the earliest.
Affected products
The affected product is the Oracle WebLogic Server wherein the following versions are affected:
10.3.6.0.0, 12.1.3.0.0, 12.2.1.3.0, 12.2.1.4.0, 14.1.1.0.0
You may take a look at the risk matrix provided by Oracle which helps to understand the versions supported.
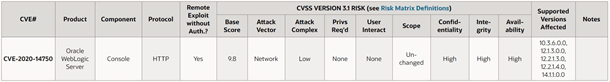
Security alerts: Applicable Product and Version
The patches proposed in the Oracle Security alert is applicable for all the product versions which is covered under the Premier Support or Extended Support phase of the Lifetime Support Policy.
The Product releases that are not under Premier Support or Extended Support are not tested for the presence of vulnerabilities addressed by this Security Alert. However, it is likely that earlier versions of affected releases are also affected by these vulnerabilities.
Attention to the Security Alert
The Cybersecurity and Infrastructure Security Agency (CISA) also published an alert on 2nd November 2020 bringing the attention of users to this patch.
“Oracle has released an out-of-band security alert to address a remote code execution vulnerability—CVE-2020-14750—in Oracle WebLogic Server. A remote attacker can exploit this vulnerability to take control of an affected system.” – CISA
A quick search on Spyse, a cybersecurity search engine, reveals that there are approximately 3000+ Oracle WebLogic Servers accessible over the public internet and are vulnerable to CVE-2020-14882.
The attackers have definitely resorted to tricks instead of treats, this scary Halloween!!
You can follow us on Linkedin, Twitter, Facebook for daily Cybersecurity and hacking news updates.
Also Read
Oracle Warns Active Exploitation of Recently Patched WebLogic RCE Flaw
Oracle Critical Patch Update Addresses 405 New Security Vulnerabilities – April 2020







