

A prototype version of the Package Analysis tool has been recently released by the Open Source Security Foundation (OpenSSF), and it is the first of its kind to be published.
Using this tool, you can identify malicious attacks against open source registries in real-time and counter them. A short period of time after its release on GitHub, this tool identified more than 200 malicious packages using npm and PyPI in a pilot run that lasted less than a month.
This project analyses the packages found in open source repositories to find out:-
- How do they behave?
- What capabilities do they have?
- What files do they access?
- What addresses do they connect to?
- What commands do they run?
Robust Tool to Scan open-source Repositories
This repository houses tools which are used to analyze open-source software packages, in particular, malware in the following packages:-
- npm packages
- PyPI packages
As a result of this effort, open-source software will be better protected through the following reporting:-
- Detecting malicious behavior.
- Informing consumers selecting packages.
- Providing researchers with data about the ecosystem.
There is one malicious package that has been identified by Package Analysis among all the suspect packages: ‘colorsss’. While this package has been found to be formerly deemed malicious.
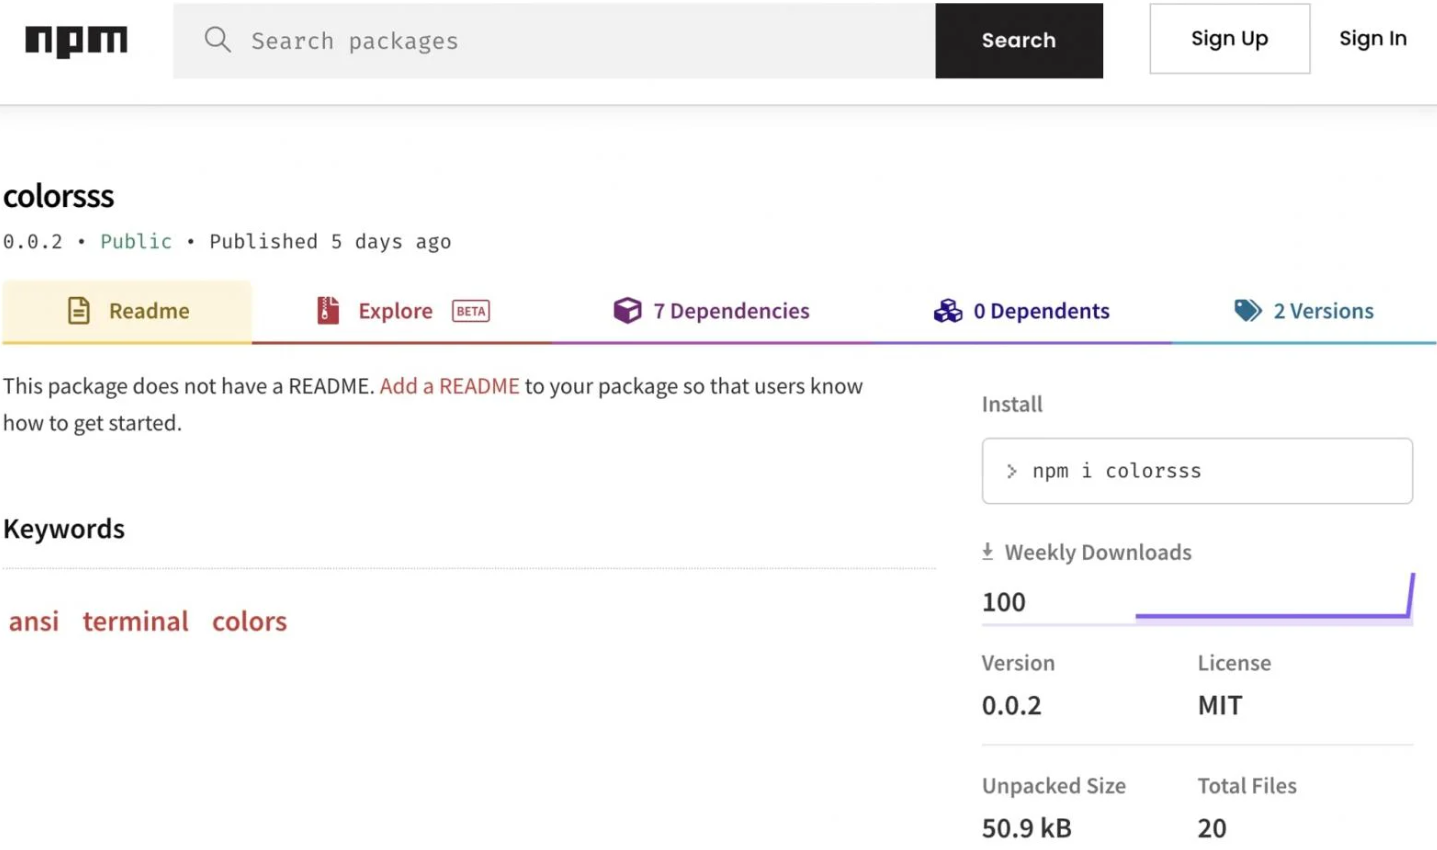
Almost all of the packages that have been found contain a simple script that runs and requests a few details about the host from home during an installation process.
In most cases, these packages are created by security researchers looking to find bug bounties as part of a bug bounty program.
There is no attempt to conceal their behavior, and the majority of them are capable of extracting meaningful information from the system like:-
- Name of the machine/system
- Username
Future Goals
Here below we have mentioned all the future goals of the Package Analysis tool:-
- The ability to detect changes in package behavior over time.
- The packaging analysis results can be processed automatically after they have been received.
- In order to maintain long-term analysis of the stored packages, they are stored themselves as they are processed.
- The pipeline will gain greater reliability by improving its efficiency of the pipeline.
You can follow us on Linkedin, Twitter, Facebook for daily Cybersecurity and hacking news updates.


, and it is the first of its kind to be published.)