Google added a new in-built feature in the Chrome browser that alerts you during sign in the non -Google access if your password ever been hacked or it was a part the data breach.
Earlier this year Chrome introduced a password checkup extension in the Chrome web store now Google integrated this extension feature in chrome and name it as “Password Leak Detection”.
Very recently Mozilla added this same feature in chrome with the name of Firefox monitor that integrated with haveibeenpwned breach database that it let you know the whether your email Address was compromised or not if you enter your email address in the search field.
This new feature in chrome not only alert you but also suggest and save strong passwords on particular sites.
Inbuilt Chrome “Password Leak Detection” feature available in the latest Chrome 78 Canary.
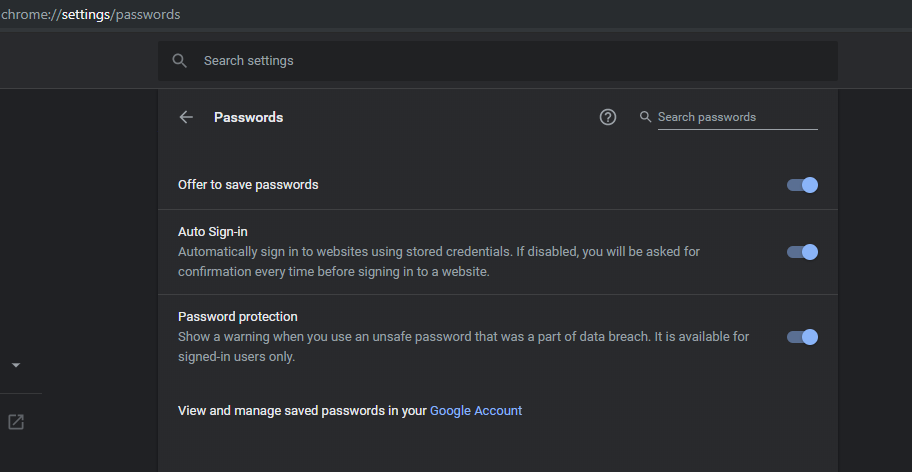
Google also integrate this feature with a password manager that alerts you whenever users try to set a weak password and the settings in the Chrome says “ Show a warning when you use an unsafe password that was a part of data breach. It is available for signed-in users only.”
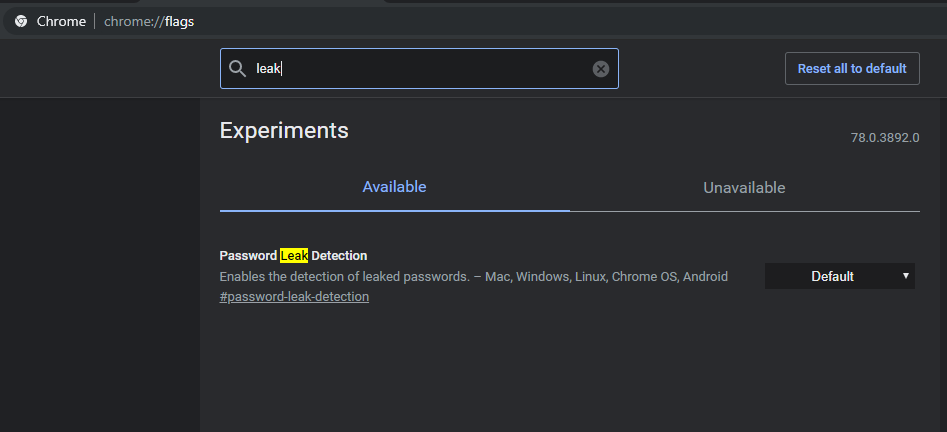
You can enable this Password Leak Detection feature in Chrome 78 canary for all the platform including Mac, Windows, Linux, Chrome OS, Android.
You can find the feature in Chrome 78 canary by following these steps that suggested by techdows,
1. Visit chrome://flags
2. Search for “leak” password, for “Password leak detection” experimental feature
After enabling the Password leak Detection, Browser requires to reset and the new feature available.
You can follow us on Linkedin, Twitter, Facebook for daily Cybersecurity and Hacking New updates.
Attackers abused compromised ConnectWise Cloud Backup credentials to access Microsoft 365 customer environments, prompting ConnectWise…
Anthropic says an internal Claude research model reconstructed how the National Security Agency generated seeds…
Two WordPress Core vulnerabilities can be chained to execute remote code without authentication, according to…
A newly disclosed OpenBSD kernel exploitation chain combines a shared memory accounting flaw with a…
GhostAction attackers have expanded their GitHub credential theft campaign with a second stage that disguises…
Indian authorities have warned that SideCopy hackers are targeting Indian organizations, including academic institutions, with…