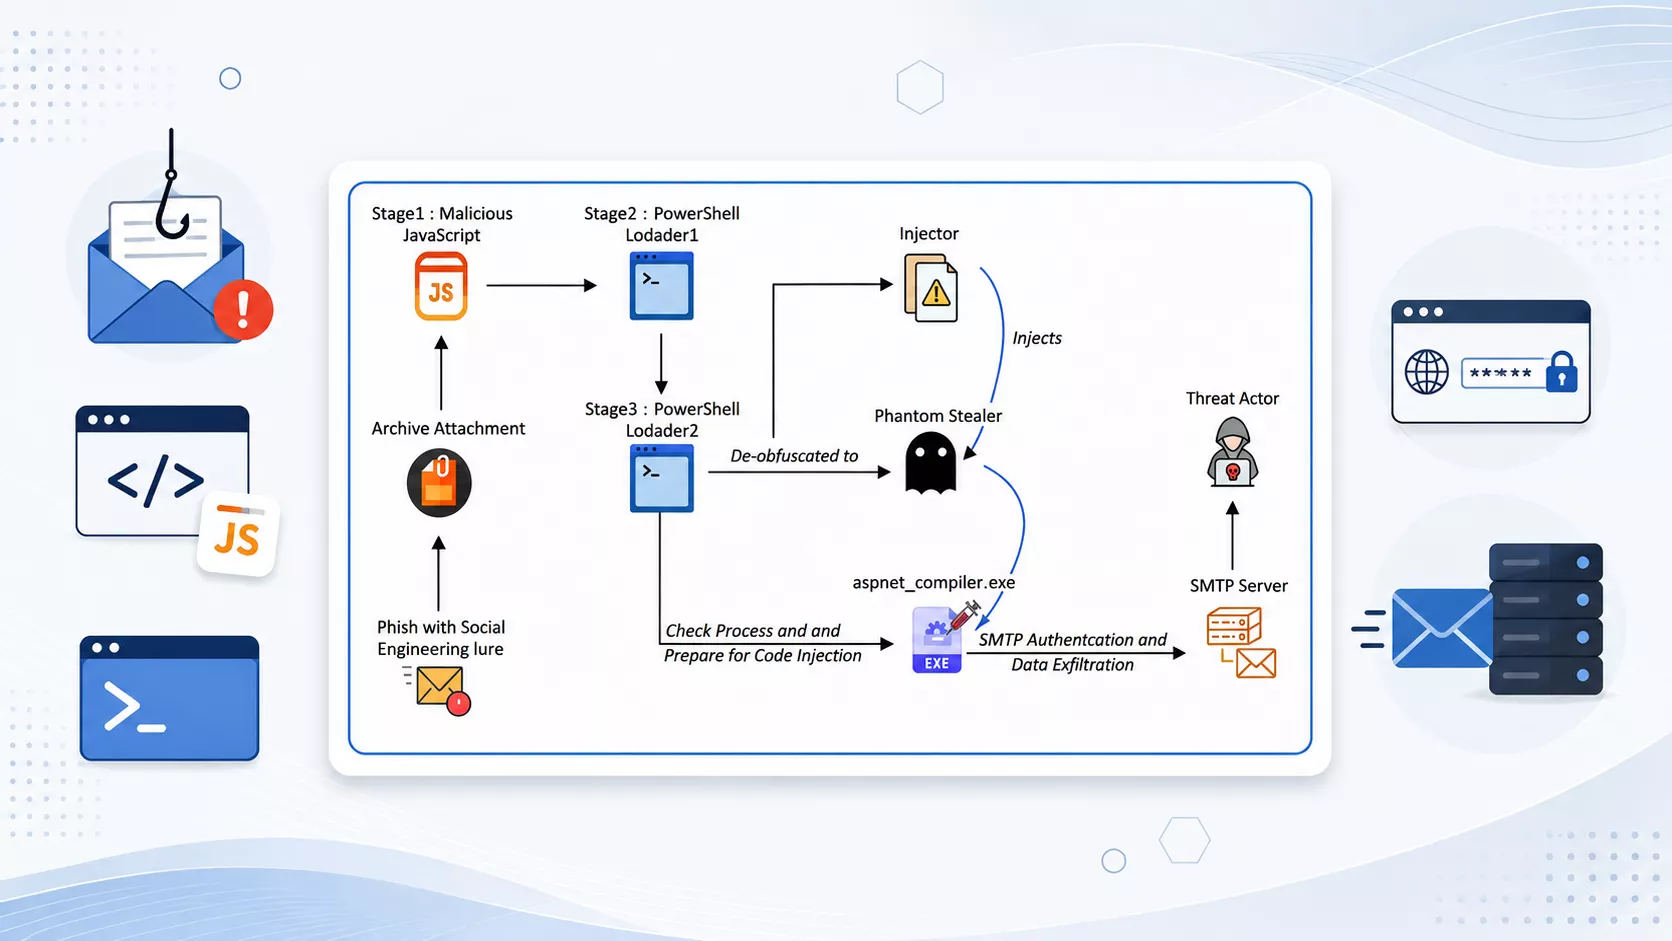

A sophisticated phishing campaign that disguises malware delivery inside routine business communications, ultimately deploying Phantom Stealer v3.5.0 to harvest browser credentials, cookies, payment data, and cryptocurrency wallet information from victims.
Documented by Seqrite, the campaign uses two distinct phishing themes that both lead to the same infection chain. One email impersonates UPS Forwarding Hub, referencing fake shipment bookings and quotation IDs to target procurement teams.
The second poses as an official notice from Malaysia’s Inland Revenue Board (LHDN), written in Malay and demanding tax documentation within a 14-day deadline to pressure finance staff.
Both emails deliver a compressed archive containing a malicious JavaScript file with business-relevant filenames like “UPS Docs_Shipment Number 3264010420.js,” designed to blend into normal workflows and avoid suspicion.

Phantom Stealer Campaign
Once executed, the obfuscated JavaScript acts purely as a loader.
- Stage 1: It uses string-array obfuscation and indirect function calls to hide its true purpose, then decodes an embedded Base64 blob containing a PowerShell script, writes it to a temporary
.ps1file, and launches it via hiddenpowershell.exeparameters. - Stage 2: PowerShell decrypts an AES-encrypted payload (key and IV embedded as Base64 strings), then runs it in memory using
Invoke-Expression, avoiding disk writes. - Stage 3: A second PowerShell loader unpacks two payloads: an XOR-encrypted .NET “injector” assembly (key: “DEVILboy56@@”) and a raw byte-array PE file matching the Phantom Stealer executable. The injector reflectively loads and injects the stealer into a legitimate process,
aspnet_compiler.exe. - Stage 4: Phantom Stealer v3.5.0 executes entirely in memory, harvesting data before exfiltration.
This layered design keeps each component hidden until runtime, making static analysis significantly harder and reducing the malware’s on-disk footprint.

Phantom Stealer targets a wide range of sensitive data, organizing stolen information into categorized files such as Chromium_passwords, Chromium_credit_cards, Chromium_cookies, Gecko_passwords, and Gecko_cookies, each named with the victim’s hostname. The malware also targets cryptocurrency wallets and messaging app data stored locally on the compromised host.
For exfiltration, it connects to an SMTP server over port 587, authenticates via Base64-encoded AUTH LOGIN credentials, with one observed username decoding to ruhi@aktekmetal[.]com[.]tr, and then upgrades the connection with STARTTLS to encrypt the transmission.
This approach allows the stolen data to blend in with legitimate outbound email traffic before the session closes cleanly with a standard QUIT command, leaving minimal trace of anomalous network behavior.
Prashil Moon found no conclusive link to a specific threat actor, and Phantom Stealer appears to be commodity malware used by multiple operators across the cybercriminal ecosystem.
Organizations should treat unexpected shipment, banking, or tax-related attachments with caution, restrict unnecessary script execution where possible, and monitor for anomalous PowerShell activity, reflective memory loading, process injection, and unusual SMTP traffic.
A defense-in-depth approach that combines email security, endpoint monitoring, and network visibility remains critical to catching these multi-stage, fileless attacks before sensitive data is compromised.
IOCs
| Type | Value |
|---|---|
| Hash | 6BBFC88534D5D515DDDB0EC9BB618530 |
| Hash | 8A620E451E64F418BC21FD458E952F2E |
| Hash | 5F238710A5EF4F6DDBBE7A118C822705 |
| Hash | a30b628d0c087f305b35be3e3f5281b3 |
| Hash | 34bfa888695b9aaa41bd575245972043 |
| Seqrite Detection | Trojan.Injector.S39585891 |
| Seqrite Detection | Trojan.YakbeexMSIL.ZZ4 |
| Seqrite Detection | PS.Trojan.Loader.50921.GC |
| Seqrite Detection | Js.Trojan.Loader.50922.GC |
Note: IP addresses and domains are intentionally defanged (e.g., [.]) to prevent accidental resolution or hyperlinking. Re-fang only within controlled threat intelligence platforms such as MISP, VirusTotal, or your SIEM.
ALERT: 20+ government sites delivered malware to businesses and citizens. See full attack research to check your own exposure.


