

The Dutch National Police in cooperation with cybersecurity firm Responders.NU, managed to obtain over 150 decryption keys from ransomware group ‘Deadbolt’ due to fake bitcoin payments.
“The police paid, received the decryption keys and then withdrew the payments. These keys allow files such as treasured photos or administration to be unlocked again, at no cost to victims”, according to the news release.
The DEADBOLT ransomware targets vulnerabilities in the products of well-known NAS vendor QNAP, the DEADBOLT gang aims to lock everyone else on your network out of their digital lives, and then to squeeze you for several thousand dollars to “recover” your data.
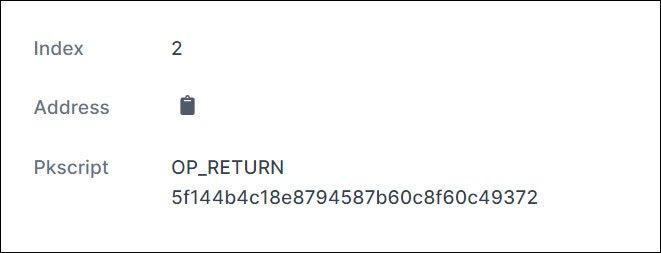
Once the ransom is paid, DeadBolt creates a bitcoin transaction to the same bitcoin ransom address containing a decryption key for the victim- the decryption key can be found under the transaction’s OP_RETURN output.
Subsequently, after the victim enters this key, it will be converted into a SHA256 hash and compared to the SHA256 hash of the victim’s decryption key and the SHA256 hash of the DeadBolt master decryption key.
Thus, if the decryption key matches one of the SHA256 hashes, the encrypted files on the NAS hard drives will get decrypted.
According to the reports, about 90% of the keys of victims that filed complaint in one of the thirteen countries were obtained. In this case, when a victim makes a ransom payment to the DeadBolt operation, the operation automatically sends a decryption key when it detects the bitcoin transaction with the exact ransom amount.
Still, the decryption key is sent immediately without waiting for a bitcoin confirmation that the bitcoin transaction is legitimate. Thus, Dutch Police and Responders.NU create ransom payments with a low fee at a time when the Bitcoin blockchain was heavily congested.
Report says the action is a nasty blow for the cybercriminals behind Deadbolt: because of the weak link in their operation they were forced to shut down their system. Specifically, they are in the crosshairs of international law enforcement authorities.
“This action clearly shows that reporting helps: victims that reported the ransomware were given priority. Their keys were among the first we obtained, before panic struck the ransomware-group.
“On top of the international victims, we were able to obtain the keys for all the Dutch victims that filed a complaint and have notified them the very evening”, Matthijs Jaspers, Cyber crime team police
Rickey Gevers, Responders.NU says, “We assist many victims of ransomware and saw an opportunity to obtain decryption keys. Through the website deadbolt.responders.nu, victims can easily check if their key is also available and follow the unlocking instructions.”
Also Read: Download Secure Web Filtering – Free E-book


