

Hackers use phishing emails to mislead recipients into providing personal data like usernames, passwords, credit card numbers, or social security numbers.
This method exploits human emotions and trust, allowing a threat actor to compromise an account, steal an identity, or disseminate malware with little technical skill.
Guardio Labs recently discovered “EchoSpoofing” which is a serious vulnerability in the Proofpoint email protection service used by 87% of Fortune 100 companies.
Through this flaw, hackers could send millions of legitimate phishing emails impersonating top famous brands such as Disney and IBM without being caught, consequently stealing money or private information from unsuspecting recipients.
How to Build a Security Framework With Limited Resources IT Security Team (PDF) - Free Guide
Proofpoint’s Email Protection
In this phishing campaign, threat actors bypassed modern email security protocols by doing the following things:-
- Creating spoofed emails on their SMTP servers
- Relaying them through misconfigured Office 365 accounts
- Exploiting Proofpoint’s permissive email flow settings
This process allowed attackers to send millions of fully authenticated phishing emails, impersonating major brands like Disney and IBM.
The emails passed SPF and DKIM checks, appearing legitimate to recipients and email security systems.
The campaign’s goal was to steal credit card information and other sensitive data through fake branded landing pages and offers.

This exploit highlights vulnerabilities in the default configurations of popular email security services, highlighting the need for stricter custom rules and better awareness of potential misconfiguration.
This refined phishing operation exploited Misconfigured Office 365 accounts and Proofpoint’s permissive settings. For two weeks, it sent out about 3 million spoofed emails every day, with a peak of 14 million.
As many as 11 server VPS clusters running on OVH were equipped with PowerMTA software that could deliver 2.88 million emails at a time.
Spoofed domains and infiltrated Office 365 accounts were frequently changed to avoid detection, and major brands such as Disney, IBM, Best Buy, and Nike were impersonated.
Though Proof Point had known since March, in May 2024, Guardio alerted it.
Together with Guardio tracing operations back, they made customer notifications, reported compromised accounts to Microsoft & VPS providers, and implemented a novel security measure using the X-OriginatorOrg header.
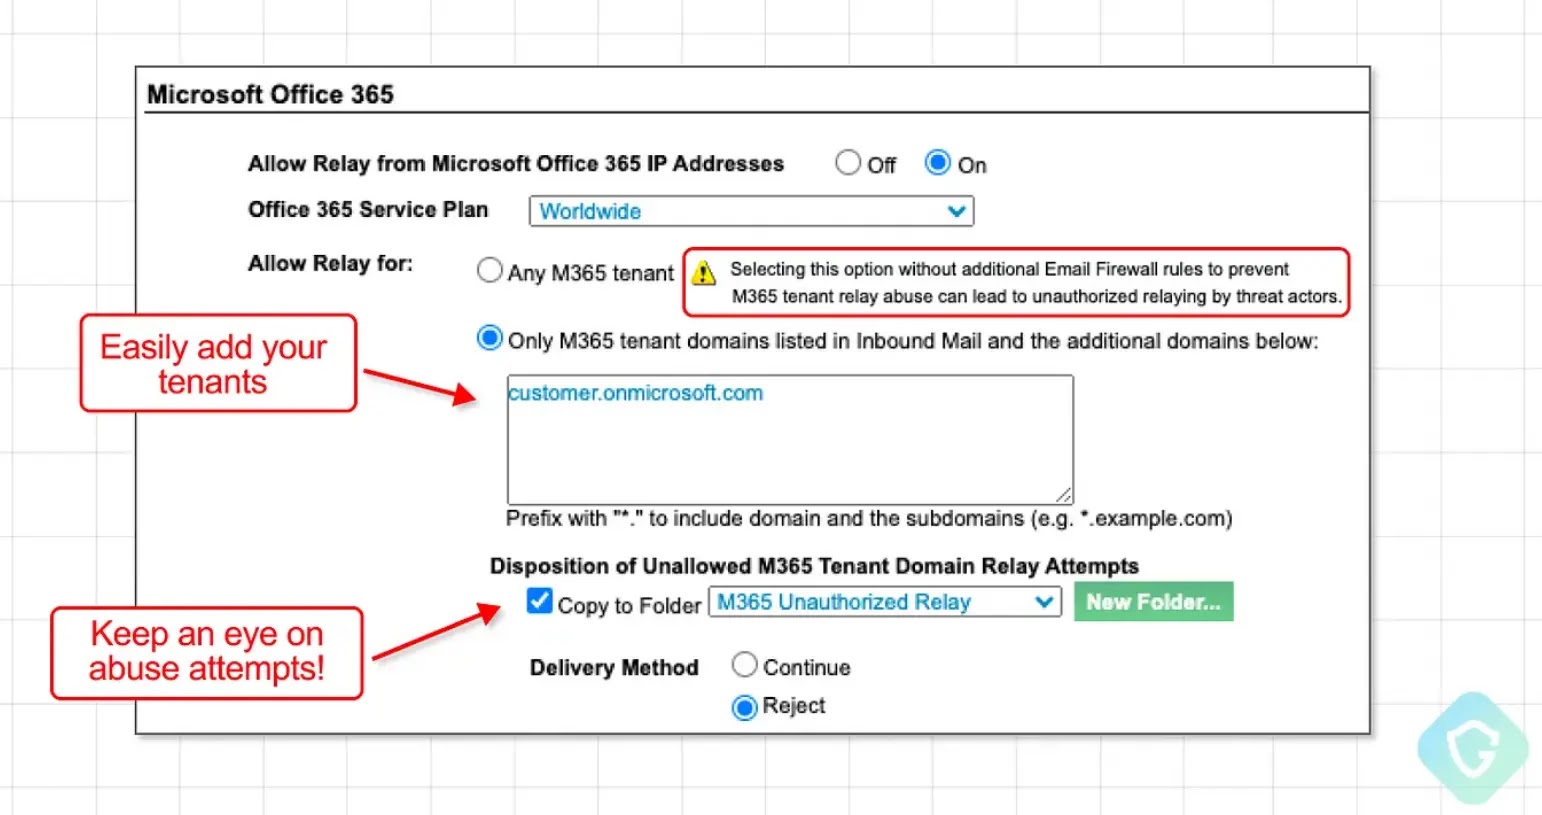
Due to this incident, Proof Point updated its admin panel to include clearer risk descriptions and approval processes, highlighting the need for stronger default security configurations in email protection services.
The campaign’s intricate nature, coupled with its wide coverage, demonstrates how much cybersecurity has evolved over the years and why preemptive actions have become so critical against large-scale phishing attacks.
Complexity is inherent in security enhancements, particularly for outdated systems such as SMTP and Microsoft Exchange.
Including remedies without adversely interfering with functionalities calls for deliberate actions and engagement of clients.
Proofpoint’s management of the EchoSpoofing challenge demonstrates maturity in risk management. By working with partners like Guardio to implement efficient, non-disruptive solutions, Proofpoint demonstrates its commitment to risk management.
Are you from SOC and DFIR Teams? – Analyse Malware Incidents & get live Access with ANY.RUN -> Free Access


