

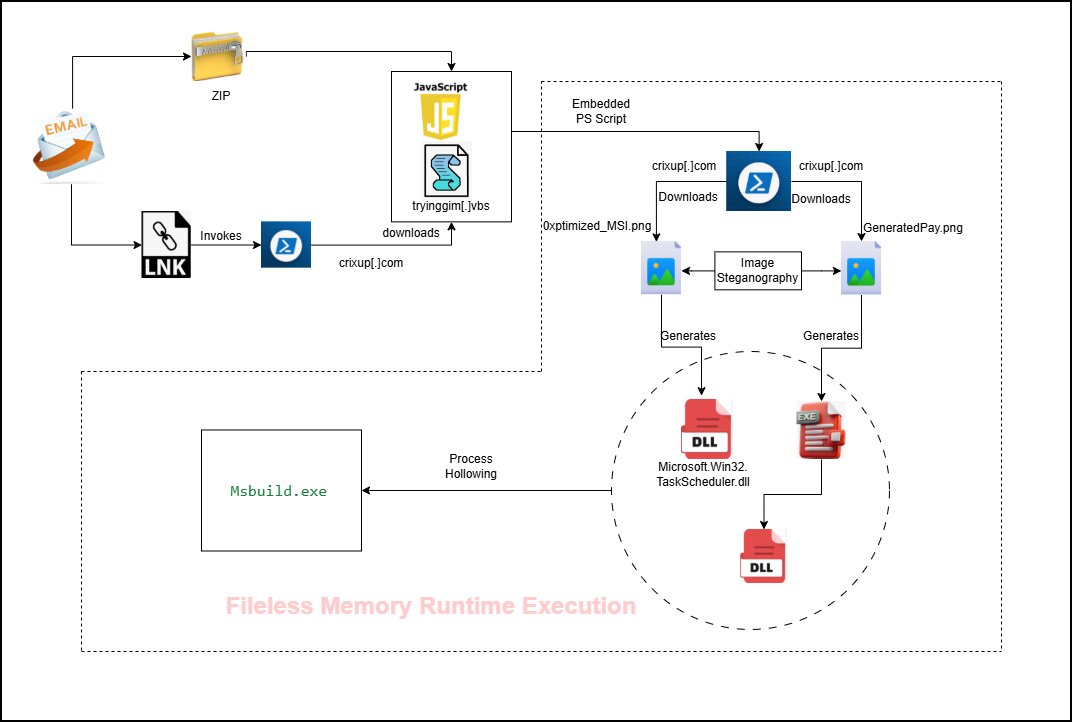
A multi-stage PureRAT campaign that hides portable executable (PE) payloads inside PNG images and executes them almost entirely in memory, making detection and forensics significantly harder for defenders.
The campaign combines steganography, PowerShell-based loaders, UAC bypass, process hollowing, and anti-virtualization checks to remain stealthy on compromised systems.
The attack begins with a weaponized .LNK file that, instead of opening a legitimate document or application, runs a hidden PowerShell command.
This script runs PowerShell in a hidden window with a bypassed execution policy, then downloads an obfuscated VBS file (tryinggim.vbs) from a remote server and launches it from the system’s temporary folder using Start-Process, inheriting the current user’s privileges.
In this operation, attackers use a layered infection chain that starts with a malicious Windows shortcut (.LNK) and ends in a fully featured PureRAT implant controlled remotely via a command-and-control (C2) server.
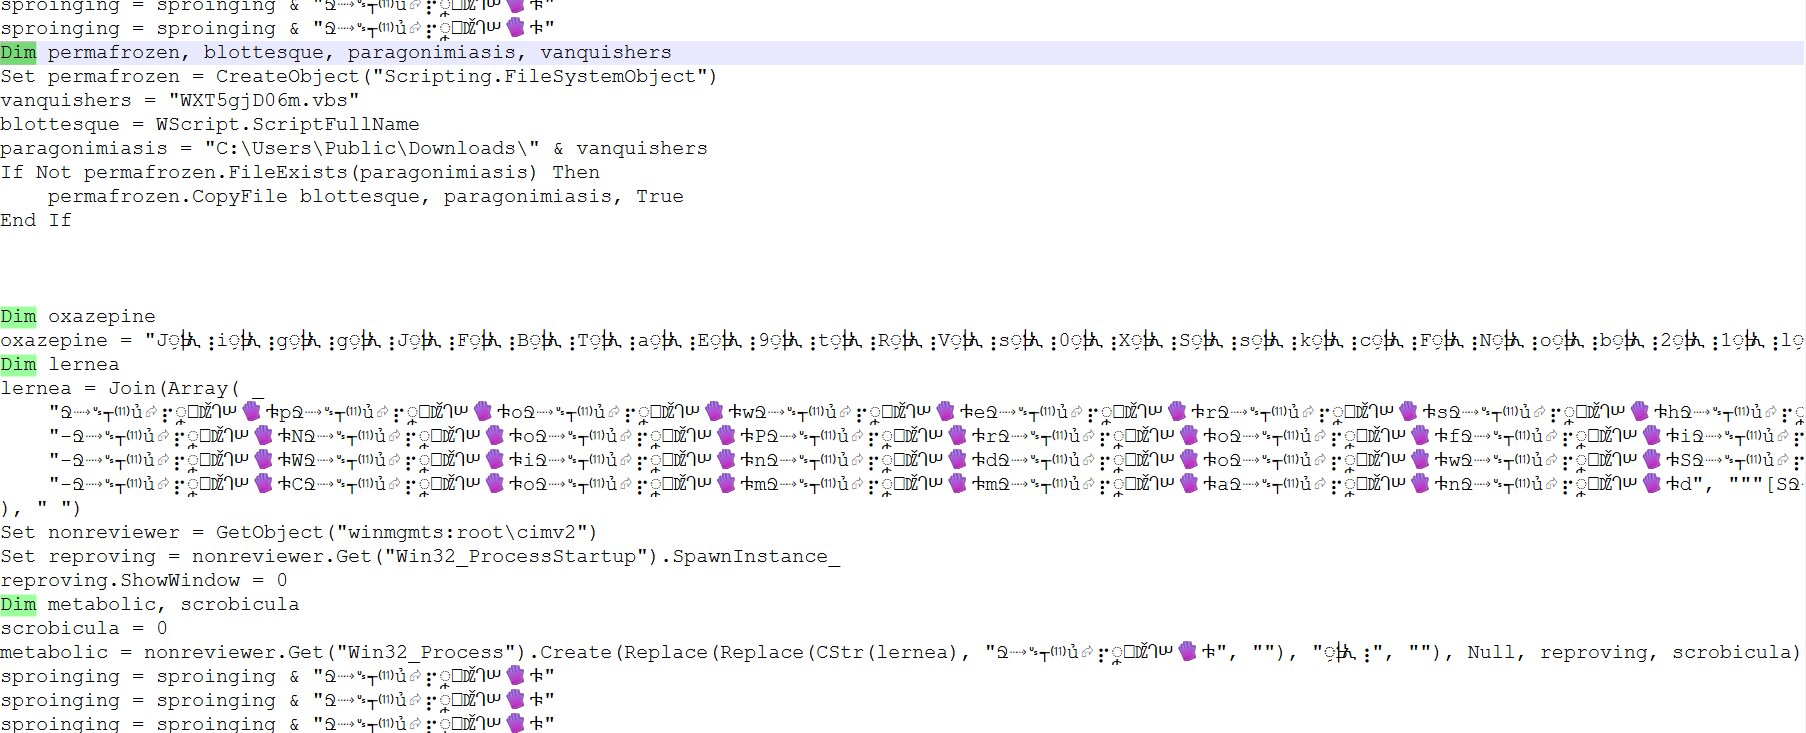
The second-stage VBS loader is heavily padded with junk data and obfuscation to frustrate static analysis and evade detection.
It copies itself into C:\Users\Public\Downloads under a random name, then uses WMI (Win32_ProcessStartup with ShowWindow=0) to spawn further payloads completely hidden from the user.
For persistence, the script creates a Task Scheduler job that runs every minute, ensuring the loader and subsequent stages are repeatedly executed without user interaction.
Fileless PE delivery via PNG steganography
The next stage is a PowerShell loader that delivers the core payloads without dropping conventional executables to disk.
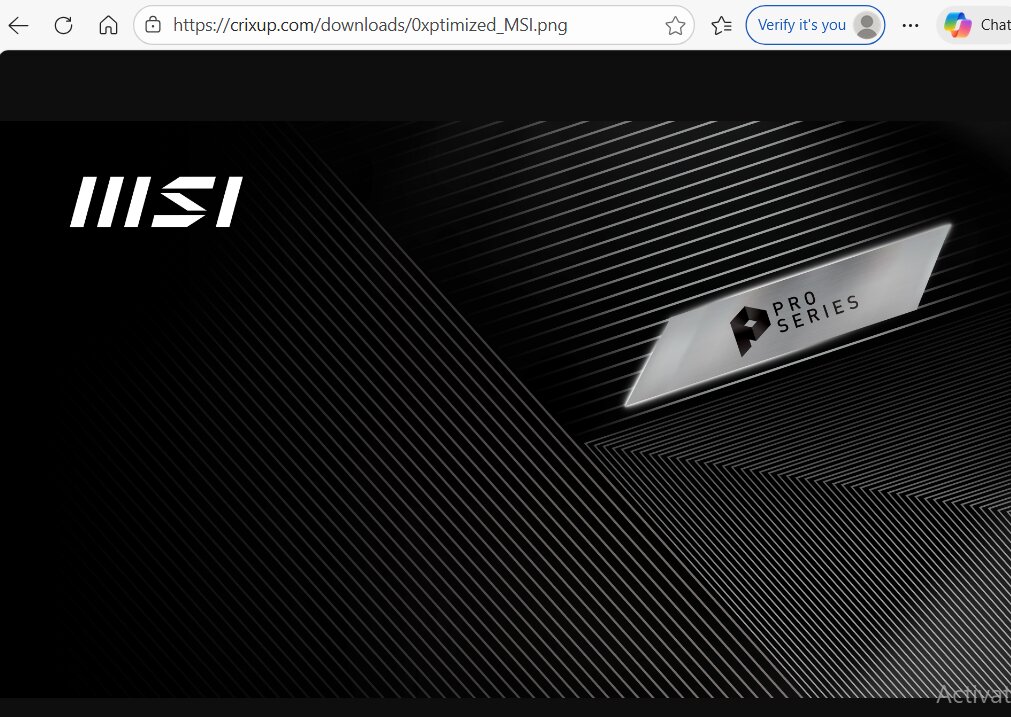
It connects to a hardcoded domain to retrieve a PNG file (“0xptimized_MSI.png”) that visually appears benign but contains a base64-encoded PE payload embedded between custom markers inside the image data.
The script locates start and end indices for the hidden blob, extracts the data, performs character substitutions, reverses the resulting array, and base64-decodes it into a byte array representing a .NET assembly.
A second PNG (“GeneratedPay.png”) is also downloaded, and the decoded assembly is loaded directly into memory via [System.Reflection.Assembly]::Load(), with its Main method invoked and the second image passed as an argument, keeping all malicious logic inside PowerShell’s process memory.
The VBScript second-stage payload is central to the infection chain, with the most malicious activity occurring within it.
This loader abuses a legitimate Task Scheduler .NET wrapper to create high-frequency tasks, and uses conhost.exe with the –headless flag to run additional hidden PowerShell commands that download and launch follow-on payloads.
For more durable persistence, the DLL sets a Run key under HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\Run, ensuring execution on user logon.
It also implements an advanced UAC bypass using cmstp.exe, generating a temporary INF file whose PreSetupCommands section executes a PowerShell-based registry modification under auto-elevated privileges, then automates confirmation of the cmstp window using Windows API calls and simulated keypresses.
Anti-VM checks and process
Before fully activating, the malware performs environment checks to avoid sandboxes and analyst VMs, including looking for VMware artifacts and MAC addresses associated with QEMU virtual machines.
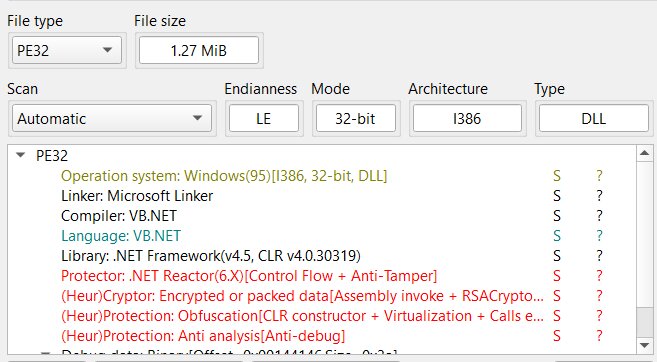
The decoded DLL (from 0xptimized_MSI.png) is a .NET module protected by .NET Reactor, which complicates reverse engineering but can be unpacked with standard tooling.
If the environment is deemed safe, the decrypted PE payload is inspected for architecture, then staged into the appropriate system directory (SysWOW64 for 32-bit, System32 for 64-bit) and executed using a RunPE/process hollowing routine.
In this routine, a legitimate Msbuild.exe process is created in a suspended state, its original memory unmapped, and the malicious payload injected into the newly allocated memory space before resuming the main thread.
Because only process memory is modified and the on-disk Msbuild.exe remains intact and signed, the malware benefits from strong defense evasion against signature- and reputation-based tools.
The final stage is a .NET-based PureRAT payload, again protected with .NET Reactor, that acts as a modular post-exploitation framework.
Its initial activity focuses on detailed host fingerprinting through WMI and system APIs, collecting information on installed security products, hardware identifiers, OS version and architecture, user accounts, and privilege levels.
Through downloadable plugins, operators can enable capabilities such as keylogging, remote desktop access, webcam and microphone monitoring, and additional credential theft on demand, turning PureRAT into a flexible dynamic loader rather than a static, one-size-fits-all implant.
This campaign highlights how attackers increasingly weaponize benign-looking PNG files and trusted Windows binaries to deliver multi-stage, fileless RAT infections.
Defenders should monitor for suspicious .LNK-initiated PowerShell activity, frequent Task Scheduler creation, anomalous cmstp.exe usage, and process hollowing into binaries like Msbuild.exe, alongside deep inspection of image traffic and memory-resident .NET assemblies to detect similar PureRAT operations.
Follow us on Google News, LinkedIn, and X to Get Instant Updates and Set GBH as a Preferred Source in Google.


 payloads inside PNG images and executes them almost entirely in memory.)