

Akira is an information stealer malware that was found in March 2023. This malware can steal sensitive information, including saved credentials and payment card details, usernames, system ID, hardware details, installed software, and network configurations.
Once this information is extracted, it uploads the data on a ‘GoFile’ online storage management service and Discord instant messaging service accounts owned by the threat actor.
Akira Stealer
According to the reports exclusively shared with Cyber Security News, Akira Stealer contains a multi-level infection process for code obfuscation and detection evasion.
The threat actor is also found to be providing services over Telegram, a C2 server, and GitHub.
Moreover, the threat actor claims that this malware is FUD (Fully Undetectable). Its telegram channel, Akira, consists of 358 subscribers as of now. The threat actor also offers a Malware-as-a-service domain “https[:]//akira[.]red/”.
File, Behavioral, and Code Analysis
As a means of Analysis, researchers collected a sample file, “3989X_NORD_VPN_PREMIUM_HITS.txt.cmd,” which was a CMD script file with obfuscated code. However, as stated by the threat actor, the file is completely undetectable on VirusTotal.
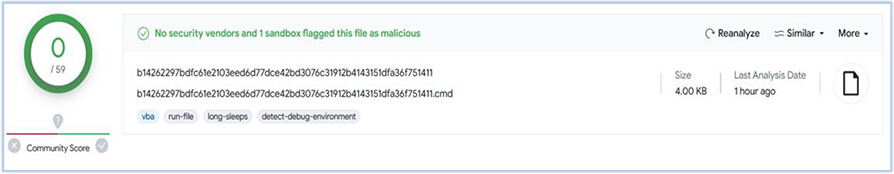
When executed, it drops a hidden.bat batch file on the current working directory, which was also found to be undetectable. This file consists of an obfuscated PowerShell script that embeds the batch file with the tmp.vbs file for executing with the csscript.exe process.
Extraction and Exfiltration
As for the information stealing, the malware creates a folder with the name of the compromised PC for storing the stolen information. Post this, the malware starts to steal information from several browsers, including Microsoft Edge, Google Chrome, Opera, Mozilla Firefox, and 14 other browsers.
Furthermore, the stealer is also capable of targeting financial data, such as saved credit cards and login credentials, collecting bookmarks and wallet extension data, taking screenshots, and much more.
A complete report about this Akira stealer malware has been published by Cyfirma, which provides detailed information about the malware behavior, source code, and other information.
Indicators of Compromise
| S.No | Indicators | Type | Context |
| 1 | 016dfdd45c8208d246d59327c40355e0 | MD5 Hash | 3989X_NORD_VPN_PREMIUM_HITS.txt.cmd |
| 2 | b14262297bdfc61e2103eed6d77dce42bd3076c31912b4143151dfa36f751411 | SHA-256 Hash | 3989X_NORD_VPN_PREMIUM_HITS.txt.cmd |
| 3 | 81e7ff1742d45075305a2082b1a7ac9d | MD5 Hash | hidden.bat |
| 4 | 03564dc699f82f7e5d52046d82863ceddc6d657c66c0078f88cfe9cf1953187b | SHA-256 Hash | hidden.bat |
| 5 | 4027c802411f8b4091c5c4eb077efa49 | MD5 Hash | File.zip |
| 6 | 50e36d96cb593c39afa2fc11ac25c976f0ff1586159d2eb2626902e6d6062f81 | SHA-256 Hash | File.zip |
| 7 | Akira[.]red | Domain | C2 server |
| 8 | https[:]//akira[.]red/pyst.txt | URL | C2 server |
| 9 | https[:]//akira[.]red/inj.php | URL | C2 server |
| 10 | https[:]//api[.]gofile[.]io/getServer | URL | Data exfiltration |
| 11 | https[:]//store11[.]gofile[.]io/uploadFile | URL | Data exfiltration |
| 12 | https[:]//store1[.]gofile[.]io/uploadFile | URL | Data exfiltration |
| 13 | https[:]//store4[.]gofile[.]io/uploadFile | URL | Data exfiltration |
| 14 | https[:]//discord[.]com/api/webhooks/1145738132550078484/px0c3QsngkzQX39aXJP-vKODDYwvODftHl6j83epN0ndbZ0O_DQ7D6vhFVDcluj0rLey | URL | Data exfiltration |
| 15 | https[:]//store7[.]gofile[.]io/download/direct/13d3e926-8be7-4c15-a1d9-f0e809ec1f14/m2[.]zip | URL | Malware download |
| 16 | https://t[.]me/AkiraRedBot | URL | Telegram channel |
| 17 | https://t[.]me/akiraundetector | URL | Telegram channel |
Protect yourself from vulnerabilities using Patch Manager Plus to patch over 850 third-party applications quickly. Try a free trial to ensure 100% security.


