

Qilin ransomware has emerged as a formidable force, rapidly ascending to prominence amid the collapse of once-dominant groups like RansomHub and LockBit in 2025.
Active since October 2022, Qilin has solidified its position through a sophisticated Ransomware-as-a-Service (RaaS) model, offering affiliates advanced tools and infrastructure while claiming 15-20% of ransom payments.
Its ability to target Windows, Linux, and ESXi systems with custom-built malware written in Rust and C showcases a technical prowess that sets it apart.
A New Leader in the Ransomware Landscape
With over 100 organizations listed on its dark web leak site and ransom demands ranging from $50,000 to $800,000, Qilin is not just filling the void left by fallen ransomware giants but redefining the landscape with a full-service cybercrime platform.

Qilin’s technical capabilities are a testament to its threat level, as it deploys payloads with advanced encryption algorithms like ChaCha20, AES, and RSA-4096, ensuring unbreakable data locking across platforms.
Its affiliate panel is a powerhouse, featuring configurable encryption modes (normal, step-skip, fast, and percent), safe-mode execution, log cleanup, and network propagation capabilities.
The Windows variant, written in Rust, leverages tools like PsExec for worm-like spreading, deletes shadow copies, clears event logs, and even prints ransom notes via connected printers to maximize impact.
Cross-Platform Destruction
On Linux and ESXi systems, the C-based variant targets virtualization environments, enumerating VMware vCenter and ESXi hosts, modifying root passwords, enabling SSH, and deploying malicious payloads to disrupt critical infrastructure.
According to Cybereason Report, it also optimizes I/O performance on ESXi hosts and targets databases and containers like MySQL, Docker, and MongoDB, ensuring maximum disruption.
Beyond malware, Qilin offers unique services like PB-scale data storage, spam tools, legal assistance through a “Call Lawyer” feature, and media support for negotiation pressure, positioning it as a comprehensive cybercrime ecosystem.
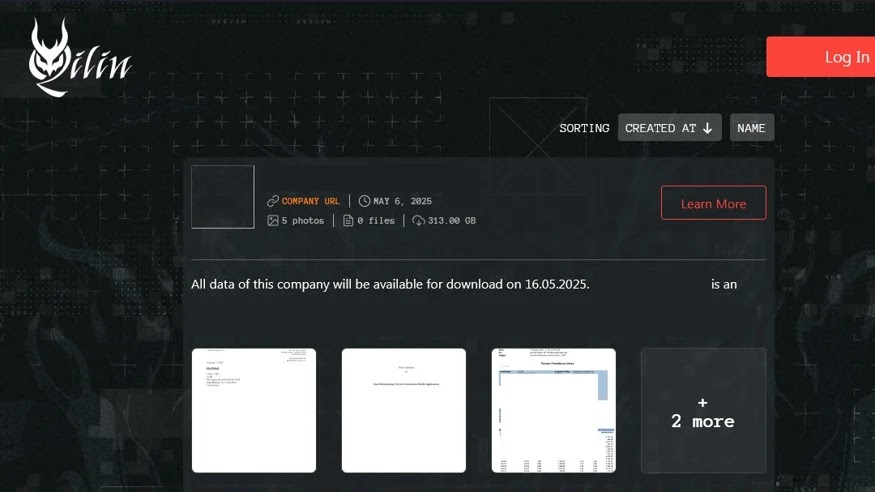
Notably, in February 2024, Qilin launched a “WikiLeaks V2” site to publish stolen data, highlighting its aggressive extortion tactics.
The ransomware’s operational stealth is further enhanced by requiring a password to initiate attacks, evading sandbox analysis, while its cross-platform strategy ensures it can cripple both traditional and virtualized environments.
As older ransomware operations face shutdowns and internal betrayals, Qilin’s rise, marked by over 50 attacks in recent months, signals a new era of cyber threats that demand robust defenses.
Organizations must prioritize multi-layered security, regular backups, and network monitoring to counter this evolving menace.
Indicators of Compromise (IOCs)
| Type | Value |
|---|---|
| IP Address | 185.208.156.157 (FTP data share) 185.196.10.19 (FTP data share) 80.64.16.87 (WikiLeaks V2) |
| SHA-256 (Windows) | 31c3574456573c89d444478772597db40f075e25c67b8de39926d2faa63ca1d8 C9707a3bc0f177e1d1a5587c61699975b1153406962d187c9a732f97d8f867c5 |
| SHA-256 (Linux) | 13cda19a9bf493f168d0eb6e8b2300828017b0ef437f75548a6c50bfb4a42a09 a7f2a21c0cd5681eab30265432367cf4b649d2b340963a977e70a16738e955ac |
Find this News Interesting! Follow us on Google News, LinkedIn, and X to Get Instant Updates







