
A newly analyzed ransomware strain, “The Gentlemen,” is raising concern among security researchers due to its ability to combine strong encryption with aggressive lateral movement.
What makes this threat particularly dangerous is its use of SYSTEM-level scheduled tasks to encrypt local drives, allowing attackers to operate with the highest Windows systems privileges.
This technique ensures deeper system access, improves encryption reliability, and bypasses many standard user-level restrictions.
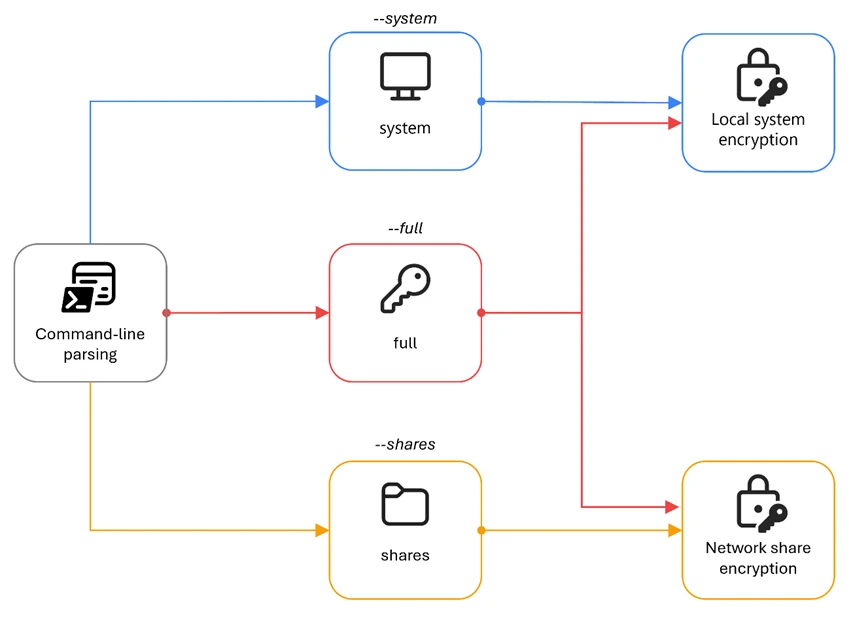
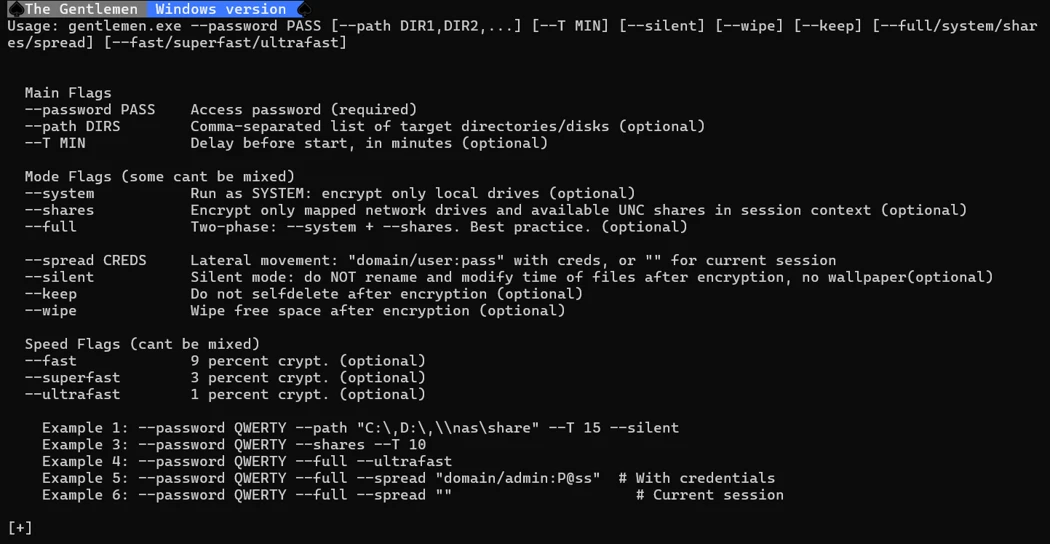
The Gentlemen ransomware uses command-line arguments to control its execution. A key feature is the “–full” mode, which launches two parallel processes: one targeting local drives using the “–system” flag and another targeting network shares with the “–shares” flag.
When the system mode is triggered, the malware creates a scheduled task that re-executes itself under the SYSTEM account.
Before encryption begins, the ransomware disables Microsoft Defender, deletes shadow copies, clears event logs, and removes forensic artifacts such as PowerShell history. These steps significantly reduce detection and recovery options.
This approach gives the ransomware unrestricted access to files that may otherwise be locked or protected. The malware first deletes any existing scheduled task named “gentlemen_system,” then creates a new one configured to run with elevated privileges, and finally executes it immediately. This chain ensures clean execution and avoids conflicts.
Tracked by Microsoft as Storm-2697, this ransomware-as-a-service (RaaS) operation has evolved rapidly since mid-2025 and is now being used in widespread attacks across multiple industries worldwide.
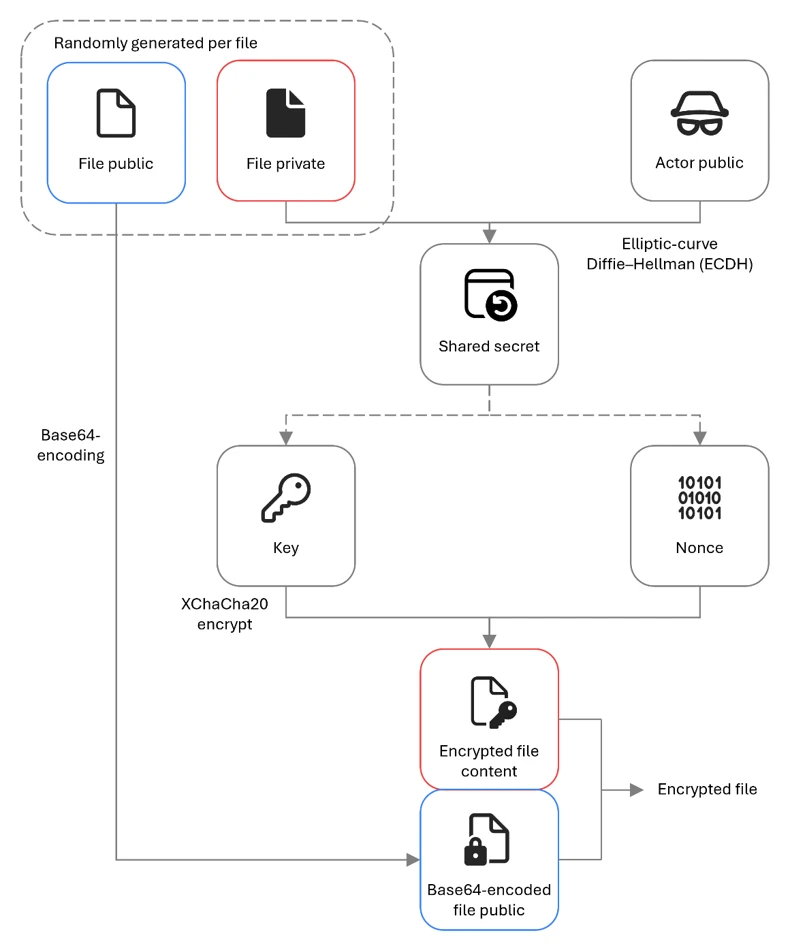
From a cryptographic perspective, The Gentlemen uses a hybrid model combining Curve25519 elliptic-curve cryptography with the XChaCha20 stream cipher.
Each file is encrypted using a unique ephemeral key, ensuring strong isolation between files. Smaller files are fully encrypted, while larger files are partially encrypted in multiple chunks to increase speed while still rendering them unusable.
Ransomware Abuses SYSTEM Task
Beyond encryption, The Gentlemen ransomware attack stands out for its highly aggressive self-propagation capabilities. When the “–spread” option is used, the malware attempts to move laterally across the network using multiple techniques simultaneously, including PsExec, WMI, scheduled tasks, services, and PowerShell remoting.
The speed arguments (--fast, --superfast, --ultrafast) are mutually exclusive and control how much of each large file is encrypted.
The malware prepares infected systems as distribution points by creating hidden SMB shares and enabling anonymous access. It then scans for other machines and attempts up to 21 different execution methods per target.
This redundancy ensures that even if some techniques fail, others may succeed, significantly increasing the chance of widespread compromise.
Generates a unique ephemeral Curve25519 key pair, consisting of a randomly generated private key and its corresponding public key.
Additionally, the ransomware employs double extortion tactics. It not only encrypts files but also exfiltrates sensitive data, threatening to leak it publicly if the ransom is not paid.
This increases pressure on victims, especially in sectors like healthcare, finance, and education, where data sensitivity is high.
Persistence is maintained through both scheduled tasks and registry run keys, allowing the malware to survive reboots and continue operations. In some cases, it also wipes free disk space to prevent recovery of deleted data, further complicating incident response.
The combination of SYSTEM-level execution, strong encryption, and multi-method propagation makes The Gentlemen a highly effective and dangerous ransomware threat.
Its growing adoption through underground forums suggests that organizations should expect increased activity and should prioritize detection of scheduled task abuse, privilege escalation, and unusual lateral movement patterns.
Indicators of compromise
| Indicator | Type | Description |
| 22b38dad7da097ea03aa28d0614164cd25fafeb1383dbc15047e34c8050f6f67 | SHA-256 | Gentlemen ransomware encryptor |
| 078163d5c16f64caa5a14784323fd51451b8c831c73396b967b4e35e6879937b | SHA-256 | PsExec binary |
| fe1033335a045c696c900d435119d210361966e2fb5cd1ba3382608cfa2c8e68 | SHA-256 | Gentlemen wallpaper Bitmap file |
Note: IP addresses and domains are intentionally defanged (e.g., [.]) to prevent accidental resolution or hyperlinking. Re-fang only within controlled threat intelligence platforms such as MISP, VirusTotal, or your SIEM.
Follow us on Google News, LinkedIn, and X to Get Instant Updates and Set GBH as a Preferred Source in Google.


