

Microsoft Threat Intelligence Center (MSTIC) found a new ransomware named “Prestige” ransomware targeting organizations in the transportation and associated logistics industries in Ukraine and Poland.
Researchers say this novel ransomware campaign was first deployed on October 11 in attacks occurring within an hour of each other across all victims.
Important Features of Prestige Ransomware
In this case, attackers’ were seen deploying the ransomware payloads across their victims’ enterprise networks which is not common in Ukraine.
“The activity shares victimology with recent Russian state-aligned activity, specifically on affected geographies and countries, and overlaps with previous victims of the FoxBlade malware (also known as HermeticWiper)”, says Microsoft
MSTIC has not connected this campaign to any known threat group and the investigations are still going on. This activity included the use of the following two remote execution utilities:
- RemoteExec – a commercially available tool for agentless remote code execution
- Impacket WMIexec – an open-source script-based solution for remote code execution
Tools used for privilege escalation and credential extraction:
- winPEAS – an open-source collection of scripts to perform privilege escalation on Windows
- comsvcs.dll – used to dump the memory of the LSASS process and steal credentials
- ntdsutil.exe – used to back up the Active Directory database, likely for later use credentials
Based on the observation, researchers say the attacker had already gained access to highly privileged credentials, like Domain Admin, to assist the ransomware deployment.
Methods Used For Ransomware Deployment
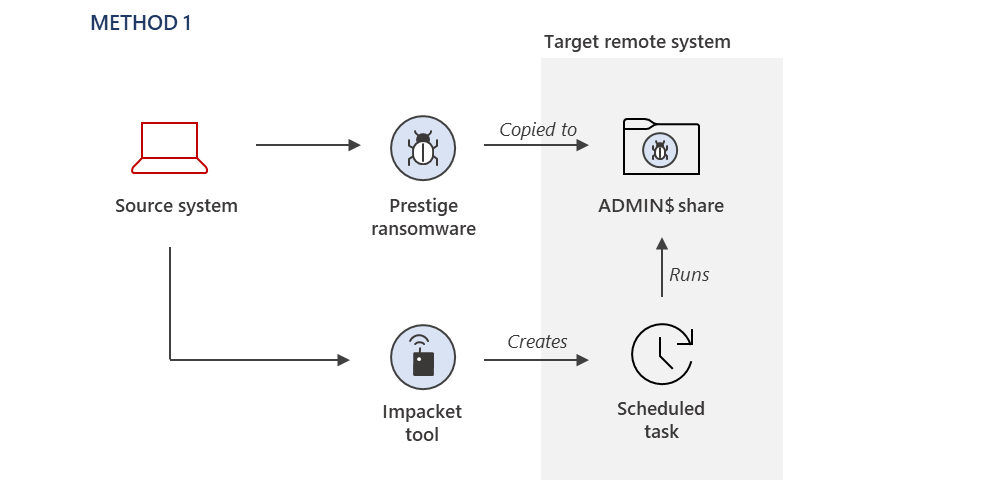
Method 1:
In the first method, the ransomware payload is copied to the ADMIN$ share of a remote system and Impacket is used to remotely create a Windows Scheduled Task on target systems to execute the payload.
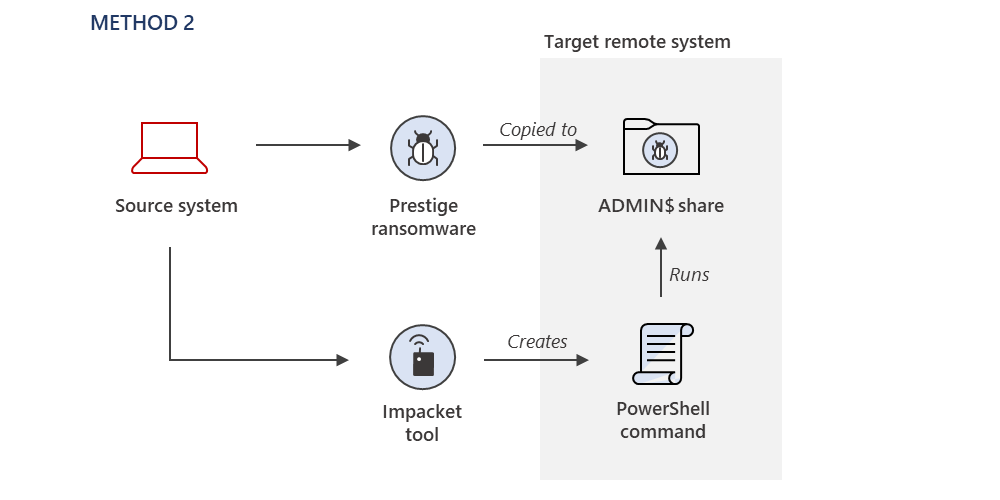
Method 2:
Subsequently, in this method the ransomware payload is copied to the ADMIN$ share of a remote system, and Impacket is used to remotely invoke an encoded PowerShell command on target systems to execute the payload
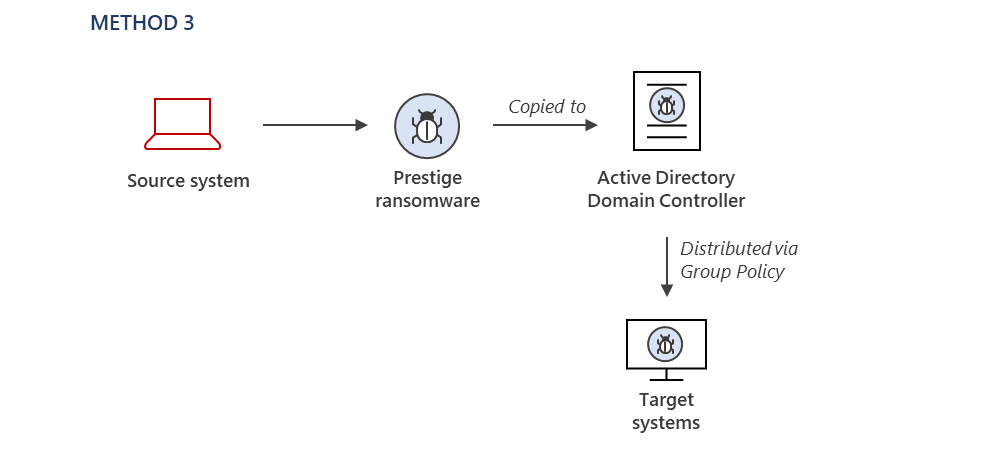
Method 3:
The ransomware payload is copied to an Active Directory Domain Controller and deployed to systems using the Default Domain Group Policy Object.
Researchers say “Prestige” ransomware works by encrypting a victims’ data and leaving a ransom note that says the data can only be unlocked with the purchase of a decryption tool.
Customers Should Act On These Alerts
- Ongoing hands-on-keyboard attack via Impacket toolkit
- WinPEAS tool detected
- Sensitive credential memory read
- Password hashes dumped from LSASS memory
- Suspicious scheduled task activity
- System recovery setting tampering
- File backups were deleted
Also Read: Download Secure Web Filtering – Free E-book





.png?fit=728,380&ssl=1&description=Microsoft Threat Intelligence Center (MSTIC) found a new ransomware named “Prestige” ransomware targeting organizations in the transportation and associated logistics industries in Ukraine and Poland.)