

Coronavirus has a direct impact on cybersecurity, threat actors taking advantage of the current situation to launch various attacks such as malware, phishing, fraud, and disinformation campaigns.
In the current situation, most of the people started working remotely, so the RDP and the video communication platforms usage will be high.
RDP Brute-force Attacks
Remote Desktop Protocol (RDP) is one of the most popular protocol developed by Microsoft that let users connect with workstations or servers remotely.
Since the lockdown the remote traffic is increased, attackers taking advantage of the situation to steal the corporate resources.
Kaspersky researchers observed, starting this March, the number of RDP attacks has been rocketed across almost the entire planet.
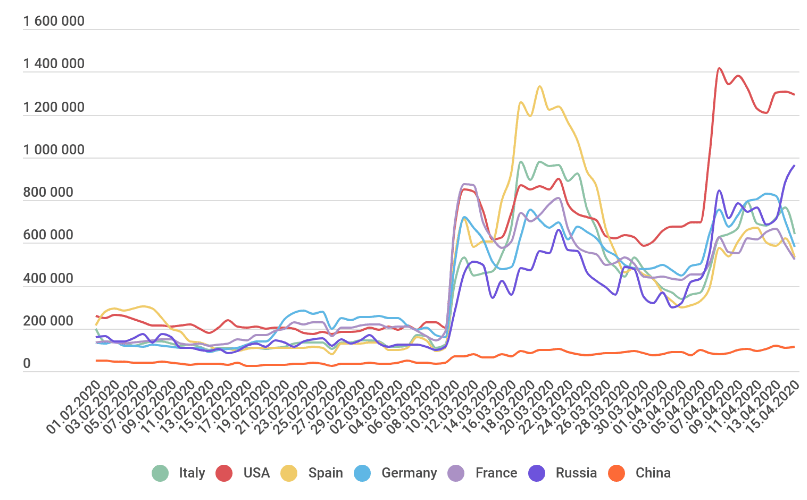
According to the report the RDP based attacks reached million per day by the end of the March as remote working proposed due to Coronavirus impact.
“Brute-force attackers are not surgical in their approach but operate by area. As far as we can tell, following the mass transition to home working, they logically concluded that the number of poorly configured RDP servers would increase, hence the rise in the number of attacks,” reads Kaspersky blog post.
In the case of RDP brute-force attacks, hackers use to scan the network using various tools to identify the IP address and the port ranges used by RDP servers.
Once RDP servers are tracked attackers use the various username and password combinations to gain access to the RDP servers.
If the attacker gains access to the RDP server they can sell the RDP credentials in dark web forums, disable antivirus software, install malware, steal company data, encrypt files, and much more.
Recently as well-know trojan TrickBot has included a new module for RDP that specifically built for brute-forcing RDP connections.
Mitigations
- Recommended to set strong RDP passwords
- Setup Network Level Authentication
- Two-factor Authentication
- If RDP not in use disable it
- Implement Account lockout policy
You can follow us on Linkedin, Twitter, Facebook for daily Cybersecurity and hacking news updates.







