

The ransomware evolution re-shaping the cyber domain, starting from 2019 the ransomware attacks against high-profile public and corporate networks by making criminal alliances.
In 2018, threat actors behind GandCrab ransomware launched their Ransomware-as-a-Service which shifts the paradigm and turns the ransomware a full-fledged business with Branding, marketing, outreach.
Threat Actor Group Truniger
Truniger also known as TeamSnatch created by an individual who interested in credit card fraud expanded hacking into through corporate networks and the threat actor uses RDP based vulnerabilities, specifically, brute-forcing to gain access to different RDP databases.
The RDP brute-forcing vector proved to be more successful and soon, the truniger started to investigate different ways to monetize the accesses which they obtained, reads Advintel report.
Truniger managed to encrypt more than 1,800 devices using GandCrab by the end of August 2018. The threat actor said that by participating in GandCrab’s affiliate program he learned the methods to launch sophisticated attacks.
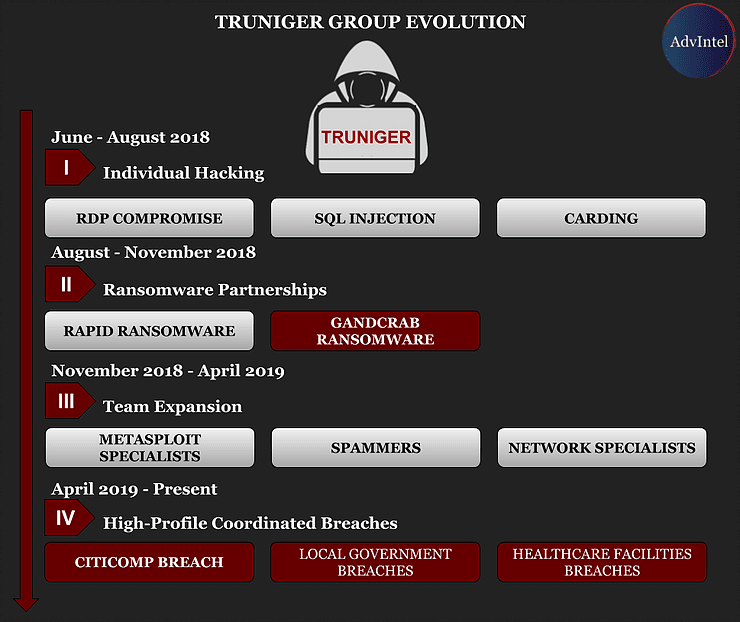
So the actor decided to build the own ransomware and expand the group by hiring technical support for ransomware operations, for specialists they are to provide monthly salaries up to USD 10,000.
Tools and Techniques Used
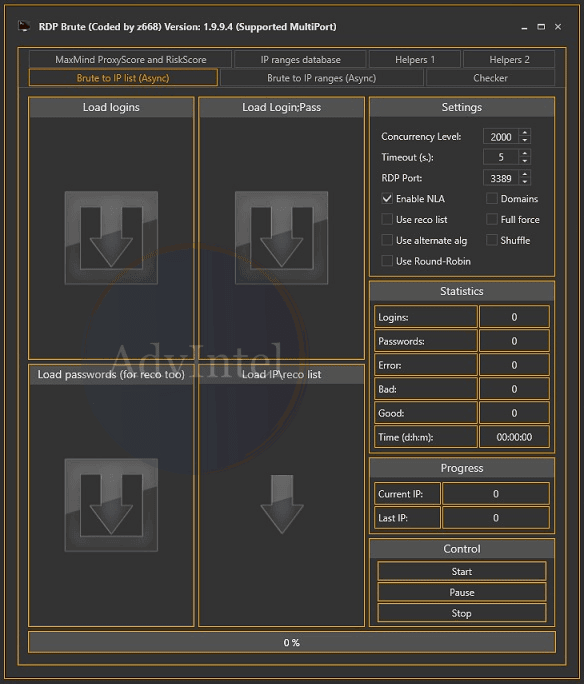
The truniger hacker group uses several techniques to distribute the ransomware and the primary attack vector among them is RDP brute-forcing, the threat actor group uses weaponized pentesting tool for initial engagement.
AdvIntel said that “On June 20, 2019, the truniger team shared that they are changing the main attack vector for network breach from RDP compromise to a botnet.”
The group tries to gain Windows system administrators privileges and the group uses mimikatz tool to search for domain admin credentials, financial details and to escalate privileges.
Truniger group said AdvIntel that the loader delivered through targeted email phishing and then recruit them for the botnet, the attackers primary focused on dedicated servers with RDP and interested in Dynamic Data Exchange (DDE).
The notable incident of the Truniger group is the attack on German IT company CityComp and obtained data from companies such as Oracle, SAP, BT, Porsche, Toshiba, Volkswagen, Airbus, and others.
The group also advertised access for various RDP network associated with government networks and the retails shops, the RDP’s are advertised for USD 500 to USD 3,000 depends upon the network.
You can follow us on Linkedin, Twitter, Facebook for daily Cybersecurity and hacking news updates







