Sunday, October 18, 2026

RedEye – CISA Developed Open-source Red Team Tool Monitoring C&C Server Activities

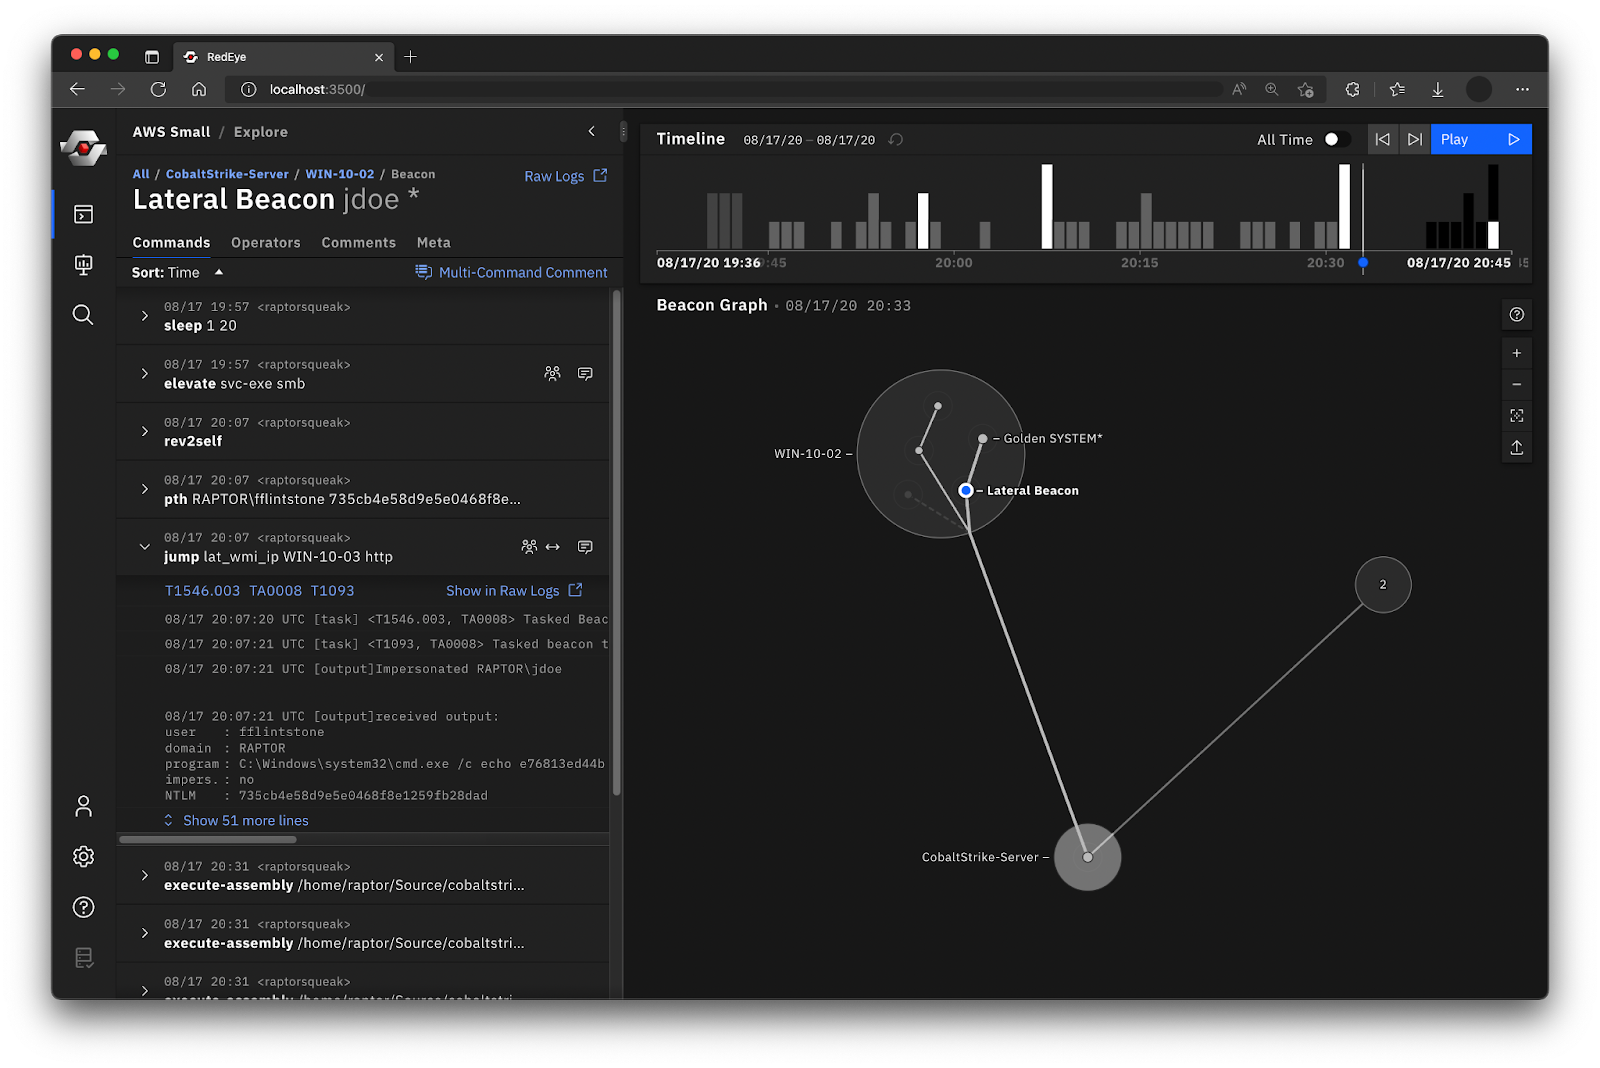
A new open-source analytical tool dubbed RedEye designed to make it easier for operators to visualize and report activities associated with C2 communication has been released by CISA.

Both the red and blue teams can benefit from RedEye, as it provides an easy way to gauge data, leading to specific decisions that can be made with confidence.

RedEye

A collaborative effort between CISA and DOE’s Pacific Northwest National Laboratory has given birth to this analytical tool. 

A graphically displayed log of all servers and hosts associated with each campaign can be retrieved by RedEye users by correlating historical records of each campaign log.

In order to view relevant information about a campaign, users can upload campaign data via RedEye to view information such as:-

  • Beacons 
  • Commands

During the process of parsing log files, such as those generated by Cobalt Strike, the tool presents the information in a format that can be easily understood.

As a result, users are able to tag activities displayed within the tool and comment on them. Operators can present findings and workflow to stakeholders using the presentation mode that is available on the RedEye application.

To discover the payload activity analysts can also analyze all the key events in a selected campaign. In addition to using RedEye to check the raw data received after an assessment, blue teams can also use it to understand it better.

This data can be used by them to see the attack path and the compromised hosts to take the appropriate action based on what they have learned.

RedEye offers a wide range of features and all its key features are presented in the below video made by CISA:-

Apart from RedEye, the CISA have also released several other open-source tools like:-

  • Malcom
  • ICS NPP
  • Sparrow

The following major platforms have been tested and proved to be compatible with RedEye:- 

  • Linux (Ubuntu 18 and above, Kali Linux 2020.1 or newer)
  • macOS (El Capitan and above)
  • Windows 7 or newer

Moreover, the CISA’s repository on GitHub hosts the tool, and it is available for download via the repository.

Also Read: Download Secure Web Filtering – Free E-book

Balaji
Balaji
BALAJI is an Ex-Security Researcher (Threat Research Labs) at Comodo Cybersecurity. Editor-in-Chief & Co-Founder - Cyber Security News & GBHackers On Security.

Hot this week

How To Access Dark Web Anonymously and know its Secretive and Mysterious Activities

What is Deep Web The deep web, invisible web, or...

How to Build and Run a Security Operations Center (SOC Guide) – 2023

Today’s Cyber security operations center (CSOC) should have everything...

Russian Hackers Bypass EDR to Deliver a Weaponized TeamViewer Component

TeamViewer's popularity and remote access capabilities make it an...

Web Server Penetration Testing Checklist – 2026

Web server pentesting is performed under three significant categories: identity,...

ATM Penetration Testing – Advanced Testing Methods to Find The Vulnerabilities

ATM Penetration testing, Hackers have found different approaches to...

Hackers Use ConnectWise SkyKick Credentials to Access Microsoft 365, Halting Cloud Backups

Attackers abused compromised ConnectWise Cloud Backup credentials to access...

Anthropic’s Claude AI Uncovers Origins of NSA-Provided Cryptographic Keys After 25 Years

Anthropic says an internal Claude research model reconstructed how...

OpenBSD Kernel Flaw Dating Back 37 Years Enables Local Privilege Escalation to Root

A newly disclosed OpenBSD kernel exploitation chain combines a...

GhostAction Hackers Hide Credential-Stealing Malware in Fake Font Files Across 94 GitHub Repositories

GhostAction attackers have expanded their GitHub credential theft campaign...

SideCopy Hackers Target Indian Organizations With ReverseRAT Malware to Steal Data

Indian authorities have warned that SideCopy hackers are targeting...

New GhostBat Android Malware Targets 60 Banking and UPI Apps to Steal PINs

A new GhostBat RAT variant targets 60 Android financial...

New ROMULUS Malware Platform Uses Six Servers to Deliver Multiple Malicious Payloads

ROMULUS, a shared ClickFix delivery platform operating across six...

Related Articles

Recent News