

To fix the website access issues that have been building up after sanctions that are imposed by the western companies have prevented the renewal of certificates. That’s why to mitigate this situation Russia has created its own trusted TLS certificate authority (CA).
The Russian websites are unable to renew the existing TLS certificates because of the sanctions that are imposed by the western governments and companies. This causes the web browsers to block all access to websites having the expired certificates.
The web browsers that are showing full-page warnings due to this issue are:-
- Google Chrome
- Apple Safari
- Microsoft Edge
- Mozilla Firefox
The TLS certificates that are used by the web browsers, secure the communication between the clients and the target website by securely linking a cryptographic key to the organization’s details.
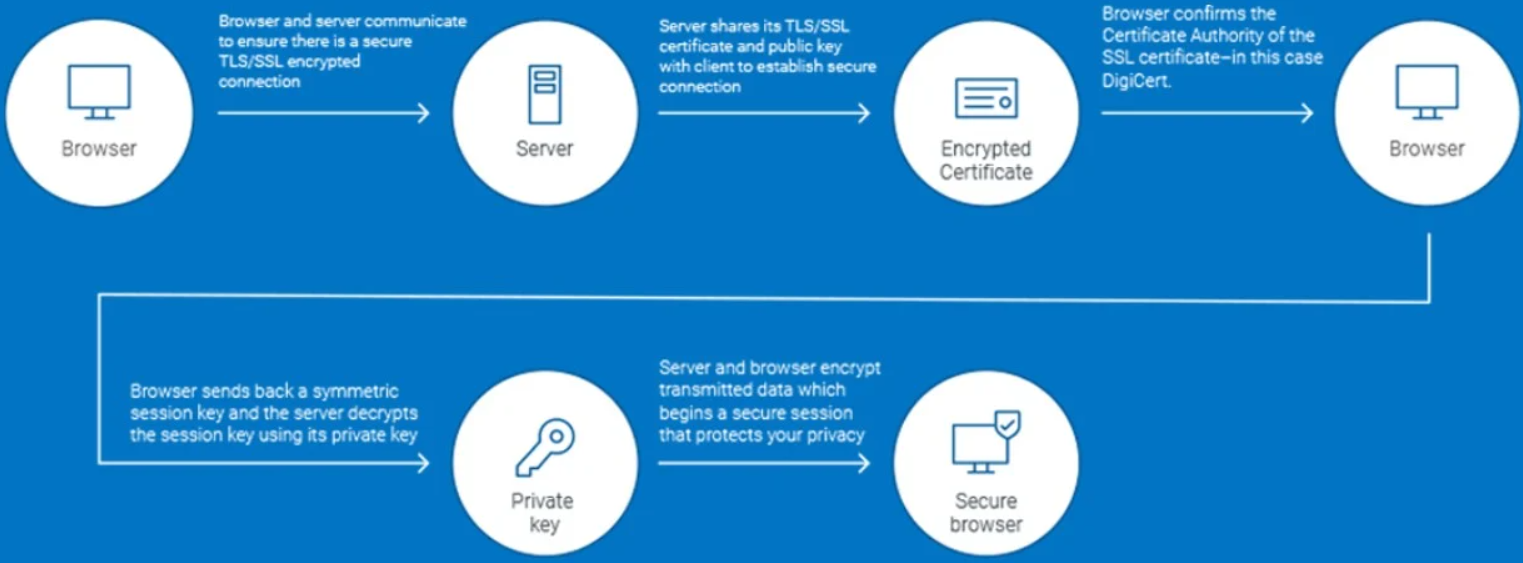
Russia’s own TLS Certificate authority
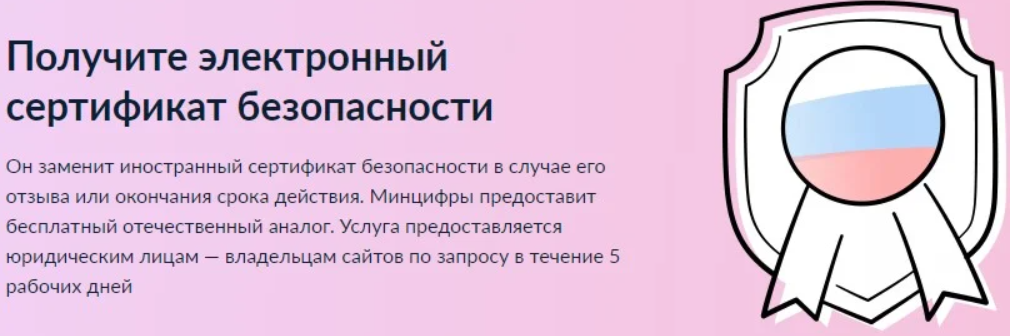
As a result, the Ministry of Digital Development is expected to provide a domestic alternative that would handle the revocation and renewal of TLS certificates.
A certificate is delivered to site owners within five working days if they request the service, with certificates available for all legal entities operating in Russia.
The new Certificate Authorities (CA) are first need to be vetted by a variety of companies, which can take quite some time before they are trusted by major web browsers.
While at this moment, only Yandex and Atom products recognize Russia’s new CA as trustworthy. Here the question arises, whether the web browsers such as Google Chrome, Microsoft Edge, Mozilla Firefox, and Apple Safari will permit safe connections to the certified servers by accepting certificates issued by the new Russian certificate authority.
Sites using Russia’s Certificates
A number of sites have already received and are now using these state-issued certificates. And here we have mentioned below the sites already using the Russia’s own certificates:-
- Sberbank
- VTB
- Russian Central Bank

Moreover, a list of 198 domains was also circulated in Russian media stating that they were notified to use the domestic TLS certificate, but the requirement hasn’t been made mandatory yet.
But, here the concern is that Russia may take advantage of their root certificate to intercept HTTPS traffic and execute several cyberattacks, reported.
The major browser vendors are unlikely to add Russia’s root certificates to their root certificate stores due to the lack of trust experienced by its certificate authorities.
You can follow us on Linkedin, Twitter, Facebook for daily Cybersecurity and hacking news updates.


