

A series of high-impact campaigns linked by overlapping tradecraft to ShinyHunters, in which attackers abused trusted Salesforce OAuth relationships to bypass conventional MFA protections, establish persistence, and exfiltrate CRM data at scale.
The activity, observed from mid-202520252025 through mid-202620262026, affected organizations in retail, education, and manufacturing.
Microsoft emphasized that the campaigns did not exploit an inherent Salesforce vulnerability. Instead, the operators manipulated legitimate OAuth workflows, compromised trusted SaaS integrations, and abused overly permissive guest access configurations.
The most prominent intrusion route involved voice phishing, or vishing. Attackers impersonated IT support staff and persuaded employees to authorize attacker-controlled connected applications in Salesforce.
In confirmed cases, the malicious application was presented as a legitimate Salesforce Data Loader utility.
Once a user approved the OAuth consent request, the application inherited that user’s permissions and could issue Salesforce API calls without requiring the attacker to authenticate repeatedly.
This effectively neutralized MFA as a meaningful barrier, as the malicious activity occurred through a valid, authorized OAuth session rather than via a stolen password or an anomalous login.
Microsoft said the access enabled attackers to enumerate Salesforce environments, query CRM data, maintain persistent access, and potentially discover credentials that could facilitate movement into other SaaS services.

In a series of campaigns observed between mid-2025 and mid-2026, Microsoft identified threat actor activity with overlapping tradecraft commonly associated with ShinyHunters, including voice phishing (vishing).
Because the calls originated from approved applications and operated with legitimate user privileges, they could evade detections focused on suspicious sign-ins.
Salesforce OAuth Abused
The threat actors also targeted Salesforce-connected vendors and integrations. In August 202520252025, compromised credentials associated with Salesloft Drift reportedly exposed connection secrets used by downstream SaaS applications, enabling attackers to use OAuth tokens across multiple customer Salesforce tenants.
A later campaign in November 202520252025 affected Gainsight-published applications integrated with Salesforce. According to Gainsight’s advisory, attackers abused trusted external connections to preserve API access across customer environments.
Microsoft further linked similar methods to the June 202620262026 Klue incident, where Storm-3138 accessed credentials used to reach Salesforce customer instances. Klue said the actor used those credentials to discover, query, and extract customer data.
In each case, the use of legitimate integration tokens made bulk discovery and export activity resemble normal application behavior.
Attackers could access accounts, contacts, and service-case records without generating the login anomalies commonly associated with account compromise.
Microsoft additionally observed suspicious activity against Salesforce Aura endpoints. Attackers exploited misconfigured Experience Cloud guest-user permissions and sent GraphQL access based Aura requests to enumerate and retrieve exposed data.
The activity did not rely on a software flaw. Instead, it exploited guest access granted beyond what was necessary. By chaining Aura requests, attackers could bypass normal record retrieval constraints and extract substantially more information than guest users should ordinarily access.
Salesforce administrators should review Experience Cloud guest-user security guidance and remove unnecessary object, field, and record permissions.
Microsoft expanded its Defender for Cloud Apps Salesforce connector to support near-real-time Salesforce telemetry through Salesforce Shield Event Monitoring.
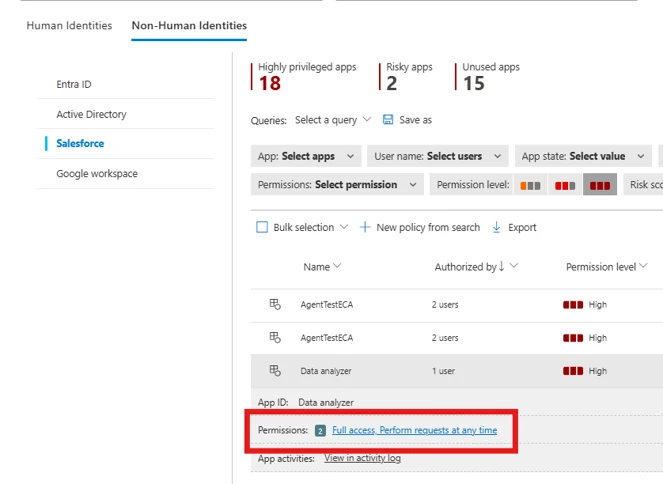
The enhanced integration provides connected-app attribution, OAuth scope visibility, API context, and risk-based insights for privileged or inactive applications.
Organizations should inventory every connected and external client application, validate OAuth scopes, revoke unused integrations, and investigate applications holding broad administrative or data-access permissions.
They should also monitor Salesforce event logs for bulk API queries, unusual export patterns, newly authorized connected apps, and unexpected activity from non-human identities.
The campaigns demonstrate that MFA alone cannot stop attacks that exploit trusted authorization. In SaaS environments, OAuth consent, third-party integrations, and guest permissions must be treated as critical identity security controls rather than operational conveniences.
Indicators of compromise (IOC)
| Indicator | Type | Description |
| 138.226.246.94 | IP address | Used by the Klue integration to call Salesforce API to perform CRM queries on June 11. Previously disclosed by Klue in their notification about the breach. |
| 212.86.125.24 | IP address | |
| 213.111.148.90 | IP address | |
| 94.154.32.160 | IP address | |
| 103.75.11.78 | IP address | Used to target the Aura framework with guest access from June 19 to 22. These IP addresses were not previously published and were discovered by Microsoft as part of a novel campaign. |
| 103.75.11.110 | IP address |
Note: IP addresses and domains are intentionally defanged (e.g., [.]) to prevent accidental resolution or hyperlinking. Re-fang only within controlled threat intelligence platforms such as MISP, VirusTotal, or your SIEM.
Stop Accepting SLAs Written for 2019 SOCs – Here’s the 2026 AI SLA Vendor Checklist – Download Free AI SOC SLA Guide


