

Sedgwick has confirmed a cybersecurity incident at its government-focused subsidiary after the TridentLocker ransomware gang claimed responsibility for stealing 3.4 gigabytes of data.
The breach highlights ongoing risks to federal contractors handling sensitive U.S. agency data.
Federal Contractor Confirms Unauthorized Access
Claims administration giant Sedgwick acknowledged on January 4, 2026, that Sedgwick Government Solutions (SGS) experienced unauthorized access to an isolated file transfer system.
The subsidiary provides risk management and claims services to key federal clients, including the Department of Homeland Security (DHS), Immigration and Customs Enforcement (ICE), Customs and Border Protection (CBP), U.S. Citizenship and Immigration Services (USCIS), Department of Labor (DOL), and Cybersecurity and Infrastructure Security Agency (CISA).
SGS also supports municipal agencies across all 50 states, the Smithsonian Institution, and the Port Authority of New York and New Jersey.
TridentLocker publicly listed SGS as a victim on New Year’s Eve, December 31, 2025, claiming to have exfiltrated 3.39 GB of documents and posting samples on its dark web leak site.
The ransomware-as-a-service (RaaS) group, which emerged in late November 2025, employs double-extortion tactics, encrypting systems and threatening to leak data.
A Sedgwick spokesperson told The Record Media: “Following the detection of the incident, we initiated our incident response protocols and engaged external cybersecurity experts through outside counsel to assist with our investigation of the affected isolated file transfer system.”
The company emphasised segmentation: “Importantly, Sedgwick Government Solutions is segmented from the rest of our business, and no wider Sedgwick systems or data were affected. Further, there is no evidence of access to claims management servers nor any impact on Sedgwick Government Solutions’ ability to continue serving its clients.”
Sedgwick, which employs over 33,000 people across 80 countries and generates multi-billion-dollar revenue, has notified law enforcement and clients while continuing operations. CISA and DHS did not respond to requests for comment.
TridentLocker has claimed 12 victims since November 2025, spanning manufacturing, government, IT, and professional services, primarily in North America and Europe, as reported by CSN.
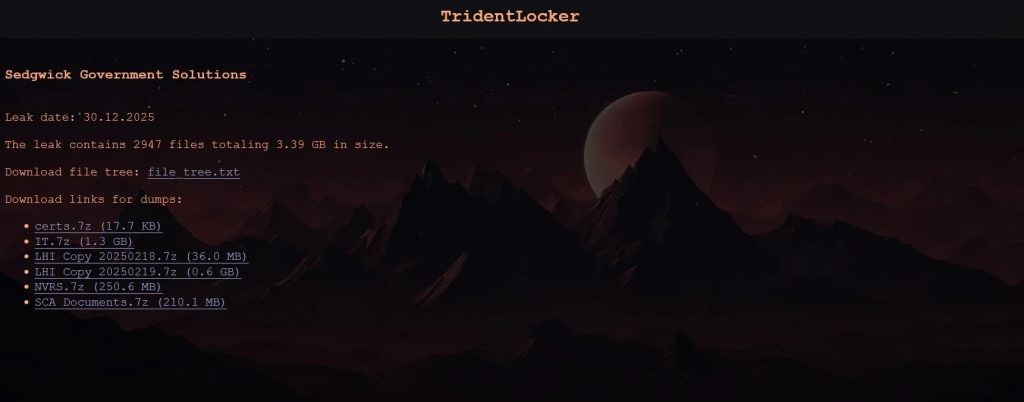
Notable prior targets include the Belgian postal service bpost, which confirmed a breach. The group uses tactics like data exfiltration over web protocols (MITRE ATT&CK T1071.001) and encryption for impact (T1486).
Federal contractors face repeated ransomware attacks; Conduent’s 2025 attack exposed data on more than 10 million people, while Chemonics suffered a breach targeting USAID work.
Experts urge enhanced segmentation, incident response, and supply chain scrutiny amid rising threats to public sector partners.
Follow us on Google News, LinkedIn, and X to Get Instant Updates and Set GBH as a Preferred Source in Google.





