Friday, November 6, 2026

Shade Ransomware Hackers Shutdown Their Operation – 750k Decryption Keys Released

Shade ransomware first spotted in late 2014, also known as Troldesh or Encoder.858. The ransomware distributed specifically through malicious email attachments.

The origin of the ransomware believed to be from Russia, the ransom notes found to be written in both Russian and English.

The threat actors behind the ransomware strain continue to enhance their capabilities. The following are the top industries targeted that include High-Tech, Wholesale, and Education.

Researchers believe the ransomware is possibly targeting more English-speaking users, once the files encrypted it appends [.crypted000007] extension at the end.

In the late 2019 Shade ransomware operators have stopped distribution of the ransomware.

Shade Ransomware Shutdown

The operators behind the Shade ransomware announced the shutdown of the ransomware now and they also published all the decryption keys.

Along with decryption keys they also publish decryption software to helps users to decrypt the encrypted files.

“All other data related to our activity (including the source codes of the trojan) was irrevocably destroyed. We apologize to all the victims of the trojan and hope that the keys we published will help them to recover their data,” reads the GitHub post published.

“We also hope that having the keys, antivirus companies will issue their own more user-friendly decryption tools.”

Also, the Shade ransomware operators believe the published keys will help the victims of the ransomware to decrypt the files and recover their data.
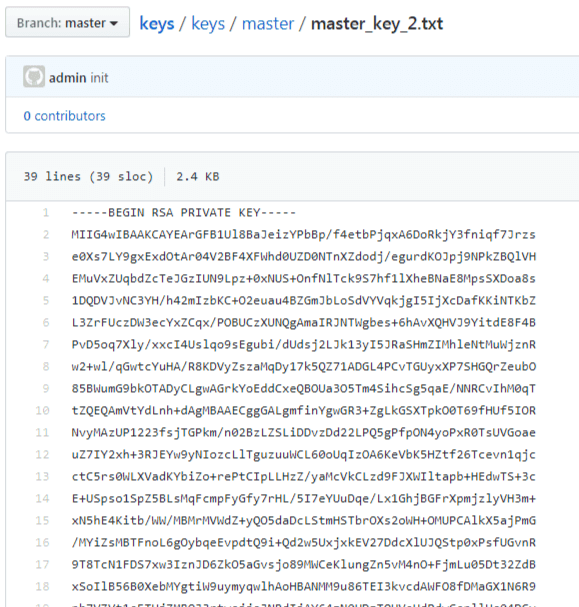
Shade Ransomware
Shade Ransomware keys

The ransomware operators also published detailed instructions on how to decrypt the files.

Kaspersky Lab’s Sergey Golovanov said that the key is working and the decryption tools will be available soon.

You can also read the complete ransomware mitigation checklist

Gurubaran
Gurubaran
Gurubaran is a co-founder of Cyber Security News and GBHackers On Security. He has 10+ years of experience as a Security Consultant, Editor, and Analyst in cybersecurity, technology, and communications.

Hot this week

How To Access Dark Web Anonymously and know its Secretive and Mysterious Activities

What is Deep Web The deep web, invisible web, or...

How to Build and Run a Security Operations Center (SOC Guide) – 2023

Today’s Cyber security operations center (CSOC) should have everything...

Russian Hackers Bypass EDR to Deliver a Weaponized TeamViewer Component

TeamViewer's popularity and remote access capabilities make it an...

Web Server Penetration Testing Checklist – 2026

Web server pentesting is performed under three significant categories: identity,...

ATM Penetration Testing – Advanced Testing Methods to Find The Vulnerabilities

ATM Penetration testing, Hackers have found different approaches to...

Storm-2603 Hackers Exploit SharePoint and Abuse Cloudflare Tunnel to Hide Remote Access

A December intrusion to Storm-2603, the China-based group Microsoft...

New GhostMap Android Vulnerability Can Crash Phones Permanently Without Opening an App or Granting Permissions

Bitdefender researchers have revealed a vulnerability called GhostMap that...

ARTEX AI Framework Linked to Bank Breaches and Cloud Attacks Found Exposed Across Hundreds of Servers

An autonomous penetration-testing framework linked to South Korean banking...

OpenMatter Network Positions Decentralized Computing as an Alternative to Data Centers for AI

Melbourne, Florida, November 5th, 2026, CyberNewswire OpenMatter Network, a pioneer...

Related Articles

Recent News



