
Shai-Hulud is a major cybersecurity threat targeting the open-source software supply chain.
Security researchers are raising alarms over “Shai-Hulud,” a self-propagating npm worm designed to steal sensitive developer credentials from GitHub, AWS, Kubernetes, and local environments.
The campaign, tracked by SlowMist’s MistEye threat intelligence platform, is already being described as one of the largest npm supply chain threats in recent years, with hundreds of malicious packages identified.
Rather than a leak, researchers confirm this was a deliberate “capability diffusion” strategy effectively turning a private cyber weapon into a public toolkit for attackers worldwide.
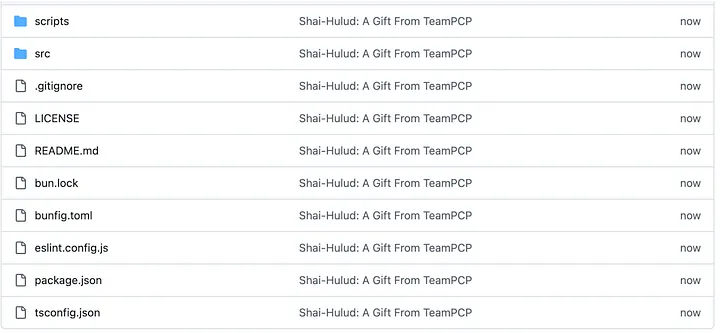
TeamPCP didn’t just publish code they provided a complete operational package. The group used compromised GitHub accounts to distribute repositories, included detailed deployment instructions, and even labeled projects with the phrase “A Gift From TeamPCP,” a move widely seen as both ironic and provocative.
Medium said in a report shared with GBhackers, On May 12, the threat group known as TeamPCP escalated the situation dramatically by releasing the full source code of Shai-Hulud on GitHub.
Security analysts warn that multiple forks and variants are already appearing, signaling rapid adoption by copycat actors.
Shai-Hulud Worm Steals Dev Secrets
At its core, Shai-Hulud is engineered for GitHub Actions CI/CD environments but extends far beyond them. Once executed, the malware activates automatically via npm scripts and begins harvesting credentials from multiple sources simultaneously.
The malware targets:
- Local files and developer tools, including GitHub CLI tokens.
- AWS credentials via IMDS and web identity tokens.
- Kubernetes service account tokens from default paths.
- Environment variables and API secrets.
Collected data is encrypted using AES-256-GCM and exfiltrated to a command-and-control (C2) server disguised as a legitimate domain, “git-tanstack.com,” mimicking the popular TanStack project.
What makes Shai-Hulud particularly dangerous is its ability to self-propagate. Once it captures valid npm tokens, it automatically modifies legitimate packages by injecting malicious preinstall scripts and republishing them to the registry.
This allows the worm to spread silently through trusted dependencies, infecting downstream developers without direct interaction.
Additionally, the malware abuses GitHub Actions workflows by exporting repository secrets into build artifacts, which are then retrieved by attackers. If direct exfiltration fails, it falls back to committing stolen data into repositories using stolen tokens.
One of the most notable features is Shai-Hulud’s specific targeting of developer environments using AI-assisted tools like Claude Code. The malware modifies configuration files such as ~/.claude.json and injects execution hooks to run malicious code automatically.
It also embeds a so-called “Anthropic Magic String,” designed to evade analysis by AI-based security tools, highlighting the attackers’ deep understanding of modern developer workflows.
Shai-Hulud includes a powerful regex engine capable of identifying high-value tokens with precision, including GitHub personal access tokens, npm tokens, and GitHub App JWTs. This enables efficient extraction of credentials at scale.
Researchers describe the malware as professional-grade, with modular architecture and enterprise-level coding practices.
A notable detail in the code excludes Russian-language systems from infection, suggesting possible ties to Russian-speaking regions a pattern seen in previous cybercrime operations.
By open-sourcing Shai-Hulud, TeamPCP has fundamentally changed the threat landscape. What was once a controlled tool is now accessible to anyone, dramatically lowering the barrier to launching supply chain attacks.
Early signs show active modifications by other actors, including expanded platform support and new infection methods. Security teams are now tracking repositories using the phrase “A Gift From TeamPCP” as part of ongoing investigations.
With the worm actively evolving and spreading, developers and organizations relying on open-source dependencies face a growing and unpredictable threat.
Indicators of Compromise
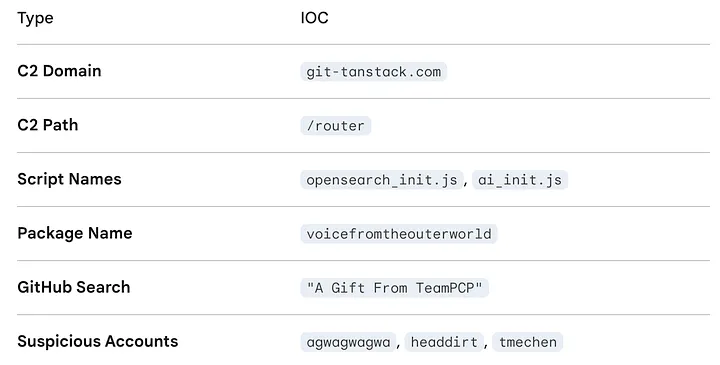
Note: IP addresses and domains are intentionally defanged (e.g., [.]) to prevent accidental resolution or hyperlinking. Re-fang only within controlled threat intelligence platforms such as MISP, VirusTotal, or your SIEM.
Follow us on Google News, LinkedIn, and X to Get Instant Updates and Set GBH as a Preferred Source in Google.





