

A Linux variant of the SideWalk backdoor has been developed by Chinese hackers who the Chinese government supports. Microsoft Windows OS-based systems belonging to academic institutions are targeted with this backdoor.
A high level of confidence is assigned to the threat group SparklingGoblin, also known as Earth Baku, as the source of the malware.
Moreover, the APT41, a cyberespionage group suspected of being linked to this campaign, is also thought to be involved.
Academic Sectors Were Targeted
As of the moment, security researchers at the cybersecurity company ESET have identified the SideWalk Linux backdoor as StageClient, which has been observed in the past.
There has been a report that the 360 Netlab researchers have spotted an early variant of the malware. The Specter botnet that attacks IP cameras was reported and described two years ago by security analysts.
While it has been determined that both Specter and StageClient have been identified as Linux variants of SideWalk, and also share the same roots as well.
In the past, a number of targets have been attacked with SideWalk Linux. But, in February 2021, SideWalk Linux was deployed against only one victim, and that’s a Hong Kong-based university.
During the students’ protests in May 2020, SparkGoblin had also focused its efforts on the same university, which had been compromised by the group in the past.
Considering that SparklingGoblin mainly attacks its targets in East Asia and Southeast Asia, it is a bit shocking that it has occurred here.
Threads used
There are two variants and both of them applied the ChaCha20 encrypting algorithm to counter the value of 0x0B, and it’s the initial value. While SideWalk has a particular way of doing this, and it’s something that is unique to them.
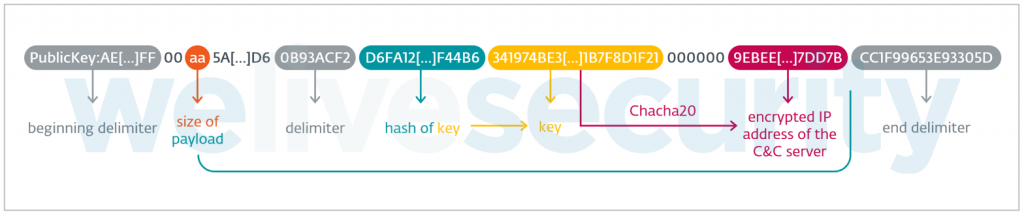
There are five identical threads used by the malware, similar to the malware running on Windows and Linux. Each thread is executed simultaneously, to carry out specific tasks, and here below we have mentioned all the threads used:-
- [StageClient::ThreadNetworkReverse]
- [StageClient::ThreadHeartDetect]
- [StageClient::ThreadPollingDriven]
- [StageClient::ThreadBizMsgSend]
- [StageClient::ThreadBizMsgHandler]
A Google Docs file was accessed by both Windows and Linux variants of SideWalk as well as the dead-drop resolver strings that were used to deliver the payload.
Download Free SWG – Secure Web Filtering – E-book







