

Threat intelligence teams have tracked Silver Fox (also known as Void Arachne), a China-based intrusion set that sits at the intersection of financially motivated cybercrime and APT-style espionage.
Originally associated with large-scale, profit-driven campaigns, the group has steadily adopted more advanced tradecraft, including modular backdoors, rootkits, and the exploitation of vulnerable drivers.
TDR’s monitoring between 2025 and early 2026 highlights a three-wave evolution tied to tax-themed phishing operations across South Asia.
In the first wave, Silver Fox leaned on its flagship ValleyRAT (aka Winos) backdoor, delivered through malicious PDF attachments that impersonated national tax authorities.
According to the report, Recent activity shows Silver Fox retooling again, this time moving away from traditional RAT-heavy chains toward misused remote monitoring tools and a custom Python stealer masquerading as a WhatsApp utility.
These lures rode on real-world communications around Taiwan’s profit-seeking enterprise tax audit window, increasing credibility and click-through rates.
Silver Fox Tax Audit Phishing
Victims received short, official-looking emails with a PDF that mimicked a Ministry of Finance announcement; opening the file triggered a multi-stage chain culminating in ValleyRAT.
Technically, the initial infection relied on a PDF with a hidden clickable annotation that fetched a ZIP archive from Tencent Cloud (myqcloud) infrastructure.
The archive contained a DLL (python311.dll) used as a loader and an executable that ultimately executed ValleyRAT, whose configuration was retrieved from a decoy JPG stored under the public user directory.
From there, ValleyRAT modular plugins enabled keystroke logging, remote control, security bypass, and data exfiltration, supporting both financial abuse and potential intelligence collection.
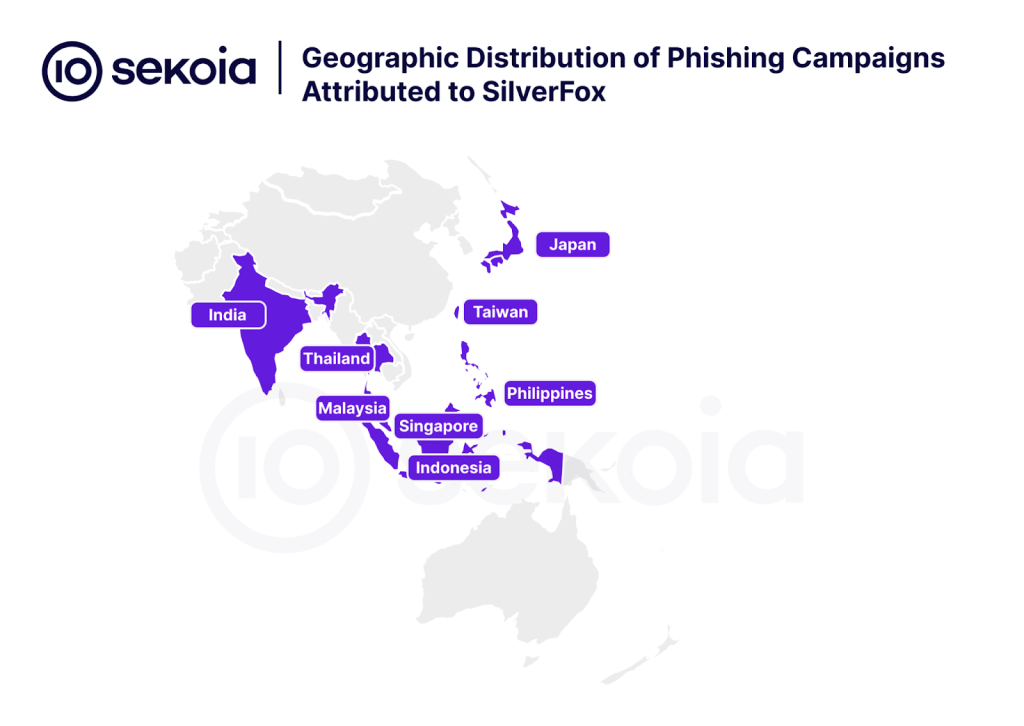
This wave primarily impacted entities in China, Taiwan, and later Japan and Malaysia, illustrating how a single lure theme was repurposed for multiple geographies.
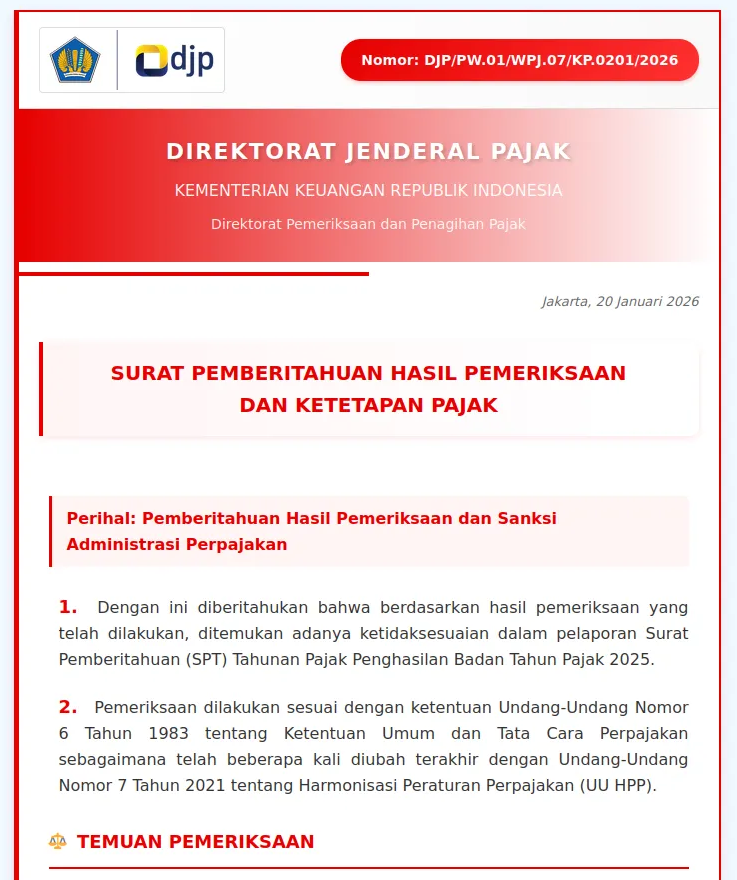
By mid-December 2025, a second wave signaled a notable operational pivot. Instead of delivering ValleyRAT directly, Silver Fox deployed a legitimate Chinese Remote Monitoring and Management (RMM) tool signed by SyncFutureTec Company Limited, obtained via tax-themed phishing websites linked from emails.
The RMM installer’s filename embedded an IPv4 address followed by “ClientSetup.exe,” with the IP string acting as the command-and-control endpoint, allowing attackers to pass C2 parameters without modifying the signed binary.
This misconfiguration abuse preserved the tool’s digital signature, helped evade static trust controls, and expanded targeting to Malaysia, the Philippines, Thailand, Indonesia, Singapore, and India.
The third and latest wave, observed in February 2026, replaced the RMM payload with a compiled Python stealer hidden behind a fake WhatsApp backup application.
Python Stealers: A Growing Threat
The phishing site, localized in Malay and hosted on infrastructure in the 154.201.87[.]0/24 range, delivered an executable that collected browser and application artefacts and uploaded them to a C2 at xqwmwru[.]top using a custom User-Agent string “WhatsAppBackup/1.0.”
Artefacts such as “C:\WhatsAppBackup\WhatsAppData.zip” and a temporary lock file signpost compromised hosts, while the C2 front-end imitates WhatsApp Web to blend malicious traffic into expected patterns.
Stolen credentials can then fuel business email compromise, account takeover, and downstream fraud.
Across all three waves, the constant is Silver Fox use of culturally and bureaucratically familiar tax or payroll lures rather than any specific malware family.
TDR assesses that the ValleyRAT and HoldingHands toolkit remains available for higher-value, espionage-leaning operations, while RMM abuse and the Python stealer better fit scalable, profit-oriented campaigns.
This dual-track posture combining opportunistic financial crime with selective APT-like intrusions mirrors a broader 2025–2026 trend where the boundary between state-linked espionage and cybercrime continues to blur.
For defenders in South Asia and beyond, spotting tax-season phishing tied to remote tools or “WhatsApp backup” utilities may now be the clearest early warning of Silver Fox activity.
Follow us on Google News, LinkedIn, and X to Get Instant Updates and Set GBH as a Preferred Source in Google.


, a China-based intrusion set that sits at the intersection of financially motivated cybercrime.)