

Researchers from Microsoft discovered a new version of PowerShell Based Malware sLoad 2.0 that using Background Intelligent Transfer Service (BITS) for malicious activities to attack Windows systems.
Microsoft called this new version as “Starslord” based on strings in the malware code, and this new version Sload 2.0 comes with an anti-analysis trick that helps attackers to isolate the malware analyst machine and the actual target machine.
Researchers believe that the new version 2.0 of the Sload campaign attack chain similar to the previous version and the malware authors added some updates.
In this new update, attackers added a dropping the dynamic list of command-and-control (C2) servers and upload screenshots.
Starslord (Sload 2.0) infection Process
Attackers launch the first stage of trojan via a spam email campaign with a malicious attachment that contains a WSF script and dummy GIF file.
A Windows Script File(WSF) is a file type used by the Microsoft Windows Script Host. It allows mixing the scripting languages JScript and VBScript within a single file, or other scripting languages such as Perl, Object REXX, Python, or Kixtart if installed by the user.
WSF script performs the BITS job and starts a process to download a PowerShell script with .jpg extension.
PowerShell drops 4 Random files – main.ini, domain.ini, <random>.tmp, <random>.ps1 and the PowerShell schedules to run the <random>.tmp which turns to <random>.ps1 in every 3 min.
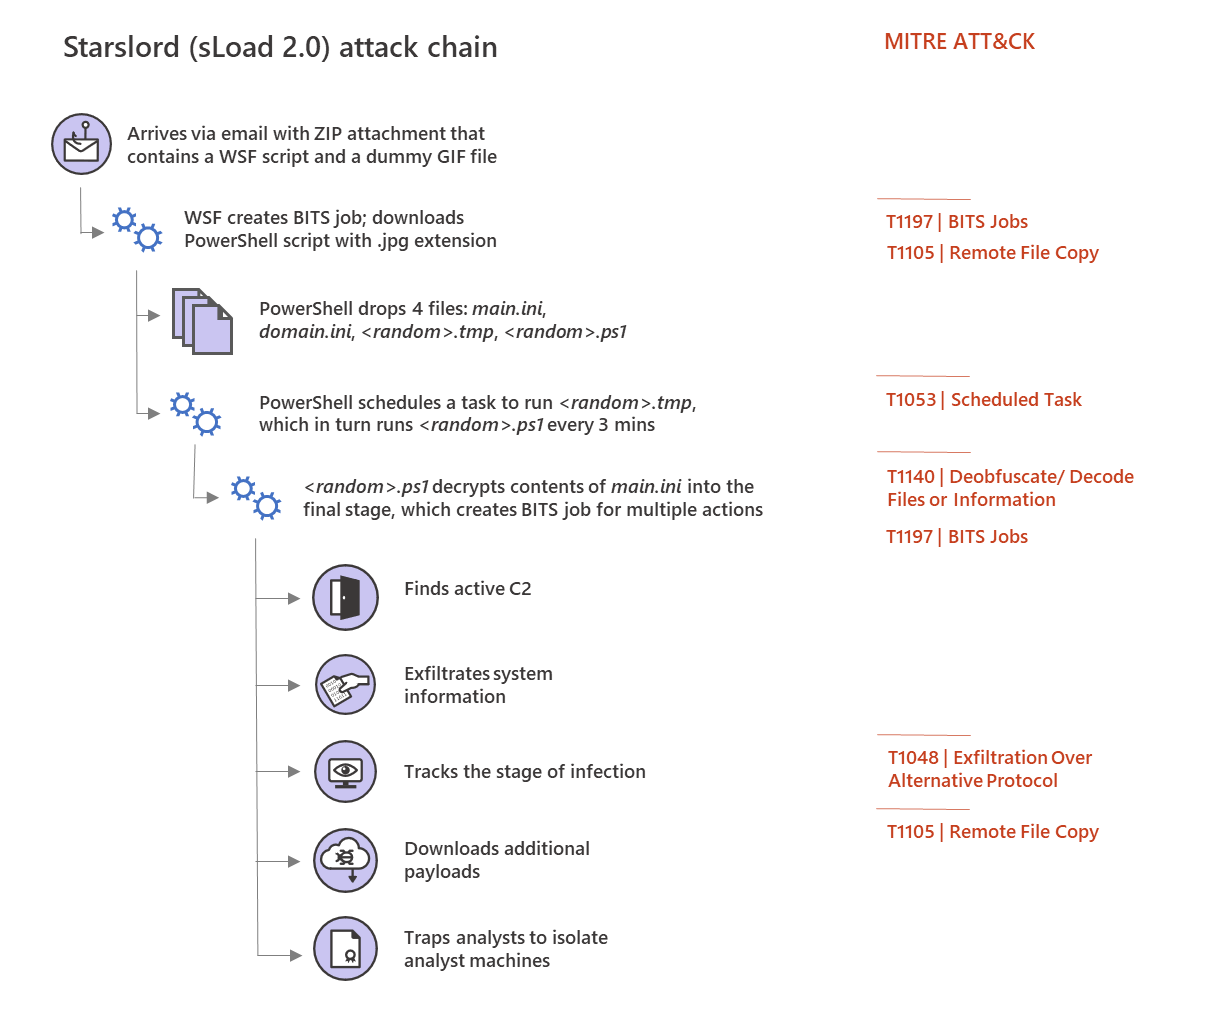
<random>.ps1 decrypts the content of main.ini In order to perform multiple infections such as exfiltration data, download additional payload, Tracking the stage of infection and isolate the analyst machine.
According to Microsoft APT research ” With the ability to track the stage of infection, malware operators with access to the Starslord backend could build a detailed view of infections across affected machines and segregate these machines into different groups. “
To perform an anti-analysis trap, Starslord comes built-in with a function named checkUniverse to determine if a host is an analyst machine.
Attackers also can track and group affected machines based on the stage of infection using Starslord that can allow for unique infection paths.
sLoad’s multi-stage attack chain, use of mutated intermediate scripts and BITS as an alternative protocol, and its polymorphic nature which makes piece malware that can be quite difficult to detect.” Microsoft APT said.
Also Read:
Unpatched Critical IE Browser Zero-Day Vulnerability Affected Millions of Windows Users
FTCODE Ransomware Attack Windows To Encrypt Files & Steals Stored Login Credentials From Browsers
LuckyMouse Chinese APT Malware Launching Weaponized Waterholing Attack on Government Data Center







)