

SloppyLemming, an India-linked espionage group also known as Outrider Tiger and Fishing Elephant, has run a year-long cyber campaign against high‑value targets in Pakistan and Bangladesh using a new BurrowShell backdoor and a Rust-based remote access tool (RAT).
This activity builds directly on earlier operations exposed by Cloudflare’s CloudForce One in 2024. However, it shows clear expansion in both tooling and infrastructure scale.
Arctic Wolf links this campaign to SloppyLemming with moderate confidence, citing a consistent South Asia victim profile, reuse of Cloudflare Workers infrastructure, familiar domain typosquatting patterns, and continued reliance on frameworks like Havoc alongside custom malware.
Arctic Wolf observed SloppyLemming targeting government agencies and critical infrastructure operators in Pakistan and Bangladesh, including defense, telecom, energy, financial, and nuclear regulatory organizations.
Dual Attack Chains
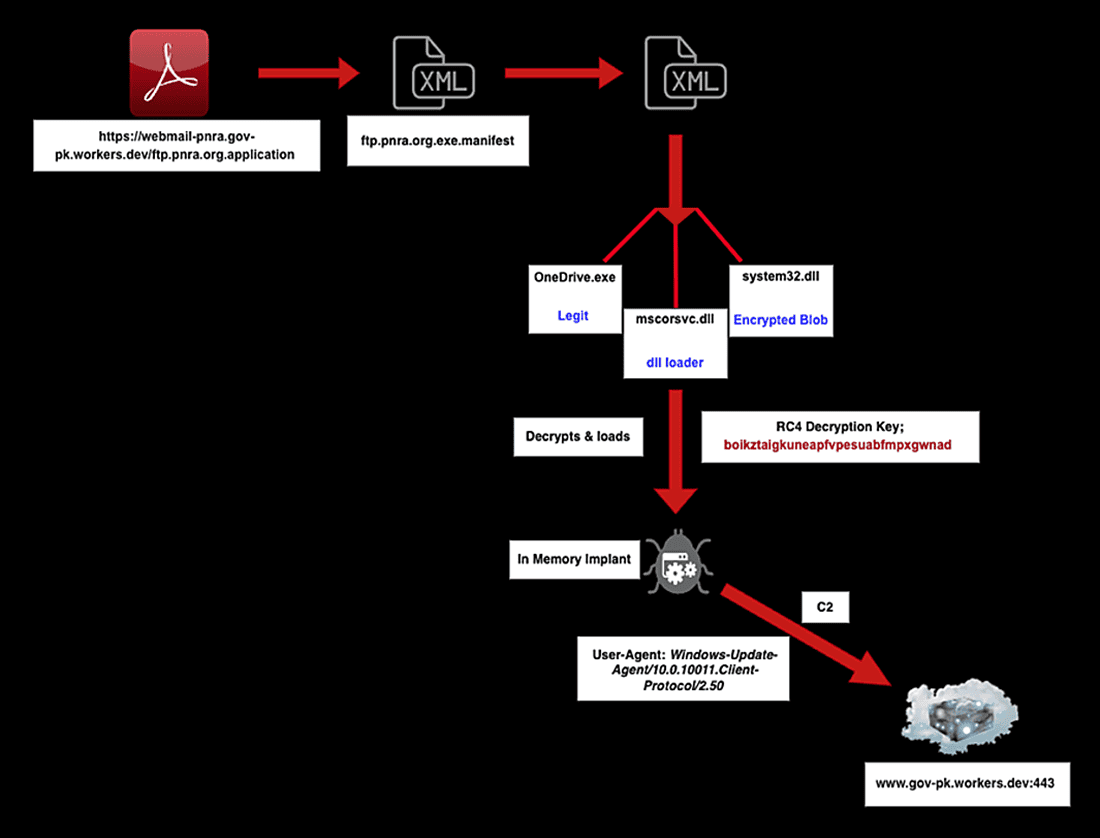
SloppyLemming now uses two main spear‑phishing chains to deploy its malware. The primary chain sends PDF lures that push victims to ClickOnce application manifests, which then deliver a DLL sideloading bundle abusing legitimate Microsoft binaries such as NGenTask.exe to load a malicious mscorsvc.dll loader and an encrypted shellcode blob.
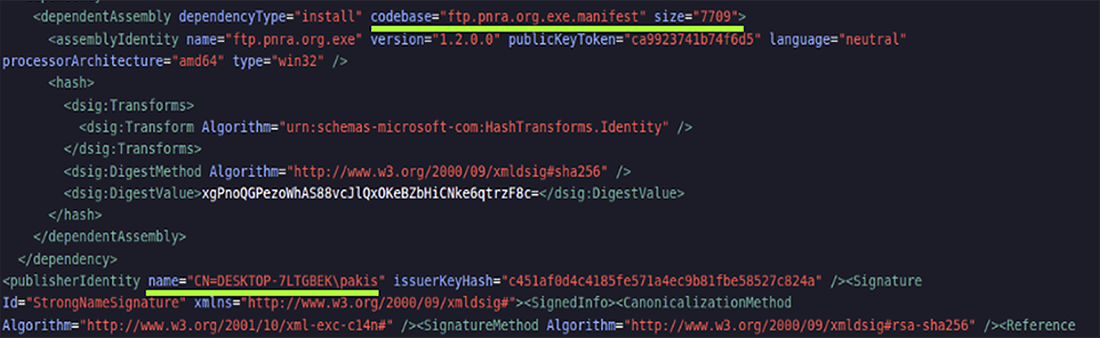
Once decrypted, that shellcode runs BurrowShell, an in‑memory backdoor that supports file operations, screenshot capture, remote command execution, and SOCKS proxy tunneling while disguising its command‑and‑control traffic as Windows Update over HTTPS.
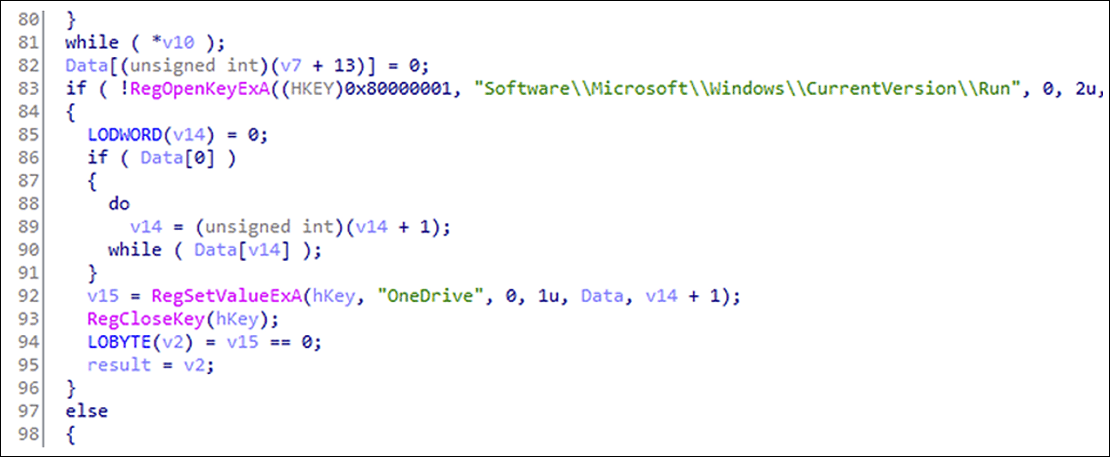
The secondary chain relies on macro‑enabled Excel files to download and execute a renamed Microsoft binary that sideloads sppc.dll, a Rust‑based keylogger and RAT.
This Rust implant logs keystrokes, runs commands, performs file manipulation, conducts port scanning and network reconnaissance, and captures screenshots, marking a shift from SloppyLemming’s earlier dependence on only traditional compiled malware and off‑the‑shelf emulation frameworks like Cobalt Strike and Havoc.
Infrastructure analysis shows SloppyLemming has greatly scaled its use of Cloudflare Workers, registering 112 workers.dev subdomains between January 2025 and January 2026, compared to just 13 such domains previously documented by Cloudflare in 2024.
These domains closely mimic Pakistani and Bangladeshi government and critical infrastructure entities and are used for both payload delivery and C2 traffic.
Despite this advanced setup, multiple Workers instances were left as open directories, unintentionally exposing staged malware, including BurrowShell components and Havoc loaders secured with distinct RC4 keys.
This operational security lapse allowed researchers to recover additional tooling and confirm SloppyLemming’s continued reliance on the Havoc framework in parallel with its new custom implants.
Impact, Attribution, and Defense
The campaign’s targeting of Pakistani nuclear regulation, defense logistics, and telecom, alongside Bangladeshi power and financial institutions, aligns with strategic intelligence collection priorities in South Asia and reinforces assessments that SloppyLemming operates in support of India‑nexus interests.
The implant includes an internal event messaging mechanism referred to as “OneCollector” in the code, likely designed to mimic legitimate Microsoft telemetry endpoints.
Additional protections include blocking known malicious workers.dev hostnames, inspecting outbound HTTPS traffic that imitates Windows Update or custom Rust‑tooling user‑agents, and deploying detection content such as YARA rules specifically tuned for BurrowShell and the Rust keylogger implants.
Arctic Wolf maps the activity across a wide span of MITRE ATT&CK techniques, including spear‑phishing, DLL search order hijacking, encrypted web C2, keylogging, and internal proxying using SOCKS tunnels.
To counter this threat, defenders are advised to tightly control macros, scrutinize PDFs and embedded URLs pointing to workers.dev domains, monitor for suspicious ClickOnce deployments, and hunt for DLL sideloading involving NGenTask.exe or phoneactivate.exe in non‑standard paths.
Follow us on Google News, LinkedIn, and X to Get Instant Updates and Set GBH as a Preferred Source in Google.


