

A previously unknown remote access trojan (RAT), dubbed SLOTAGENT, after analyzing a suspicious ZIP archive uploaded from Japan to a public malware repository in early 2026.
The malware demonstrates advanced evasion techniques and flexible post-exploitation capabilities, making it a notable addition to the evolving threat landscape.
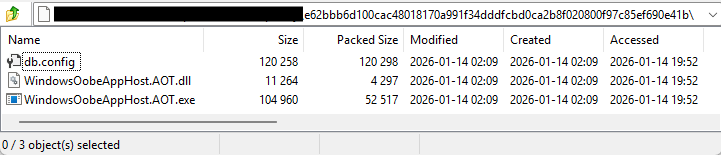
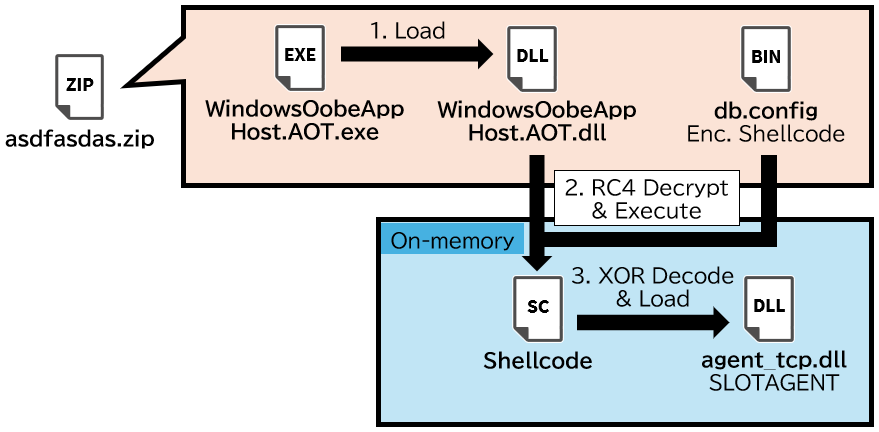
The ZIP file contains a malicious executable, WindowsOobeAppHost.AOT.exe, which triggers the execution chain by loading a DLL file, WindowsOobeAppHost.AOT.dll. The DLL exports a function named __managed__Main, which initiates the malware’s core logic.
SLOTAGENT employs a multi-stage loading mechanism that complicates analysis. At runtime, the loader dynamically resolves Windows API functions using a custom API hashing algorithm based on XOR operations and ROR11 bit rotation.
The malware then decrypts data stored in a file named db.config using RC4 encryption, leveraging a key derived during execution. The decrypted payload is executed as shellcode using low-level Windows APIs such as NtCreateThreadEx.
In early 2026, IIJ discovered unknown malware contained in a ZIP file uploaded from Japan to a public malware repository.
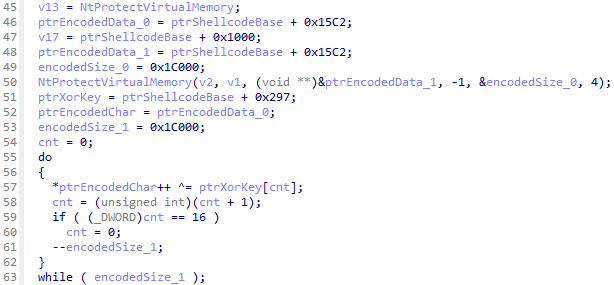
Inside the shellcode, an XOR-encoded DLL payload is embedded. This payload is decoded using a 16-byte key located at a specific memory offset and is then reflectively loaded into memory.
The final payload is the SLOTAGENT RAT itself, internally referred to as agent_tcp.dll.
Command-and-Control Communication
Once active, SLOTAGENT establishes communication with a hardcoded command-and-control (C2) server at 43.156.59[.]110:699 over TCP. It uses a proprietary protocol that mimics structured HTTP-like communication.
The malware sends data in stages:
- A 4-byte length field.
- A path string such as /api/v1/stream/data.
- A JSON-formatted payload.
- A delimiter to mark the end of the message.
During initial communication, SLOTAGENT collects and transmits detailed host information, including system name, username, IP address, MAC address, OS version, process ID, and privilege level. It also includes random byte sequences likely used for tracking or obfuscation.
SLOTAGENT supports a wide range of commands, enabling attackers to control infected systems fully. Key functionalities include:
- Screenshot capture in BMP format.
- File upload and download (including chunked transfers).
- Remote shell execution.
- System and process enumeration.
- File system navigation and manipulation.
- Memory dumping of processes.
- Execution of Beacon Object Files (BOF), similar to Cobalt Strike.
- Timestamp tampering (time stomping) for anti-forensics.
- Self-deletion and cleanup via the “destroy” command.
The shellcode contains an XOR-encoded SLOTAGENT (DLL file), which is then XOR-decoded using a 16-byte key located at offset 0x297 after execution, and then reflectively loaded.
These features indicate that SLOTAGENT is designed for both espionage and post-exploitation operations.
Anti-Analysis Techniques
SLOTAGENT incorporates multiple layers of defense against reverse engineering. In addition to API hashing, it uses string encryption based on a TEA-like algorithm.
SLOTAGENT calls multiple Windows API functions during execution, but the addresses of these API functions are dynamically resolved at runtime using API hashing with a DJB2-based algorithm.

To support defenders, researchers released an IDA Python script that can decrypt these strings statically, significantly improving malware analysis and threat hunting workflows.
Critical strings, including command names, are encrypted and only decrypted at runtime, making static analysis ineffective.
The script is publicly available on GitHub and can assist incident responders in identifying SLOTAGENT infections.
The discovery of SLOTAGENT highlights the continued evolution of RAT malware toward stealth, modularity, and anti-analysis resilience.
Its use of BOF execution and layered encryption aligns it with modern offensive frameworks, suggesting possible use in targeted attacks.
Organizations are advised to monitor unusual outbound TCP connections, inspect encrypted payload execution patterns, and leverage behavioral detection to identify similar threats.
IOCs
| SHA256 | explanation |
|---|---|
| e62bbb6d100cac48018170a991f34dddfcbd0ca2b8f020800f97c85ef690e41b | ZIP archive containing the files required for execution |
| 97e0714ee7279feb558aa38ab9d4c279731d3000c501aff7ad5c2967c3cb987f | Encrypted SLOTAGENT ( db.config) |
| c1681d3aae736585c1dd656fe3ad66dafd3712ad4125e09fc97a4f1e5f367548 | SLOTAGENT loader ( WindowsOobeAppHost.AOT.dll) |
| a9c46b67ff938930b16b377df9ddf86f3a56ef9876267387f30299a069c98472 | SLOTAGENT (executes in memory) |
Follow us on Google News, LinkedIn, and X to Get Instant Updates and Set GBH as a Preferred Source in Google.





, dubbed SLOTAGENT, after analyzing a suspicious ZIP archive uploaded from Japan to a public malware repository in early 2026.)