

Attackers have been observed distributing a modular Remote Access Trojan (RAT) through the npm ecosystem by deliberately splitting malicious functionality across multiple seemingly benign packages, enabling the campaign to evade traditional code review and detection mechanisms for over three months.
The activity was uncovered during analysis of a compromised npm package, lib-mtop, which contained a basic downloader.
Although originally published years earlier, three new versions appeared in late March 2026, suggesting a potential maintainer account takeover or malicious repurposing.
The package itself masqueraded as an unscoped clone of a private @ali namespace dependency, commonly used internally by Alibaba, making it particularly attractive in enterprise development environments referencing those packages.
While the loader inside lib-mtop relied on a straightforward pattern fetching remote JavaScript via curl and executing it using Node.js require() further investigation revealed a far more sophisticated supply chain attack.
The same maintainer account also published additional packages including aone-kit, aone-kit-cli, and aone-sandbox, which acted as empty wrappers mimicking private Alibaba packages.
However, the package local-config-parser stood out due to its legitimate functionality, implementing JSON-based rule parsing with sandboxed execution via Node.js vm.
Individually, these packages appeared harmless. Combined, they formed a staged malware delivery chain.
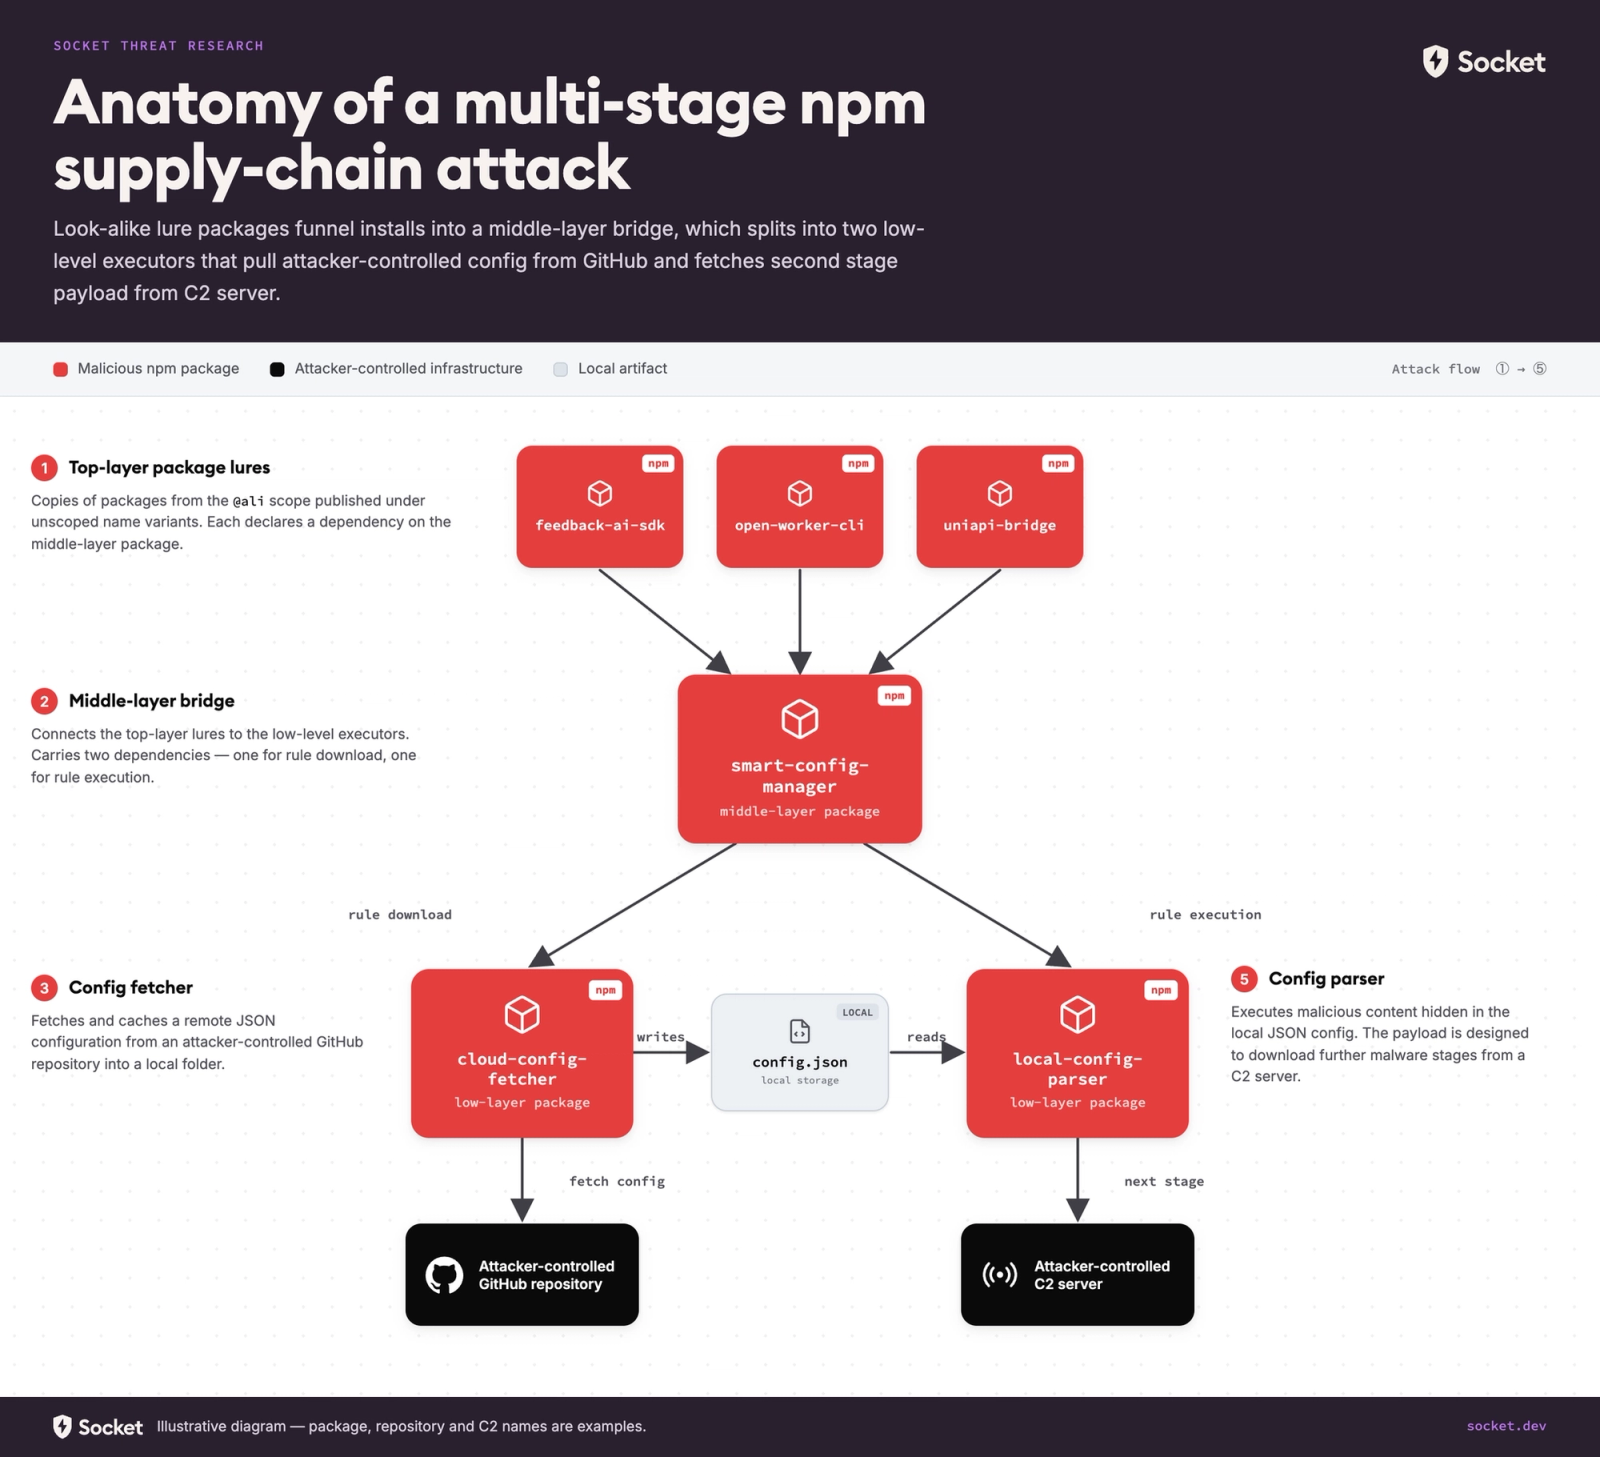
At the top layer, lure packages such as aone-cloud-cli, open-worker-cli, and uniapi-bridge triggered installation chains by referencing private @ali dependencies.
These packages introduced a shared intermediary dependency, smart-config-manager, which linked to two critical components: cloud-config-fetcher and local-config-parser.
The infection chain relied on a distributed execution model. The cloud-config-fetcher module retrieved a remote configuration file from a GitHub repository controlled by the attackers storing it locally as .cloud-preferences.json.
This file was then parsed by local-config-parser, which executed embedded rules using the vm module.
The malicious payload was concealed within these rules. Although the surrounding code appeared to perform benign transformations, hidden logic exploited a known sandbox escape technique using the Function constructor: F(′returnprocess′)().
This allowed attackers to break out of the vm isolation and gain access to the host environment, including Node.js internals such as require and module loaders.
Once execution was achieved, the malware fetched a secondary payload from an Alibaba Cloud-hosted endpoint blending malicious traffic with legitimate cloud infrastructure.
This stage performed reconnaissance, environment fingerprinting, and deployed platform-specific persistence mechanisms.
Socket Researchers said that, the campaign leveraged at least 15 npm packages published across multiple maintainer accounts to obscure attribution and avoid detection.
On Windows systems, it replaced components of Alibaba’s Alilang security application, while on Linux and macOS it leveraged background execution and scheduled persistence.
Split RAT Components Across npm
The final payload, identified as aone-cli, is a fully featured cross-platform RAT designed for targeted espionage.
It supports command execution, file exfiltration, reverse proxy tunneling, and lateral movement via enterprise collaboration tools such as DingTalk.
Notably, it also includes mechanisms to poison AI-assisted development tools by injecting malicious code into Python scripts located in tool-specific directories.
Command-and-control (C2) communication is obfuscated using spoofed HTTP headers referencing legitimate Alibaba services such as alidocs.dingtalk.com.
The RAT continuously polls its C2 server and supports a wide command set, including system reconnaissance, module installation, and arbitrary code execution.
Infrastructure analysis shows that multiple npm publisher accounts were created within a narrow timeframe in late April 2026, aligning with the staged rollout of the attack chain.
Additionally, GitHub commits associated with the malicious configuration and payloads were timestamped in China Standard Time (UTC+0800) and contained Chinese-language comments, suggesting but not conclusively proving a Chinese-speaking threat actor.
The campaign demonstrates a notable evolution in supply chain attacks, where malicious logic is fragmented across multiple packages to bypass isolated code audits.
By ensuring each component appears benign in isolation, attackers significantly reduce the likelihood of detection.
Given the targeting of Alibaba’s internal tooling ecosystem and the RAT’s espionage capabilities, the operation is likely aimed at corporate intelligence gathering.
Despite relatively low download counts, the targeted nature and lateral movement features make impact assessment difficult, especially as the infrastructure remained active months after deployment.
IOCs
| Package name |
|---|
| lib-mtop |
| aone-kit |
| aone-kit-cli |
| aone-sandbox |
| local-config-parser |
| smart-config-manager |
| cloud-config-fetcher |
| fast-transform-pipeline |
| aone-cloud-cli |
| colder-cli |
| def-open-client |
| feedback-ai-sdk |
| flight-compare-analyzer |
| lwp-web-client |
| lzd-unified-station-sdk |
| open-worker-cli |
| test-skill-zip |
| uniapi-bridge |
Note: IP addresses and domains are intentionally defanged (e.g., [.]) to prevent accidental resolution or hyperlinking. Re-fang only within controlled threat intelligence platforms such as MISP, VirusTotal, or your SIEM.
What Features Should AI SOC Have in 2026? A Complete Checklist : Download the AI SOC Features Checklist


 through the npm ecosystem by deliberately splitting malicious functionality.)