
A coordinated social-engineering operation tracked as Spring Ring abused Microsoft Teams external accounts to impersonate corporate IT help desks, targeting more than 150 employees across at least 10 organizations between January and April 2026.
The campaign demonstrates how attackers can turn trusted collaboration channels into an initial-access route for remote-control tools, custom malware, and attempted domain-controller compromise.
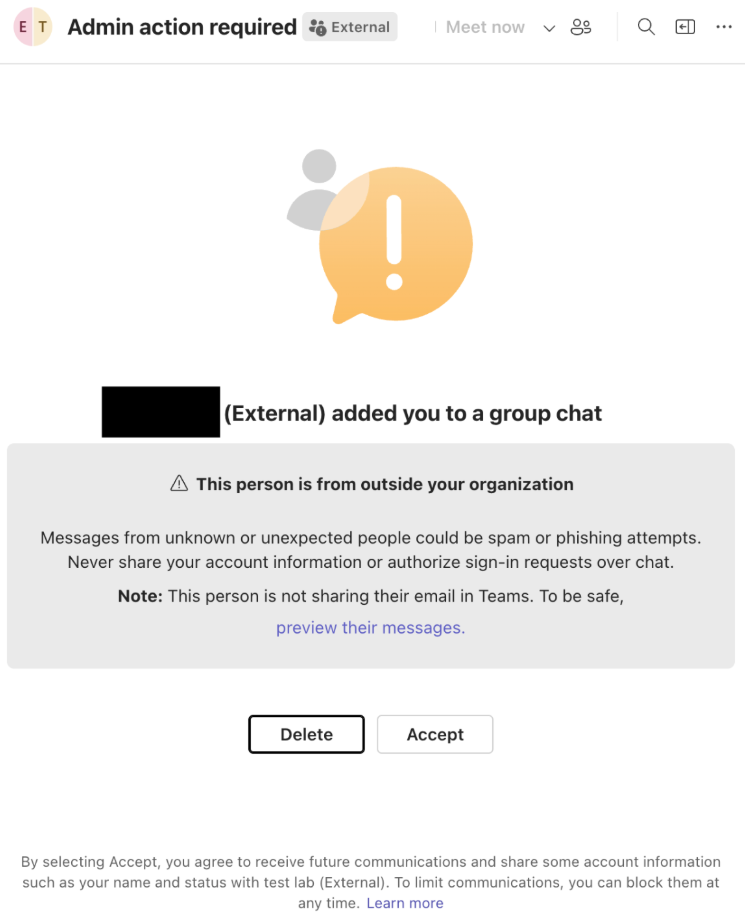
The operation relied on 26 distinct external identities that used professional-looking display names such as “Help Desk,” “IT Assistance” and “Support Staff.”
Many were hosted on attacker-controlled .onmicrosoft[.]com tenants crafted to resemble internal corporate infrastructure, including names containing terms such as “internal,” “network,” “certified” and “infrastructure.”
The campaign did not exploit a vulnerability in Microsoft Teams. Instead, it weaponized the trust employees place in collaboration platforms and the ability of external users to initiate chats.
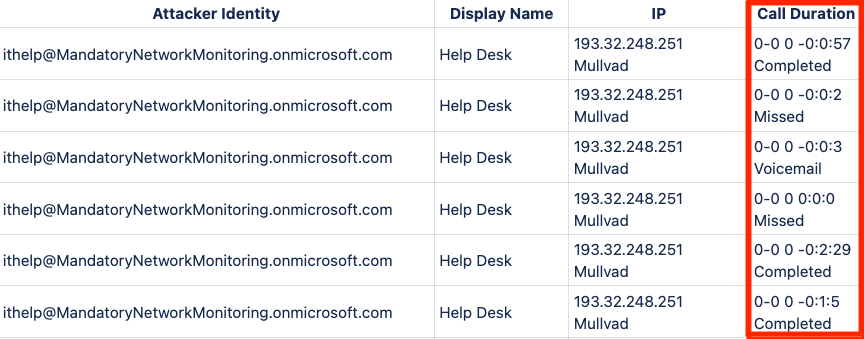
After sending a one-to-one chat request, the operators rapidly escalated to unsolicited Teams voice calls, posing as technicians who needed to troubleshoot a security or system issue.
Successful calls commonly lasted 10 to 15 minutes long enough to persuade victims to run software, visit attacker-controlled links or grant remote access.
Spring Ring’s defining feature is its use of real-time voice phishing, or vishing. Unlike conventional email phishing, the attackers could adjust their script in response to a victim’s questions and apply urgency during a live call.
This interaction lowered the barrier to user execution. In some cases, victims were instructed to launch Windows Quick Assist or install third-party remote monitoring and management software.
Once the victim granted control, the fake technician had an interactive foothold on the endpoint.
The technique illustrates why legitimate RMM software remains attractive to attackers: it can blend into routine IT-support activity while providing remote access without requiring an exploit.
The campaign also reflects a wider shift toward collaboration-platform abuse. Unit 42 reported that alerts involving collaboration tools represented 42% of all Cortex phishing alerts in the first four months of 2026, compared with 30% in the preceding four-month period.
In Campaign A, after obtaining remote access through RMM tooling, attackers conducted lightweight reconnaissance with whoami /groups and net group /dom to identify user privileges and domain context.
They then executed a PowerShell command to retrieve an obfuscated remote-access Trojan from san-sid[.]com.
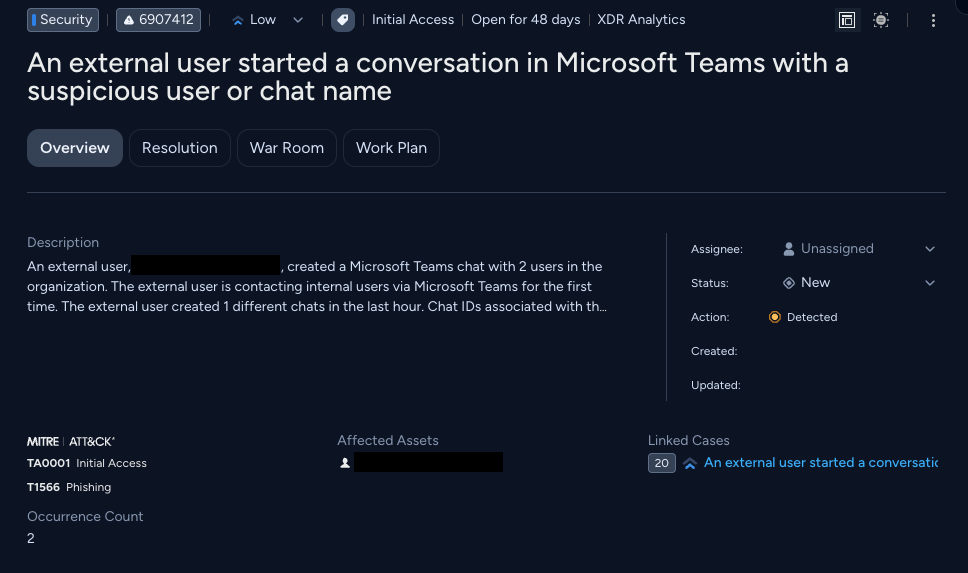
Unit 42 researchers identified Spring Ring, the after detecting suspicious creation of Teams chats across multiple Microsoft 365 tenants.
Spring Ring Campaign
The PowerShell payload used variable and arithmetic obfuscation to complicate automated analysis. Once deobfuscated, the core stager was only nine lines long.
It attempted to bypass the Windows Antimalware Scan Interface by manipulating the amsiInitFailed flag, validated the bypass, encrypted host information and contacted its command-and-control infrastructure for additional payloads.
Cortex XDR blocked the malware during execution, according to Unit 42.
This chain reinforces the continuing effectiveness of PowerShell as an execution mechanism: attackers can use trusted Windows components to fetch, decode and run follow-on payloads while reducing reliance on a large initial binary.
Campaign B used a more tailored cloud-hosting lure. Victims were sent executables hosted on Amazon S3 endpoints whose domains and filenames incorporated the target organization and employee name, such as <company>-org-filters-update-<victim>.exe.
The personalization made the download appear consistent with an internal update or policy-related workflow.
After execution, the malware copied itself into the Temp directory, created components resembling vhlp-*.exe and scnr-*.exe for persistence, and started a hidden headless Microsoft Edge process.
Attackers then sideloaded a browser extension and used Python from C:\ProgramData\IntegrityData\python.exe to scan internal systems over SMB on TCP port 445.
The most serious stage involved generating NTLM authentication traffic toward the domain controller and attempting a PetitPotam-based authentication-coercion attack.
The technique aims to force a domain controller to authenticate to attacker-controlled infrastructure, allowing the authentication flow to be relayed to another service and potentially enabling domain-level privileges.
Unit 42 Managed Detection and Response blocked the domain-takeover attempt.
Defenders should treat unsolicited external Teams chats particularly those that immediately transition into voice calls as identity-security events.
Suspicious .onmicrosoft[.]com tenants, rapid outreach to several employees, repeated short calls, unapproved RMM launches, personalized cloud downloads, headless browser activity and unexpected SMB or NTLM traffic involving domain controllers are high-value detection signals.
Organizations should restrict external Teams access where business requirements allow, verify support requests through known internal channels, enforce approved remote-support tooling, and harden NTLM relay exposure on domain infrastructure.
Above all, employees should be trained that legitimate IT teams should not request remote control or software installation through an unexpected external Teams call.
IOCs
| S. No. | IP Address |
|---|---|
| 1 | 193.32.248[.]251 |
| 2 | 193.138.7[.]142 |
| 3 | 185.65.134[.]209 |
| 4 | 178.130.47[.]46 |
| 5 | 5.181.3[.]106 |
| 6 | 2.56.172[.]214 |
| 7 | 185.234.67[.]53 |
| 8 | 45.8.157[.]185 |
| 9 | 80.66.72[.]215 |
| 10 | 136.0.20[.]6 |
| 11 | 185.213.155[.]226 |
| 12 | 185.155.99[.]161 |
Note: IP addresses and domains are intentionally defanged (e.g., [.]) to prevent accidental resolution or hyperlinking. Re-fang only within controlled threat intelligence platforms such as MISP, VirusTotal, or your SIEM.
★ Learn 7 Metric-Gated AI SOC Deployment Phases – Download Free AI SOC Deployment Playbook 2026.






