

Squirrelwaffle malware has been found in existence since the mid of September 2021. This malware is designed to cause chain infections. The Rapid Response Team at Sophos has recently discovered that the Squirrelwaffle malware loader used ProxyLogon and ProxyShell exploits for targeting Microsoft Exchange Server.
After gaining access to the vulnerable server, the attackers used the email thread hijacking technique which involves inserting malicious replies into Employees’ existing email threads to distribute the Squirrelwaffle malware to both internal and external recipients.
When they monitored further, they found that the vulnerable server was not only used for malicious spam campaigns but also for a financial fraud attack by extracting information from a stolen email thread.
Squirrelwaffle
Squirrelwaffle is a type of malware loader distributed via spam campaigns as a malicious office document. This provides information about the victim’s environment and with a channel that can be used to deliver and infect with other malware.
When a victim opens the malicious office document and enables macros, it downloads a VB script and executes Cobalt Strike Beacons which give control over the victim’s machine.
The Investigation
Usually, the Squirrelwaffle attack is ended when the defenders detect and remediate by providing patches to the vulnerable servers. But in the recent set of events, such remediation measures wouldn’t have stopped the financial fraud attack as they have already exported an email thread about customer payment from the victim’s exchange server. Hence it is recommended to investigate further for other impacts.
Typo-squatted domains were registered and used by the attackers for email thread replies.
The registered domain appears similar to the original victim’s domain but with a small typo that is often not noticed by the victims. Once they convince the victims, they use these email threads to redirect the payments.
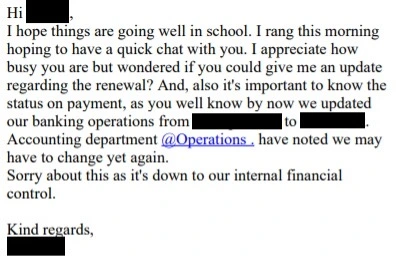
To provide additional legitimacy to the victims, they used additional email addresses from the typo-squatted domain and added them in CC of the reply emails. Just like every other phishing campaign, these attackers also provide a sense of urgency to the victims.
Prevention
It is advised to keep the Microsoft Exchange Servers updated and patched to prevent any type of compromise. Industry-recognized prevention methods such as SPF records, DKIM, and DMARC records must be standard to stop phishing campaigns. It is also necessary to provide knowledge to all the employees about Phishing attempts.
You can follow us on Linkedin, Twitter, Facebook for daily Cybersecurity updates.






