

In August 2022, hackers launched a limited wave of attacks that targeted at least 10 organizations around the world.
There are two newly disclosed zero-day vulnerabilities being exploited by the hackers in these attacks in order to gain access to and compromise Exchange servers in these attacks.
Chopper web shell was installed during these attacks in order to make hands-on keyboard access more convenient. Attackers utilize this technique to gain access to Active Directory in order to perform reconnaissance and exfiltration of data.
As a result of these wild exploits, it is likely that these vulnerabilities will be weaponized further in the coming days due to the growing trend toward weaponizing them.
0-Day Flaws Exploited
Here below we have mentioned the two 0-Day flaws exploited by the hackers in the wild to attack 10 organizations:-
- CVE-2022-41040: Microsoft Exchange Server Elevation of Privilege Vulnerability with CVSS score: 8.8.
- CVE-2022-41082: Microsoft Exchange Server Remote Code Execution Vulnerability with CVSS score: 8.8.
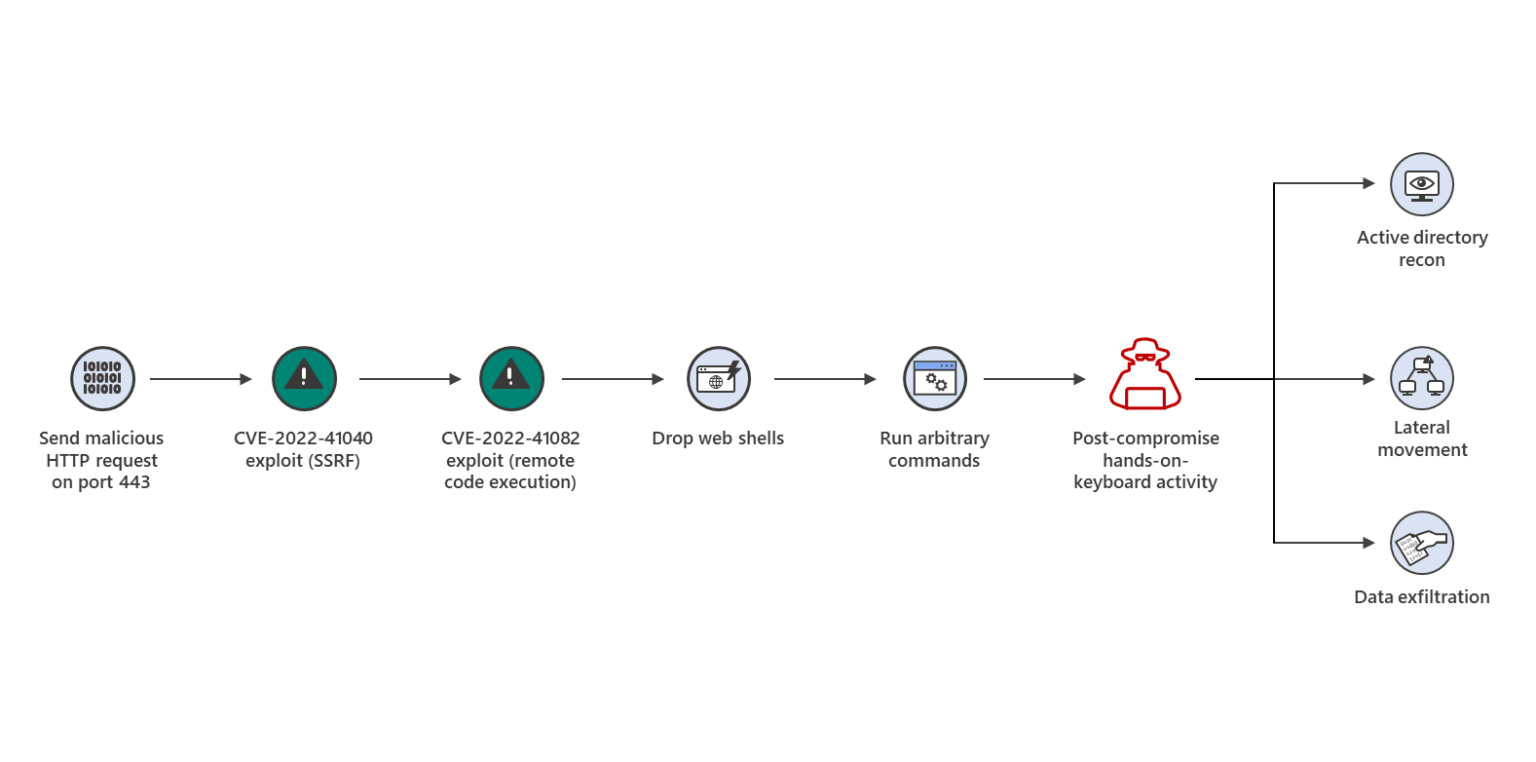
The combination of these two zero-day vulnerabilities together has been named “ProxyNotShell.” The exploitation of these vulnerabilities is possible by using a standard account with a standard authentication process.
In many different ways, it is possible to acquire the credentials of standard users. While the GTSC, a Vietnamese cybersecurity company, was the first to discover the vulnerabilities that have been exploited.
It is suspected that these intrusions were carried out by a Chinese threat actor.
Mitigation
No action is required on the part of Microsoft Exchange Online customers. Microsoft recommended reviewing the URL Rewriting Instructions for Microsoft Exchange customers using on-premises Exchange and also recommended users implement them immediately.
If you are a Microsoft Exchange Server user using Microsoft 365 Defender, then you have to follow the following checklist provided by Microsoft:-
- Enable cloud-based protection in Microsoft Defender Antivirus.
- Protect security services from being interrupted by attackers by enabling tamper protection.
- Microsoft Defender for Endpoint can detect malicious artifacts when EDR is operating in block mode.
- Protect the Internet network from malicious domains and other malicious content by enabling network protection.
- Enable full automation for investigation and remediation. By doing so Microsoft Defender for Endpoint can be notified of breaches immediately, allowing it to take immediate action.
- Discovering your network’s devices will allow you to have greater visibility into what’s going on.
While as additional prevention measures they also recommended users to:-
- Enable multi-factor authentication (MFA)
- Legacy authentication must be disabled
- Do not accept suspicious or unknown 2FA prompts
- Make sure to use complex passwords


