

A December intrusion to Storm-2603, the China-based group Microsoft ties to Warlock ransomware.
The attackers used ToolShell flaws in on-premises SharePoint and ran a memory-only webshell inside the IIS worker process.
They then layered several tunnels, including Cloudflare Tunnel, to keep access after the initial foothold was gone. Kaspersky assesses the attribution with moderate confidence.
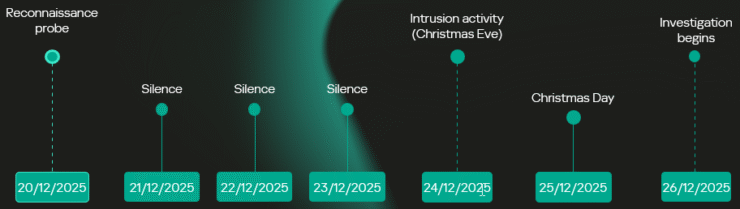
On December 20, a single request hit the SharePoint ToolPane endpoint. It came from infrastructure linked to ONYPHE, an attack-surface platform that checks for vulnerability by injecting a harmless marker rather than only listing exposed assets.
A second connection followed about 12 minutes later from a bulletproof hosting provider. Three quiet days passed before the real attack on December 24, when staffing is thin.
That gap kept analysts from correlating the probe with the later activity, and the event was treated as low priority.
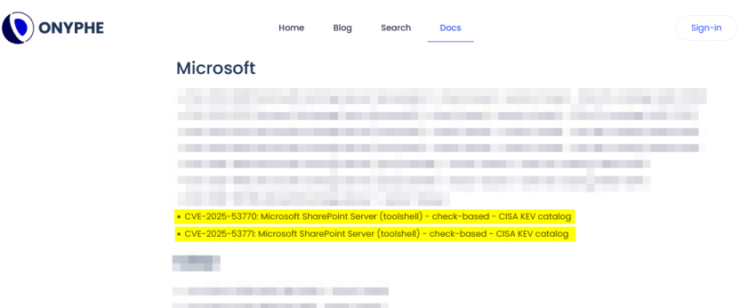
The exploit used the ToolShell chain (CVE-2025-53770 and CVE-2025-53771). These flaws bypass earlier fixes for CVE-2025-49704 and CVE-2025-49706.
Microsoft attributes the ransomware-linked exploitation to Storm-2603. Other actors, including Linen Typhoon and Violet Typhoon, focused on espionage.
The December 24 request came from 45.91.94.204, a Safing Privacy Network node, and loaded a webshell directly into w3wp.exe.
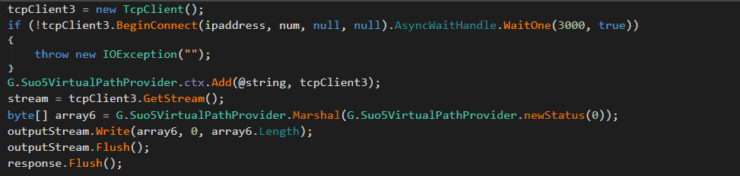
The main module, G.cs, registers a custom VirtualPathProvider and hooks GetCacheKey(). It stays dormant unless a specific User-Agent appears.
It talks to its operator over a custom XOR-obfuscated binary protocol. It also builds a full-duplex proxy using the suo5 tool, which tunnels TCP traffic through HTTP.
Helper modules download files, silently install MSI packages, list users, processes and connections, and create administrator accounts through native SAM RPC calls.
Privilege escalation to SYSTEM relies on an EfsPotato-style named-pipe impersonation. This works because the IIS worker process holds SeImpersonatePrivilege.
Next, w3wp.exe ran msiexec.exe to pull a Velociraptor installer from Supabase storage. The version was 0.73.4.0, which is vulnerable to CVE-2025-6264.
Storm-2603 Attack
Kaspersky reported Storm-2603, abusing the same open-source forensics tool in an August 2025 Warlock, LockBit incident.
ONYPHE adopted the approach used by Niels Hofmans (hazcod). Namely, it attempts to inject a harmless marker into the target server to find out if it is vulnerable.
Through Velociraptor, the actor deployed Zoho Assist, VS Code CLI tunneling, Cloudflare Tunnel and a lightweight reverse proxy.
These channels no longer depend on the webshell, the IIS lifecycle or the ToolShell bug. Defenders who recycle the application pool and patch SharePoint would still face live remote access.
They also sideloaded a DLL identified as Warlock’s AV killer. The Warlock ransomware launch was blocked by the Proactive Defense Module in Kaspersky Endpoint Security.
Kaspersky points defenders to loader events showing Microsoft.GeneratedCode and App_Web_toolpane.aspx loading together.
When a specific User-Agent is detected in the request headers, the module parses it, extracts the payload, and establishes a TCP connection to a target host inside the target’s network if needed.
Strings such as ObjectDataProvider, ExpandedWrapper and LosFormatter in those assemblies add further evidence.
The team released CLRDeserializationExploitFinder, which uses AMSI and CLR profiling to flag these gadget chains.
Microsoft’s mitigation steps are to install the SharePoint security updates and enable AMSI in Full Mode. Rotate ASP.NET machine keys, restart IIS with iisreset.exe, and deploy Defender for Endpoint or an equivalent.
For the virtual-path implant, hunt for IIS configuration ETW events 25 and 47 that map a path with no file on disk.
The expected file-monitoring events 17, 18, 19 and 21 should also be missing for that path. Treat any unapproved VirtualPathProvider as suspect.
Organizations should also hunt for unsanctioned Cloudflare tunnel clients, Zoho Assist agents and VS Code tunnels on servers.
IOCs
| Indicator of compromise | Description |
| 45.91.94[.]204 | SPN node |
| 0xFD91321BF7FF7245DDA9B7B5D791ACE8 | vskp2 – webshell implant |
| hxxps://vdfccjpnedujhrzscjtq[.]supabase[.]co/storage/v1/object/public/image/v4[.]msi | Vulnerable Velociraptor package |
| 0x3A55D8F8F29716C694671834D8C6CB29 | C:\ProgramFiles\Velociraptor\Velociraptor.exe |
Note: IP addresses and domains are intentionally defanged (e.g., [.]) to prevent accidental resolution or hyperlinking. Re-fang only within controlled threat intelligence platforms such as MISP, VirusTotal, or your SIEM.
Stops Cyber threats before impact with 21 min faster MTTR. Integrate ANYRUN’s Sandbox in your SOC.







