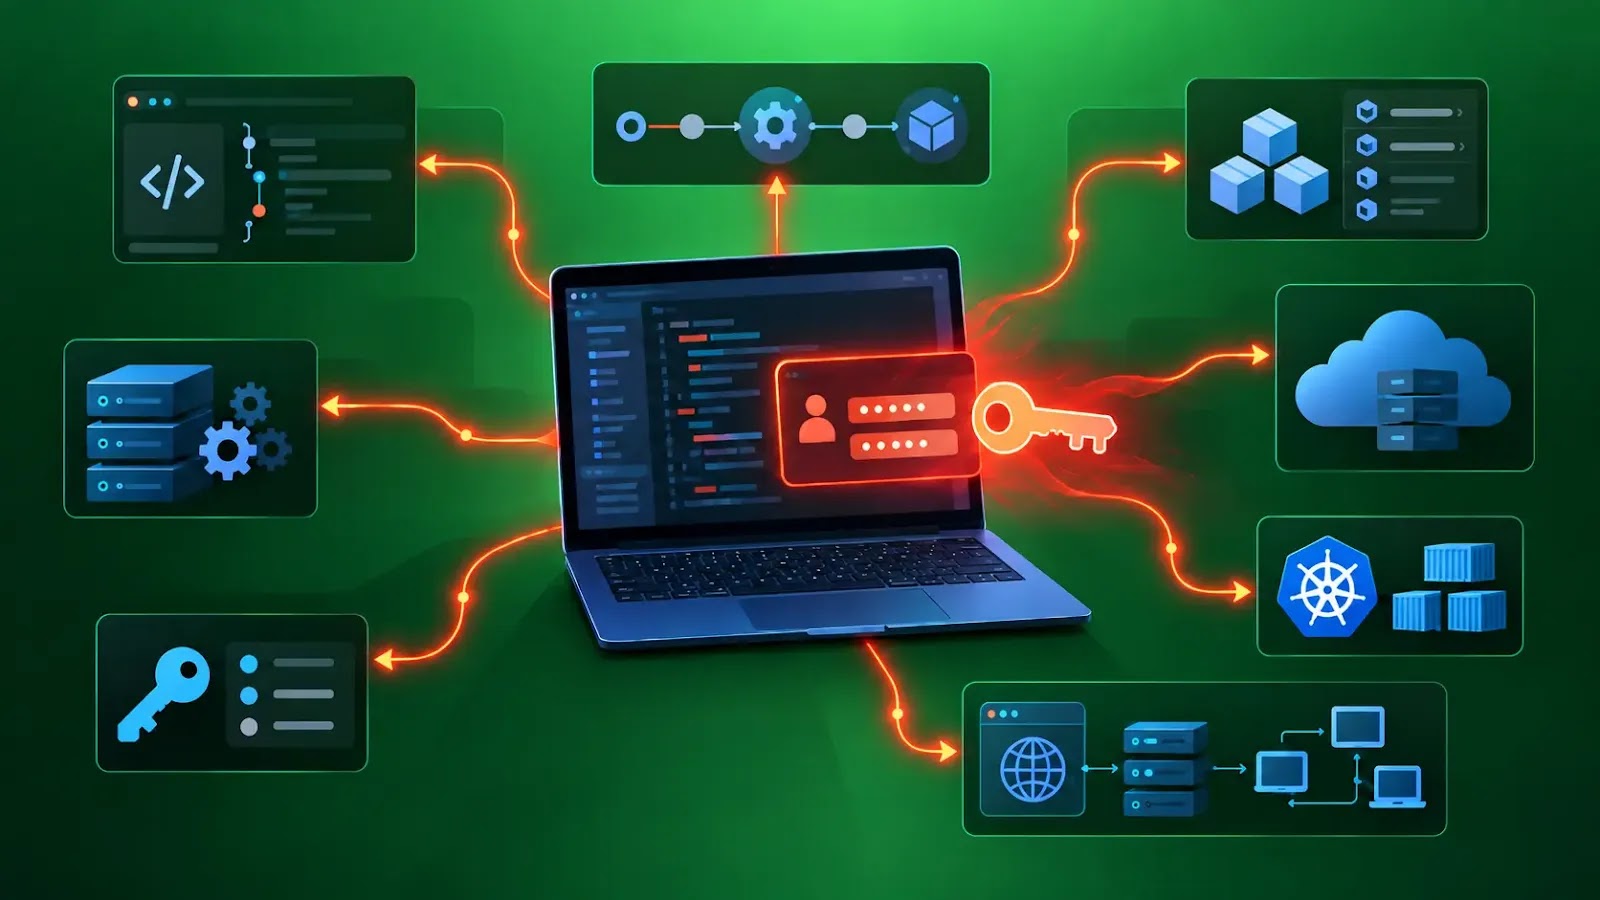

Software supply chain attacks are increasingly evolving into cloud identity breaches, as attackers weaponize trusted packages to steal credentials from developer workstations and CI/CD environments before an application is ever executed.
The result is a dangerous pivot: a routine dependency installation can give threat actors access to cloud accounts, source-code repositories, container platforms, secrets-management systems, and production resources.
The initial compromise often begins with an apparently legitimate package update. A developer installs a dependency, or a build runner retrieves a new version during an automated pipeline.
The build may complete normally, but malicious lifecycle scripts can execute during installation and immediately enumerate environment variables, local configuration files, process memory, cloud metadata services, and token stores.
This makes the developer environment a high-value cloud access point rather than merely a place where code is written.
Microsoft’s analysis of the Mini Shai-Hulud campaign showed how malicious @antv npm packages used a preinstall hook to run an obfuscated payload during npm install.
Workstations and build runners frequently hold AWS access keys, Azure CLI sessions, GCP service-account credentials, GitHub personal access tokens, npm publishing tokens, Kubernetes kubeconfig files, SSH keys, Vault tokens, and deployment secrets.
These credentials may exist in predictable locations such as ~/.aws/credentials, ~/.kube/config, .npmrc, and .netrc, creating a fast path from a compromised dependency to cloud reconnaissance and account takeover.
Qualys Researchers said that, the malware targeted credentials from GitHub Actions, AWS, Kubernetes, HashiCorp Vault, npm, and 1Password environments.
Because the code executed before the installed application was launched, cancelling the installation or avoiding runtime execution did not necessarily prevent credential theft.
Supply Chain Intrusions
The activity illustrates the broader attacker playbook: compromise a maintainer account or publishing credential, inject a malicious install-time payload into a legitimate dependency, steal credentials from downstream environments, and use those credentials to expand the intrusion.
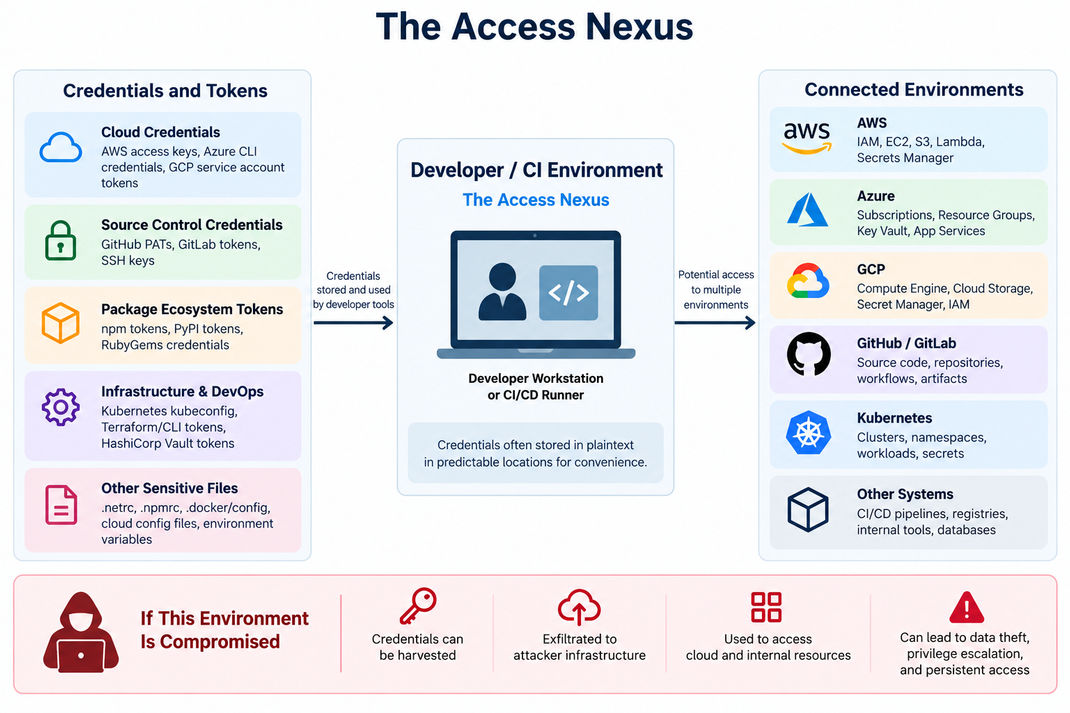
Stolen npm or GitHub tokens can enable further package tampering, while cloud credentials may support discovery of IAM roles, storage buckets, virtual machines, serverless functions, secrets stores, and Kubernetes workloads.
MITRE ATT&CK tracks this behavior under T1195.001: Compromise Software Dependencies and Development Tools, which covers adversaries manipulating dependencies or development tooling before software reaches the final consumer.
In a modern cloud environment, that initial-access technique can quickly overlap with credential theft, valid-account abuse, cloud service discovery, data collection, and persistence.
The key risk is that conventional package-removal procedures are insufficient. Deleting a malicious dependency addresses the initial delivery mechanism but does not invalidate credentials harvested during execution.
If attackers accessed CI/CD secrets, cloud access keys, repository tokens, or metadata-derived workload credentials, they may already have a valid route back into the environment.
Organizations should treat any confirmed install-time package compromise as a potential identity incident.
Incident responders should identify every credential accessible to the affected workstation or runner, revoke and rotate exposed tokens, review cloud audit logs across the full exposure window, examine repository and package-registry activity, and investigate newly created IAM roles, access keys, workflow files, SSH authorized keys.
Preventive controls must reduce both execution opportunities and credential impact. CI pipelines should disable unnecessary lifecycle scripts, enforce dependency lockfile integrity, use approved private registries, and pin known-good versions rather than automatically accepting new releases.
Where compatible with build requirements, npm installations should use --ignore-scripts or equivalent controls to block untrusted preinstall and postinstall execution.
Cloud credentials should also be short-lived, narrowly scoped, and workload-bound. Organizations should replace long-lived stored keys with OIDC-based federation where possible, ensure build jobs do not retain deployment-level privileges, and protect cloud instance metadata services.
AWS environments, for example, should enforce IMDSv2 to make simple metadata credential harvesting substantially harder.
Qualys TotalCloud can help security teams connect identity, posture, workload, inventory, and sensitive-data signals across AWS, Azure, and GCP.
Its capabilities include identifying exposed secrets, visualizing risky permission paths, and prioritizing toxic cloud access conditions through TruRisk-driven context.
Cut every SOC alert investigation by 21 min. Power your SOC with instant IOC context for immediate response: Integrate TI Lookup in your SOC