

A group of security researchers uncovered a 12 Bluetooth based vulnerabilities dubbed “SweynTooth” in BLE software development kits of seven major system-on-a-chip (SoC) vendors.
BLE ( Bluetooth Low Energy) a technology developed for wireless communication with a set of many standardized protocols that provide remote connectivity and also specifically handles the battery life of the device different power consumption and usage capabilities.
We have recently reported another critical Bluetooth vulnerability discovered in the Android Bluetooth system that allows remote attackers to silently execute arbitrary code remotely and take the complete device control.
Now researchers from Singapore University of Technology and Design reported the new set of vulnerabilities in BLE SoC implementations allow attackers to perform deadlocks, crashes and buffer overflow or completely bypass security within the radio range and the different circumstances.
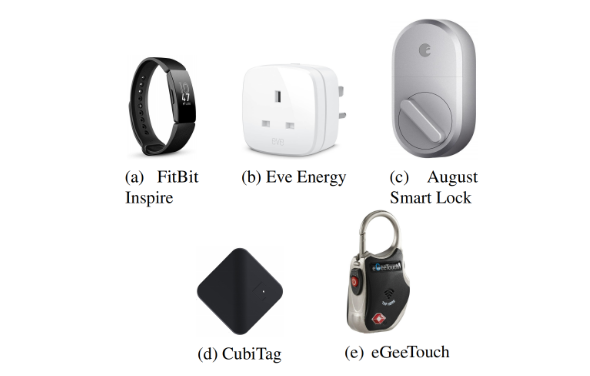
Also, SweynTooth vulnerabilities affected various IoT products in appliances such as smart-homes, wearables and environmental tracking or sensing, medical and logistics products.
Vulnerable BLE SDKs sold by seven vendors of the following:
- Texas Instruments
- NXP
- Cypress
- Dialog Semiconductors
- Microchip
- STMicroelectronics
- Telink Semiconductor.
Type of Vulnerabilities
There are 3 types of major SweynTooth flaw identified in this research and each vulnerability impact the devices in different ways,
Crash :
Six Bluetooth vulnerabilities are addressed that lead to crash a device once the attacker triggers the vulnerabilities due to some incorrect code behavior or memory corruption.
- Link Layer Length Overflow CVE-2019-16336, CVE-2019-17519
- Truncated L2CAP CVE-2019-17517
- Silent Length Overflow CVE-2019-17518
- Public Key Crash CVE-2019-17520
- Invalid L2CAP Fragment CVE-2019-19195
- Key Size Overflow CVE-2019-19196
According to the finding report, “when a buffer overflow on BLE reception buffer occurs. When a device crash occurs, they usually restart. However, such a restart capability depends on whether a correct hard fault handling mechanism was implemented in the product that uses the vulnerable BLE SoC.”
This vulnerability affected the vendors including Cypress, NXP, Dialog Semiconductors, Texas Instruments, Microchip, Telink Semiconductor.
Deadlock:
There are 3 vulnerabilities related to Deadlock type that affect the availability of the BLE connection without causing a hard fault or memory corruption.
- LLID Deadlock CVE-2019-17061 , CVE-2019-17060
- Sequential ATT Deadlock CVE-2019-19192
- Invalid Connection Request CVE-2019-19192
Researchers explain that they usually occurred due to some improper synchronization between user code and the SDK firmware distributed by the SoC vendor, leaving the user code being stuck at some point.
There are 3 Vendors affected by these vulnerabilities: Cypress, NXP, STMicroelectronics.
3. Security Bypass:
Security bypass type Bluetooth vulnerability in SweynTooth consider as a “Critical” one and the vulnerability allows attackers in radio range to bypass the latest secure pairing mode of BLE.
Successfully exploit this vulnerability allow attack to perform an arbitrary read or write access to the device’s functions remotely.
Attackers also perform smart luggage lock that can be remotely locked or unlocked through a smartphone app.
This Zero LTK Installation security bypass Bluetooth vulnerability ( CVE-2019-19194 ) affected only Zero LTK Installation.
You can also read the detailed and in-depth technical details here.







 vendors.)